
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 42
- Trending now
- 5
- Breaking
- Live
Cloudflare Warns of AI-Powered Hacking Surge, Introduces Six-Pillar Modern Security Model
Cloudflare reports a surge in autonomous AI penetration-testing frameworks, including ARTEX forks, and recommends six security measures to help organisations defend against automated reconnaissance, exploitation and credential-based attacks.
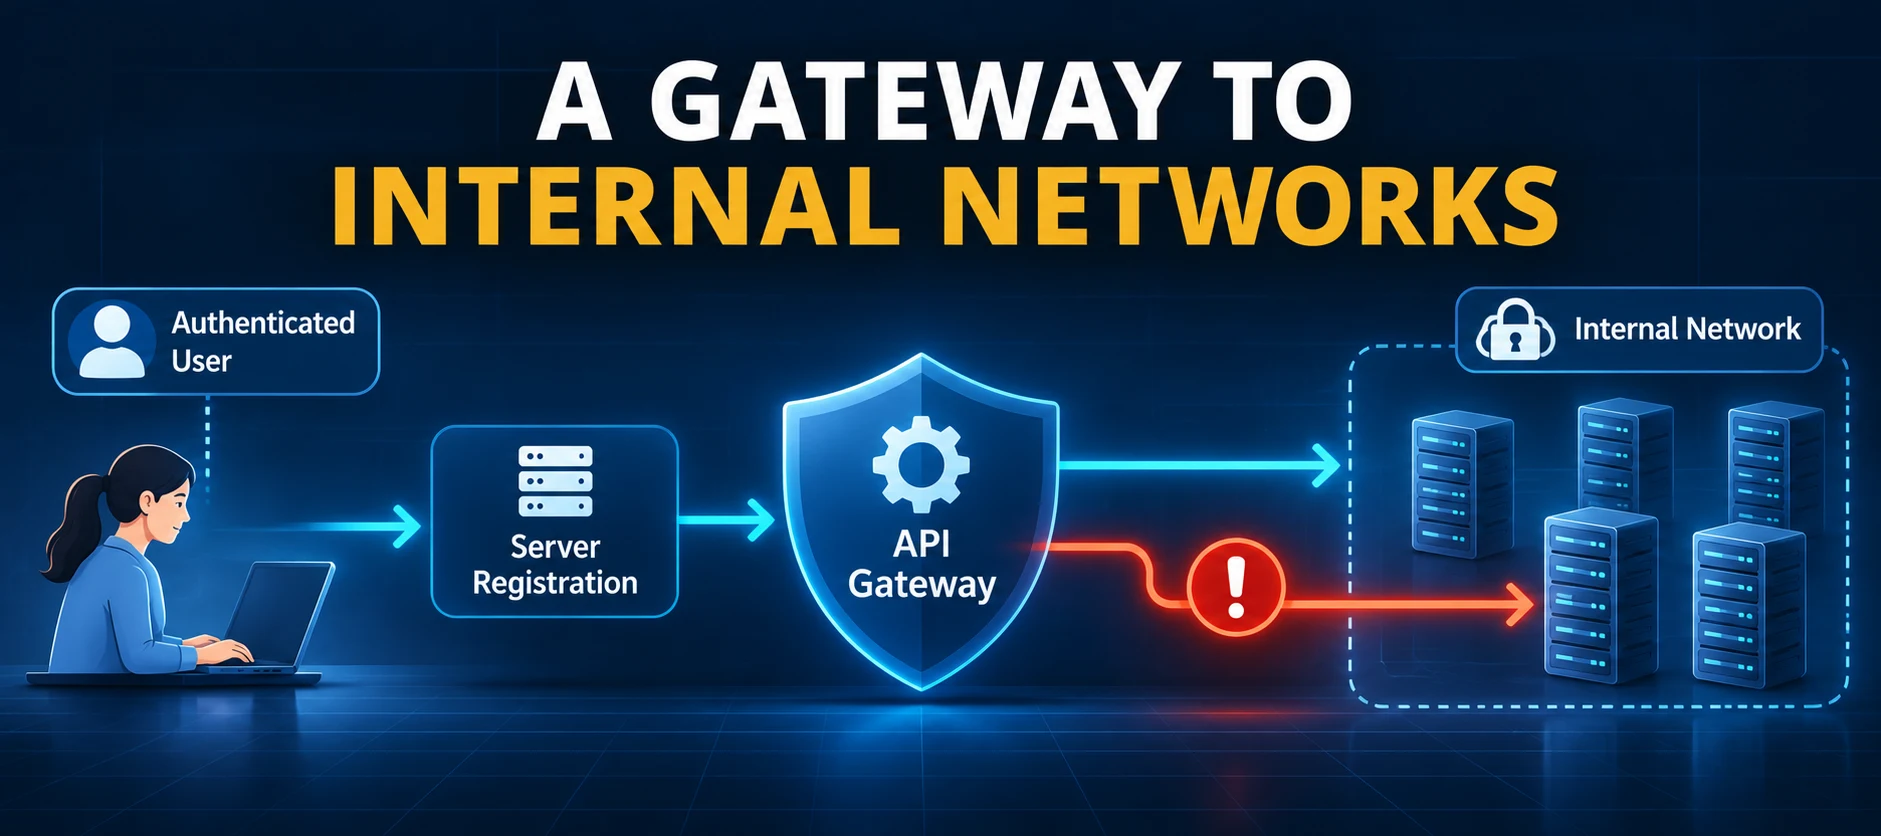
AWS Fixes SSRF Flaw in MCP Gateway Registry That Could Expose Internal Services
AWS has disclosed CVE-2026-125926, an SSRF vulnerability in mcp-gateway-registry that could let authorized users route gateway requests to internal network services. Version 1.35.0 contains the fix.
 Trending
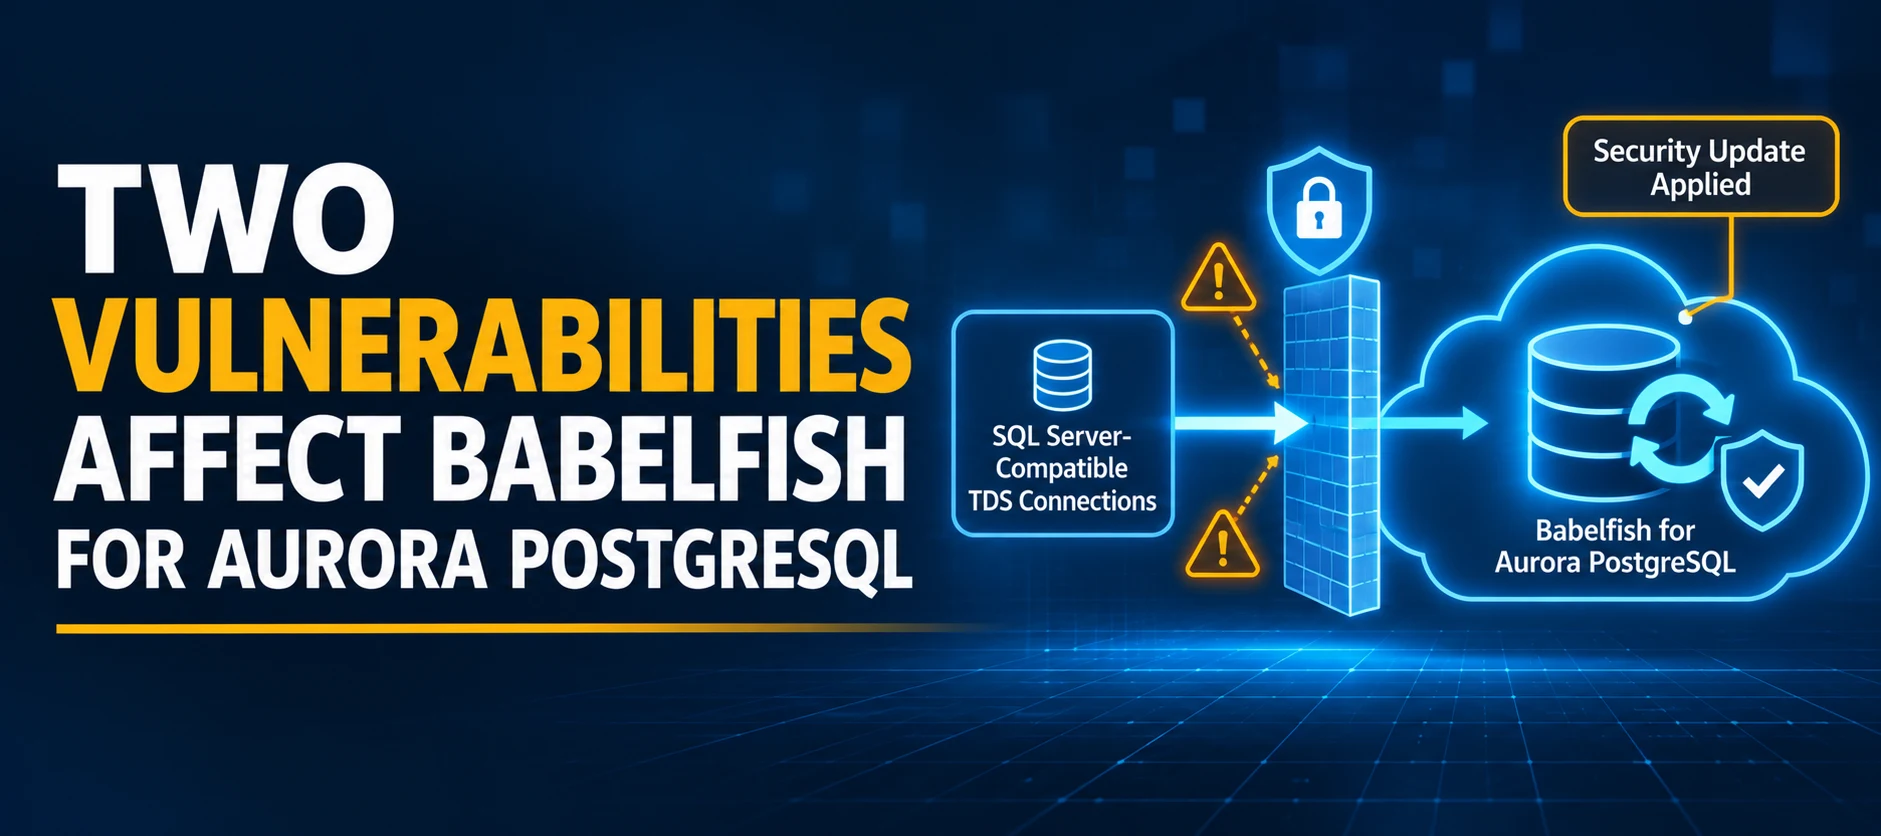
AWS Warns of Two Babelfish Vulnerabilities Affecting Aurora PostgreSQL
AWS has disclosed two memory-safety vulnerabilities in Babelfish for Aurora PostgreSQL. CVE-2026-119923 affects unauthenticated TDS handshakes, while CVE-2026-119924 could expose adjacent process memory or cause denial of service.
 Trending
AWS Warns of APT Vulnerability Affecting Ubuntu and Debian Systems
AWS warns of CVE-2026-109518, an APT package manager vulnerability affecting Ubuntu and Debian systems. The flaw could allow a network-positioned attacker to bypass package verification and execute code with elevated privileges.
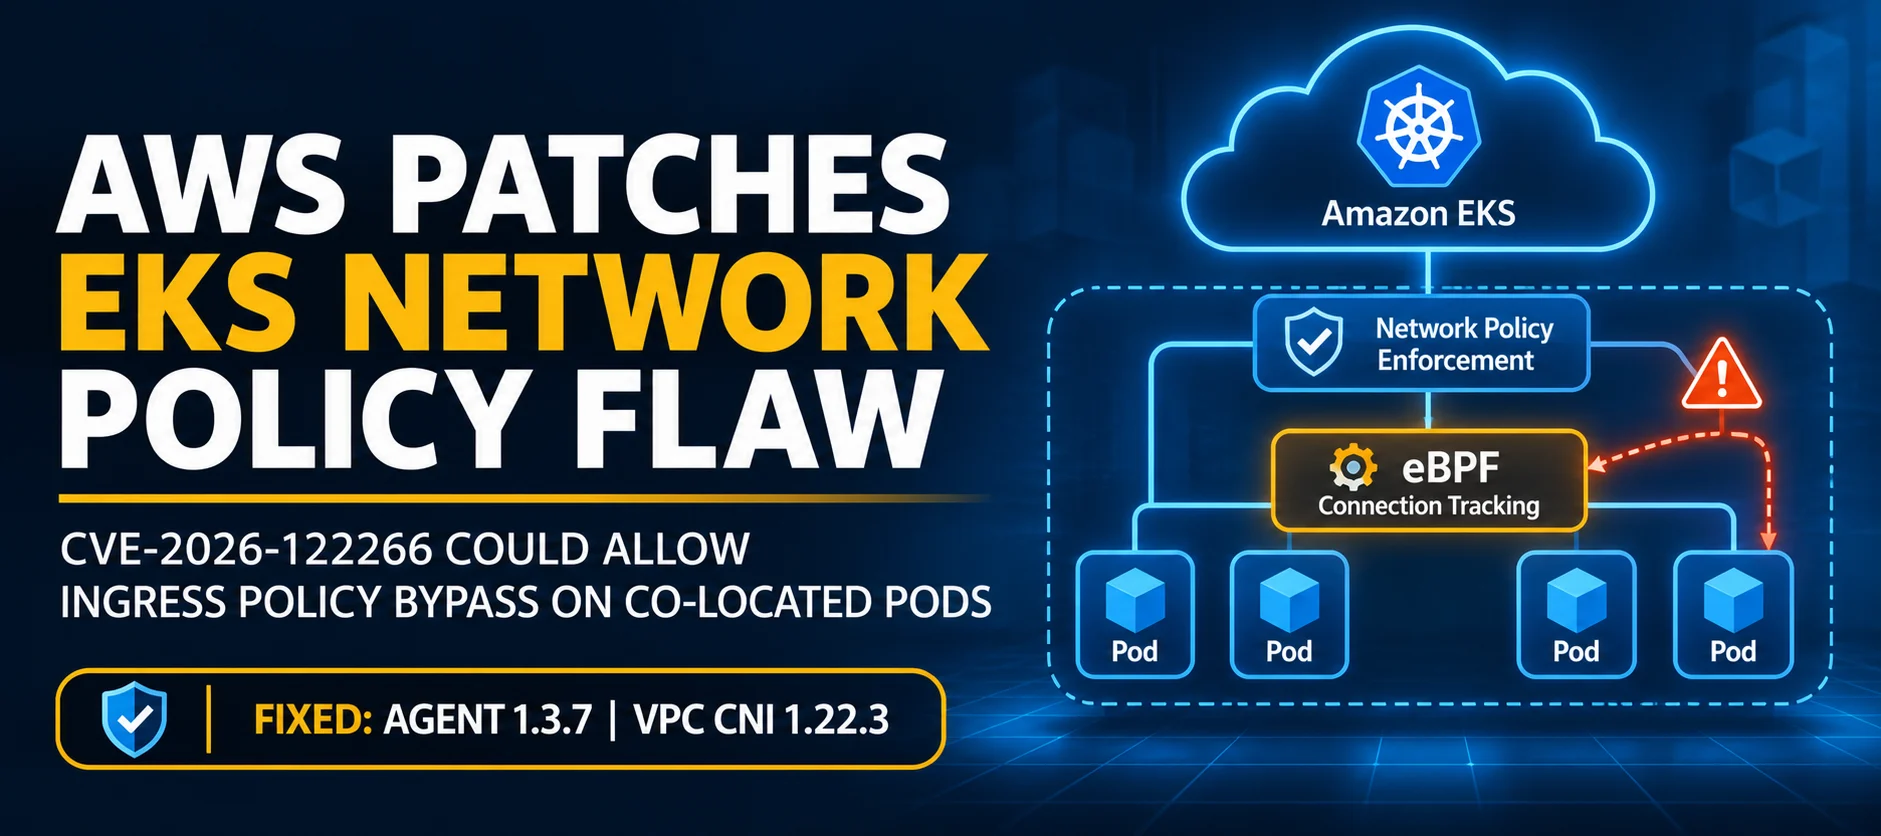
AWS Fixes EKS Network Policy Flaw That Could Allow Ingress Restrictions to Be Bypassed
AWS has addressed CVE-2026-122266 in the Amazon EKS Network Policy Agent. The flaw could allow an authenticated adjacent user to bypass NetworkPolicy ingress enforcement on co-located pods.
 Trending
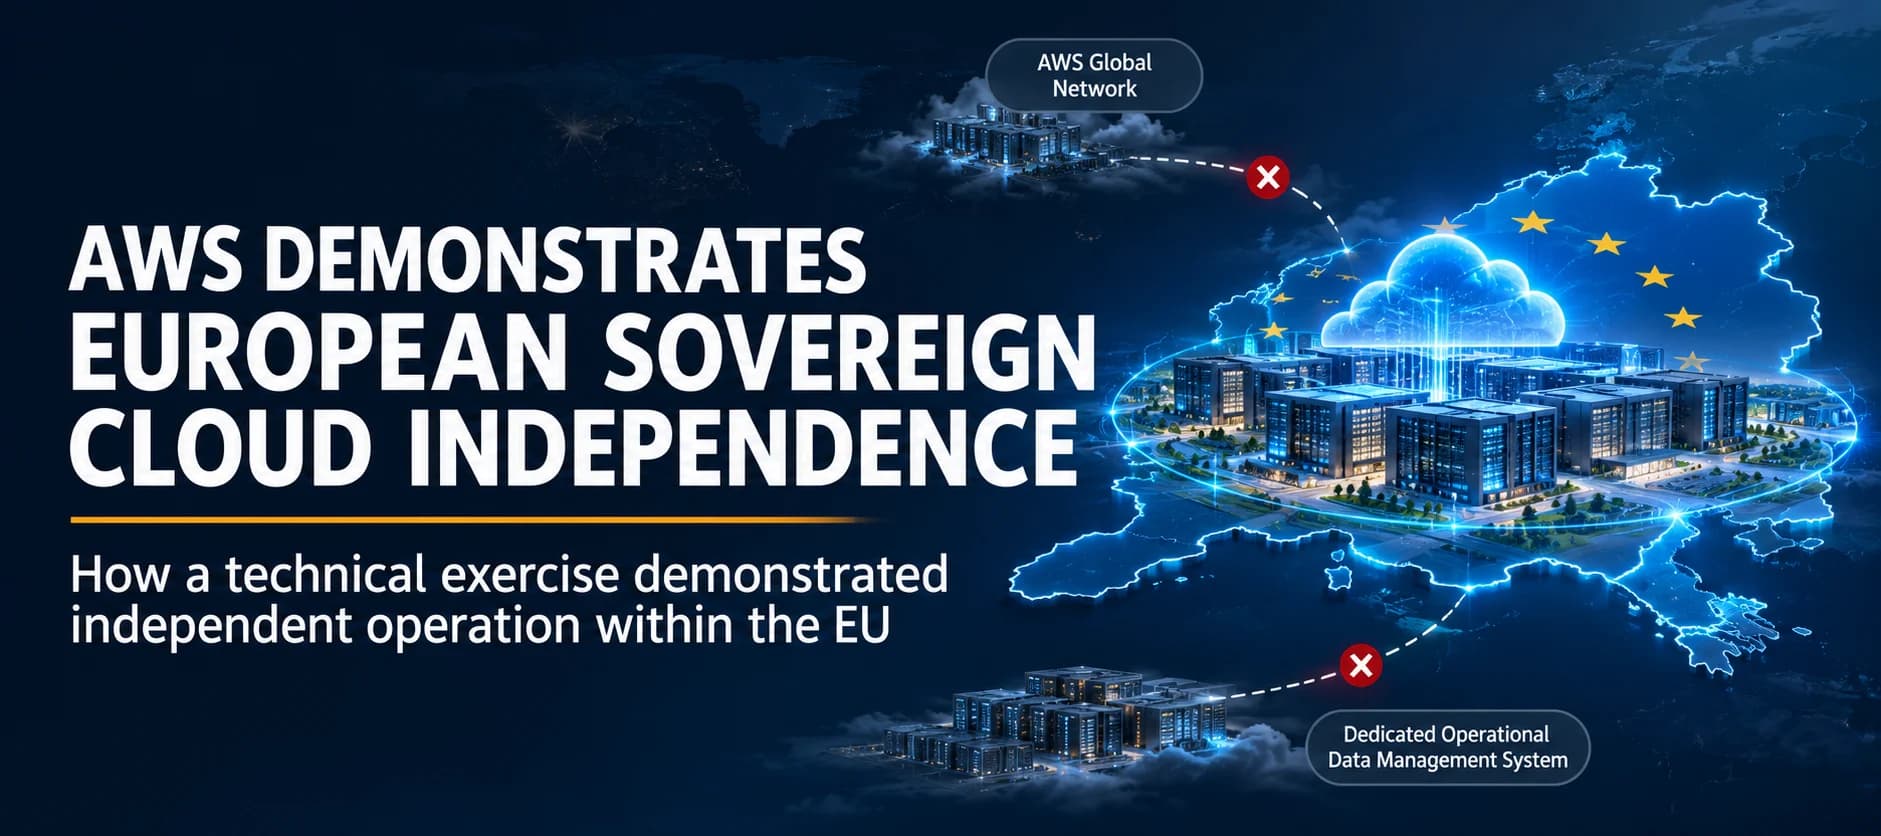
AWS Demonstrates European Sovereign Cloud Can Operate Independently Within the EU
AWS says its European Sovereign Cloud continued running during an exercise that switched off two global systems, demonstrating that its workloads and customer data remained accessible without relying on infrastructure outside the EU.
 Trending
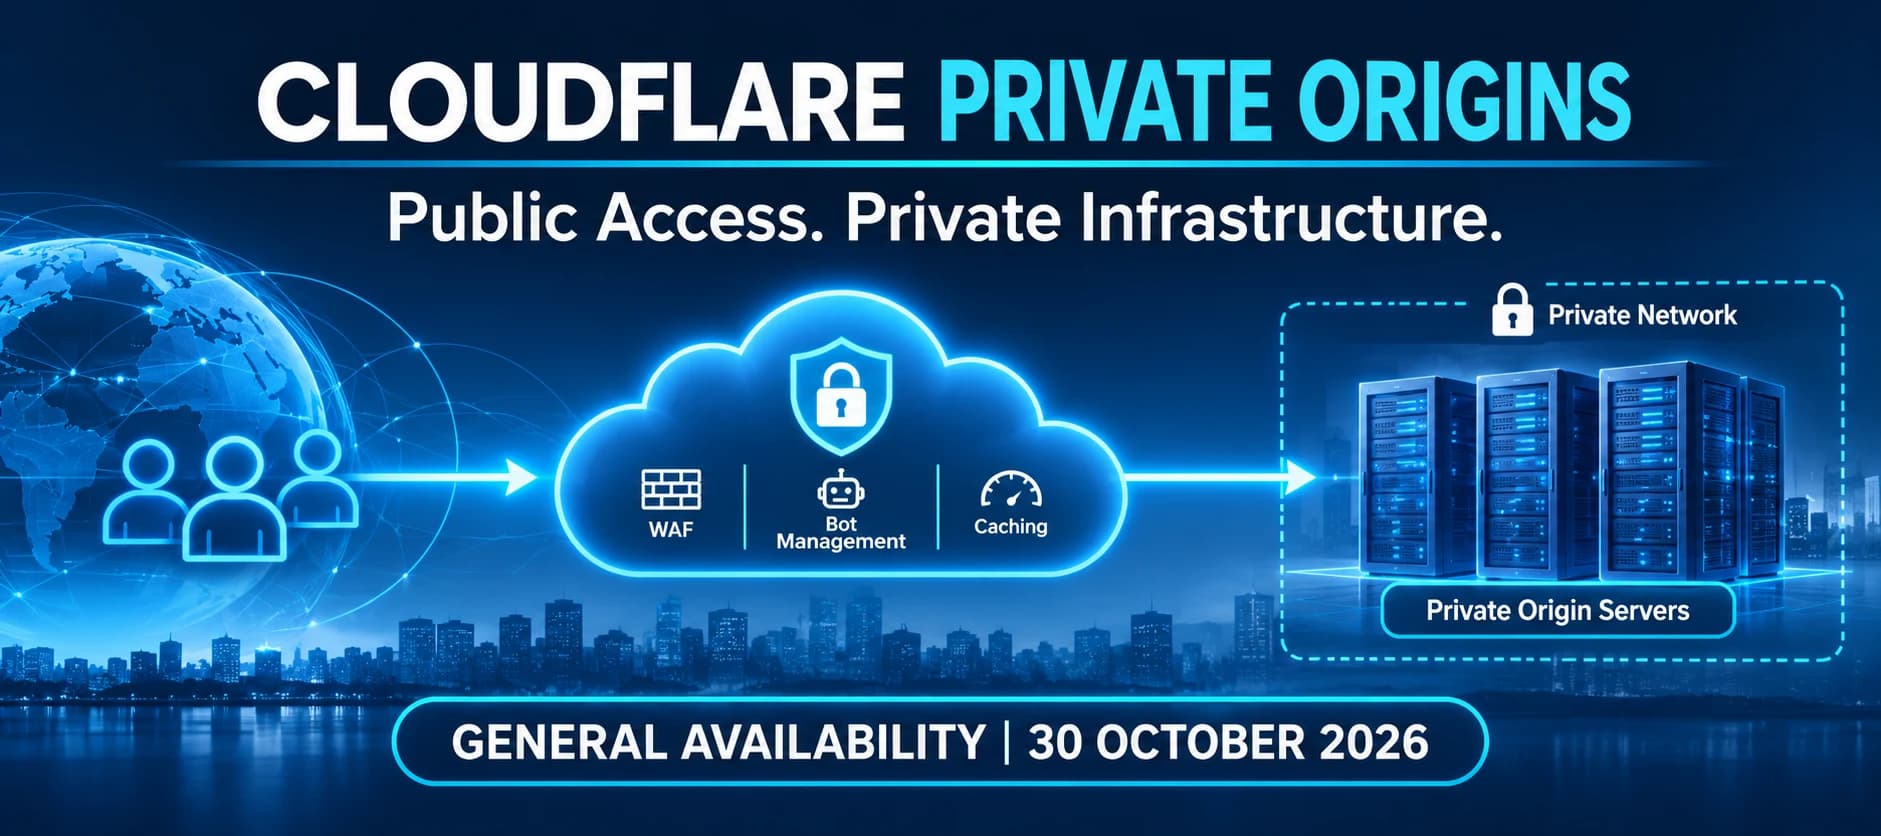
Cloudflare Makes Private Origins Generally Available, Bringing Enterprise Security to Private Infrastructure
Cloudflare has made Private Origins generally available, allowing organisations to route public traffic to private origin servers while retaining WAF, bot management, caching and other application security controls without exposing origin IPs.
 Trending
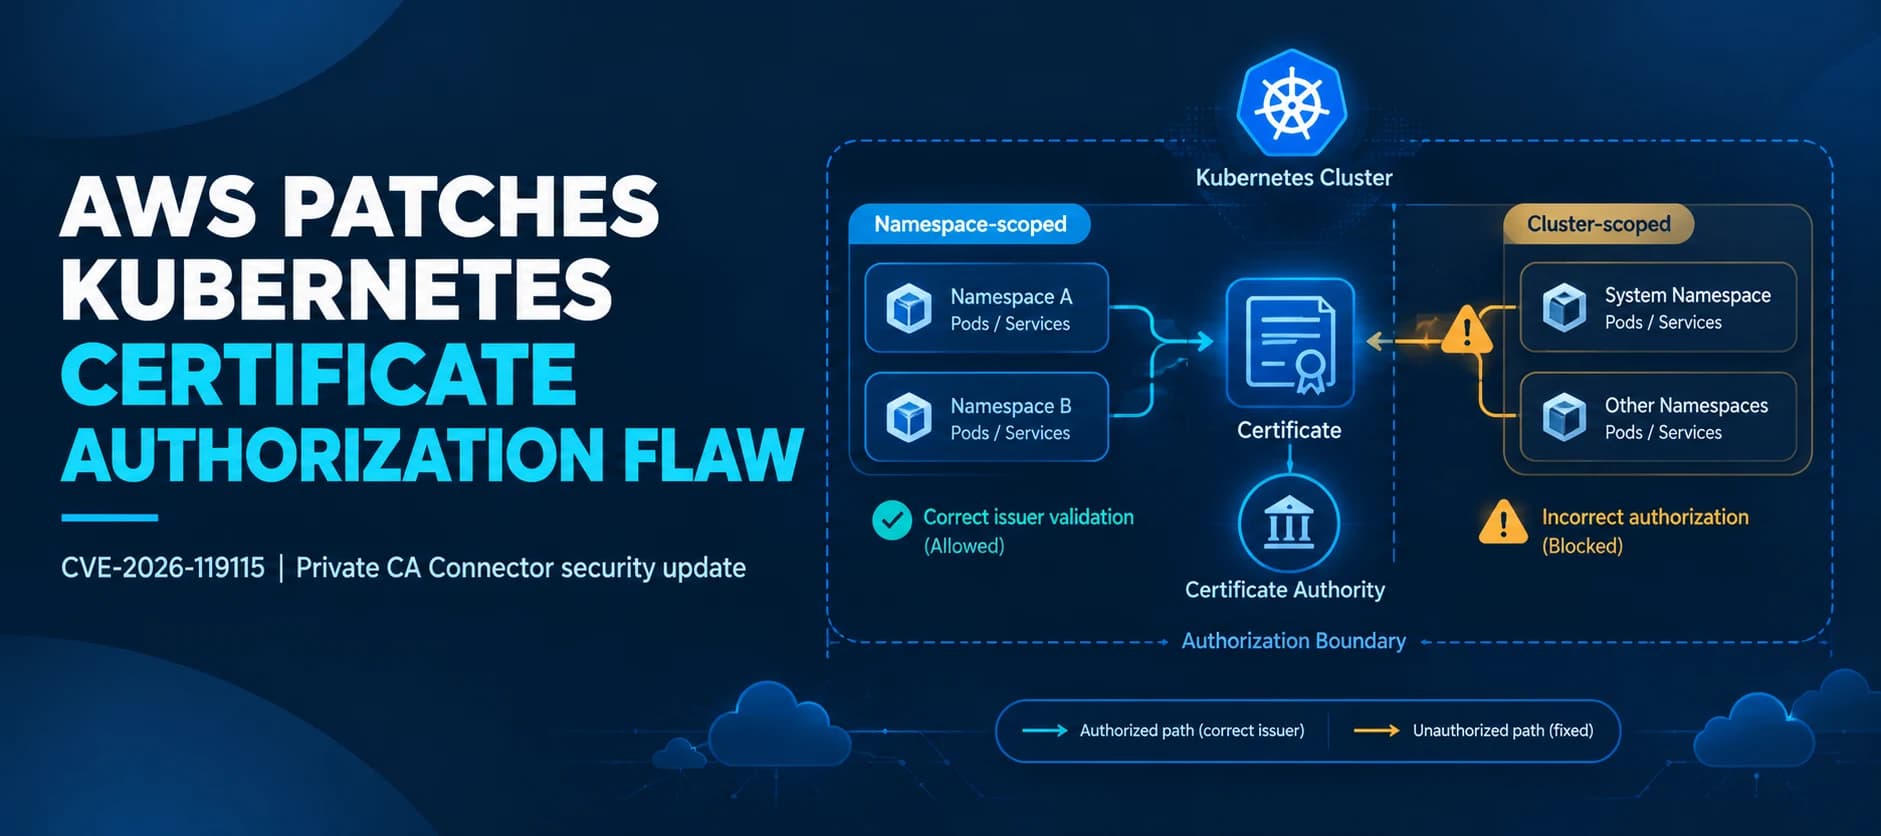
AWS Fixes Certificate Authorization Flaw in Private CA Connector for Kubernetes
AWS has fixed CVE-2026-119115, an authorization flaw that could let authenticated users obtain certificates from unauthorized cluster-scoped issuers. Organizations should upgrade and audit issuer references before deployment.
 Trending
AWS Warns of Brotli Vulnerability Enabling Code Execution and Memory Disclosure
AWS has issued an important security bulletin for CVE-2026-111497, a Brotli decompression vulnerability that could enable code execution or memory disclosure. The advisory outlines patching and mitigation steps for multiple AWS services and customer-managed environments.
 Trending
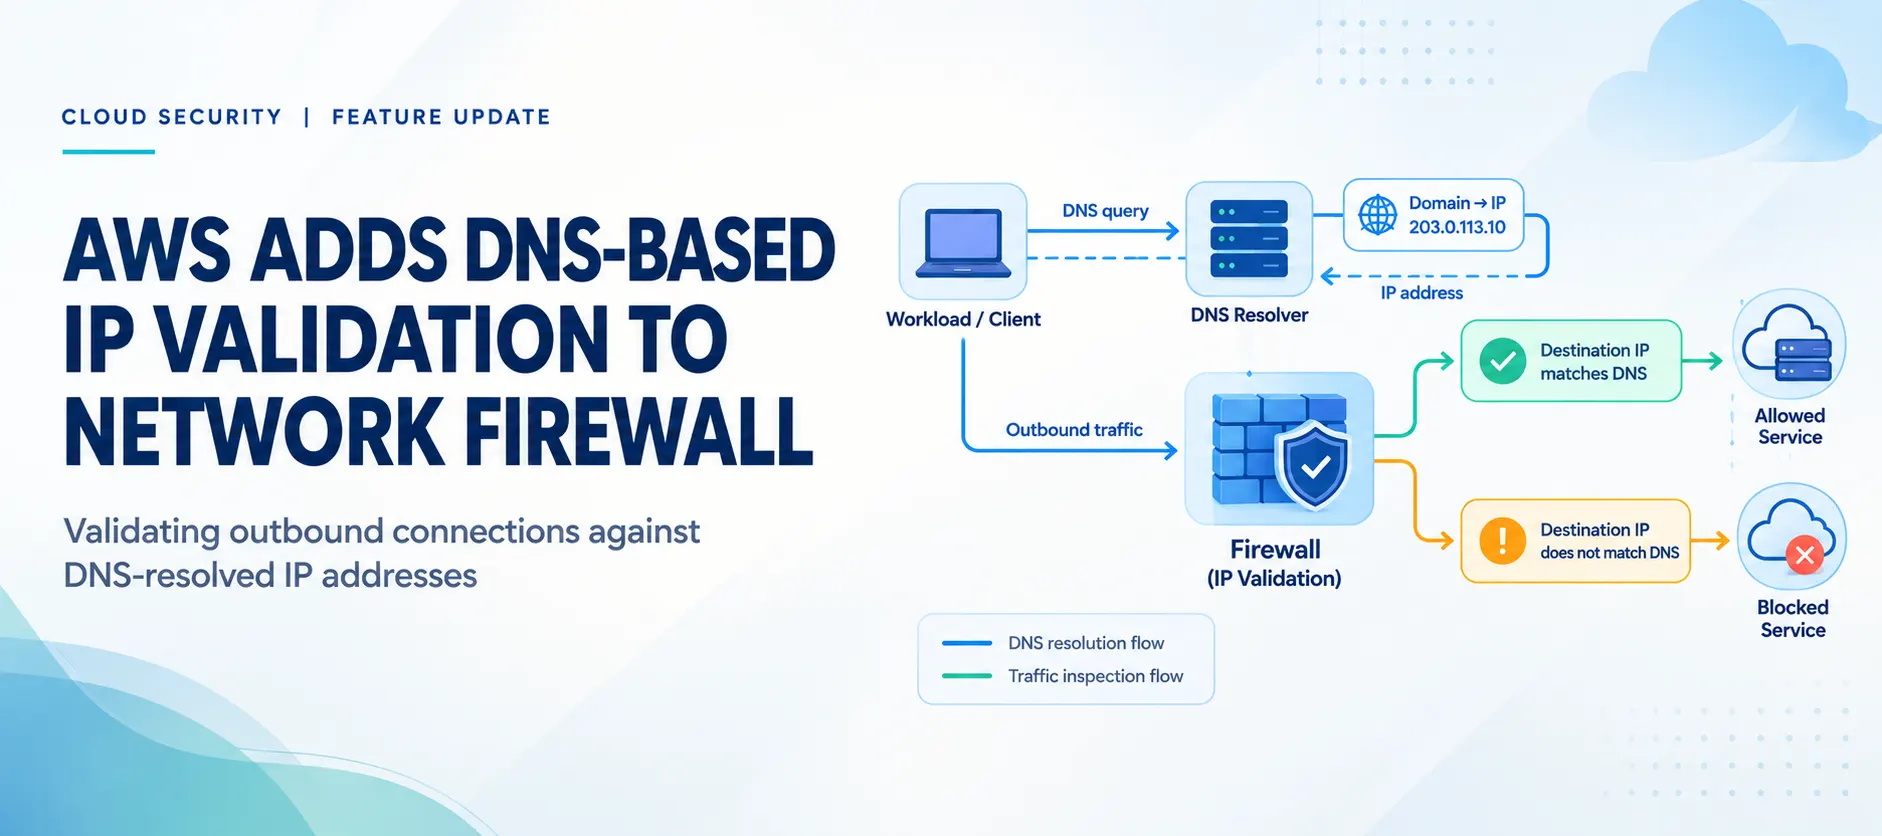
AWS Adds DNS-Based IP Validation to Network Firewall
AWS introduces Route 53 Resolved IP Validation for Network Firewall, enabling domain-based filtering for non-web traffic and helping prevent SNI spoofing without requiring TLS inspection.
 Trending
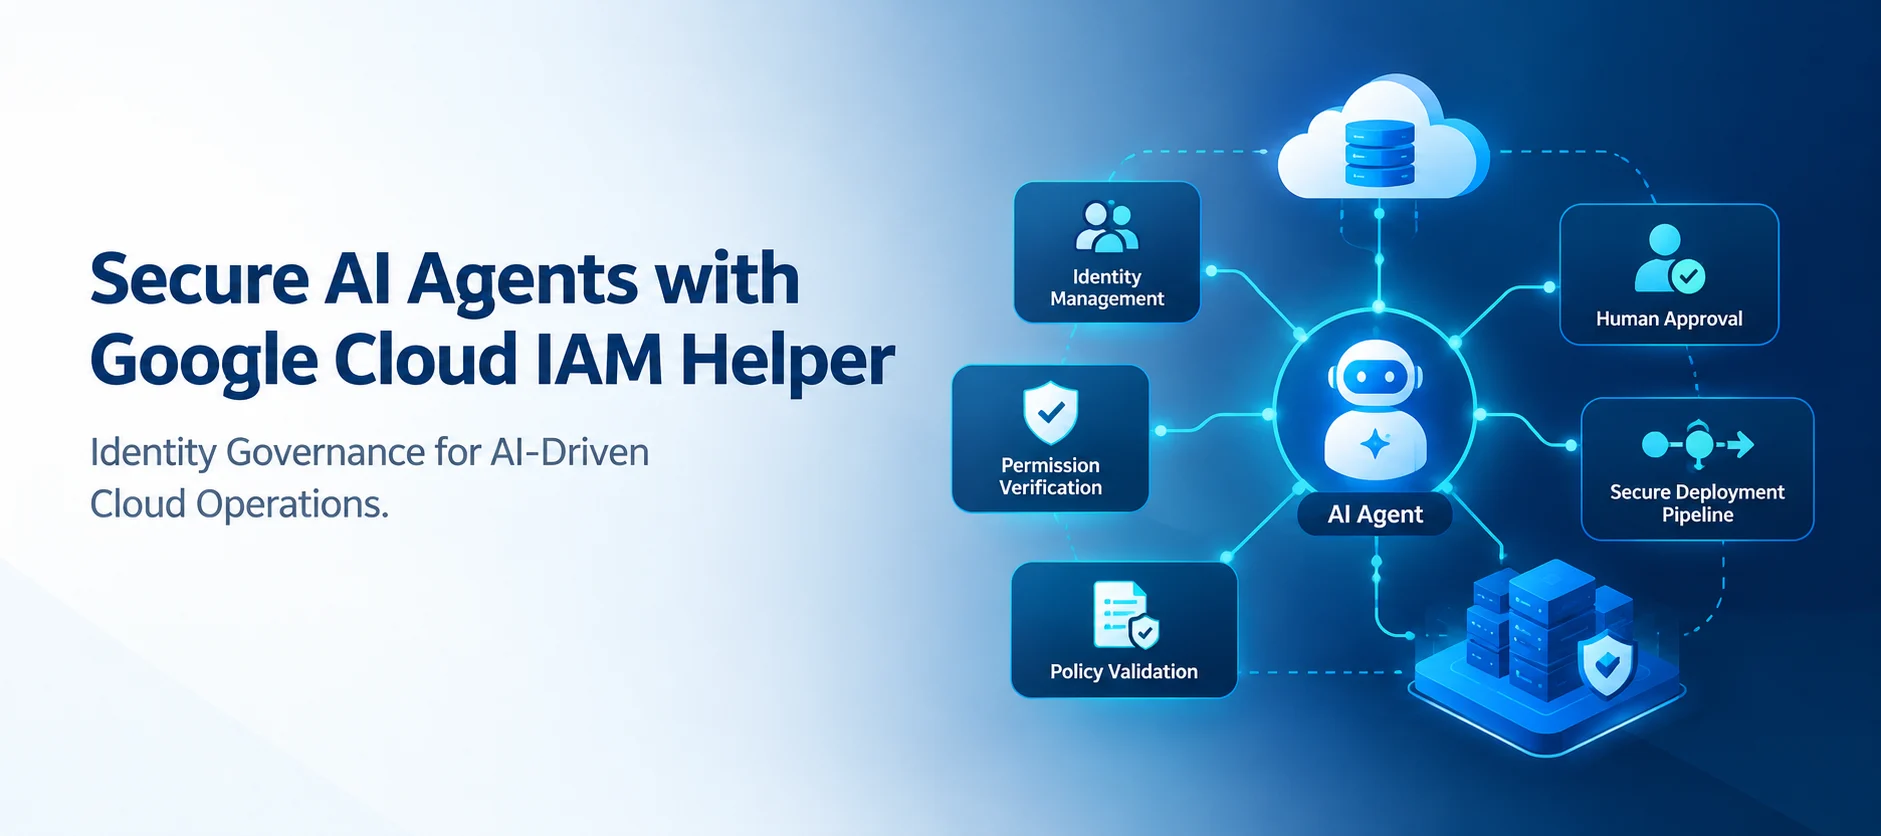
Google Cloud Introduces IAM Helper to Secure AI Agent Access
Google Cloud introduces IAM Helper Agent Skills and MCP tools to streamline identity management, troubleshoot permissions, simulate policy changes and support human-approved access controls for AI-driven workflows.
 Trending
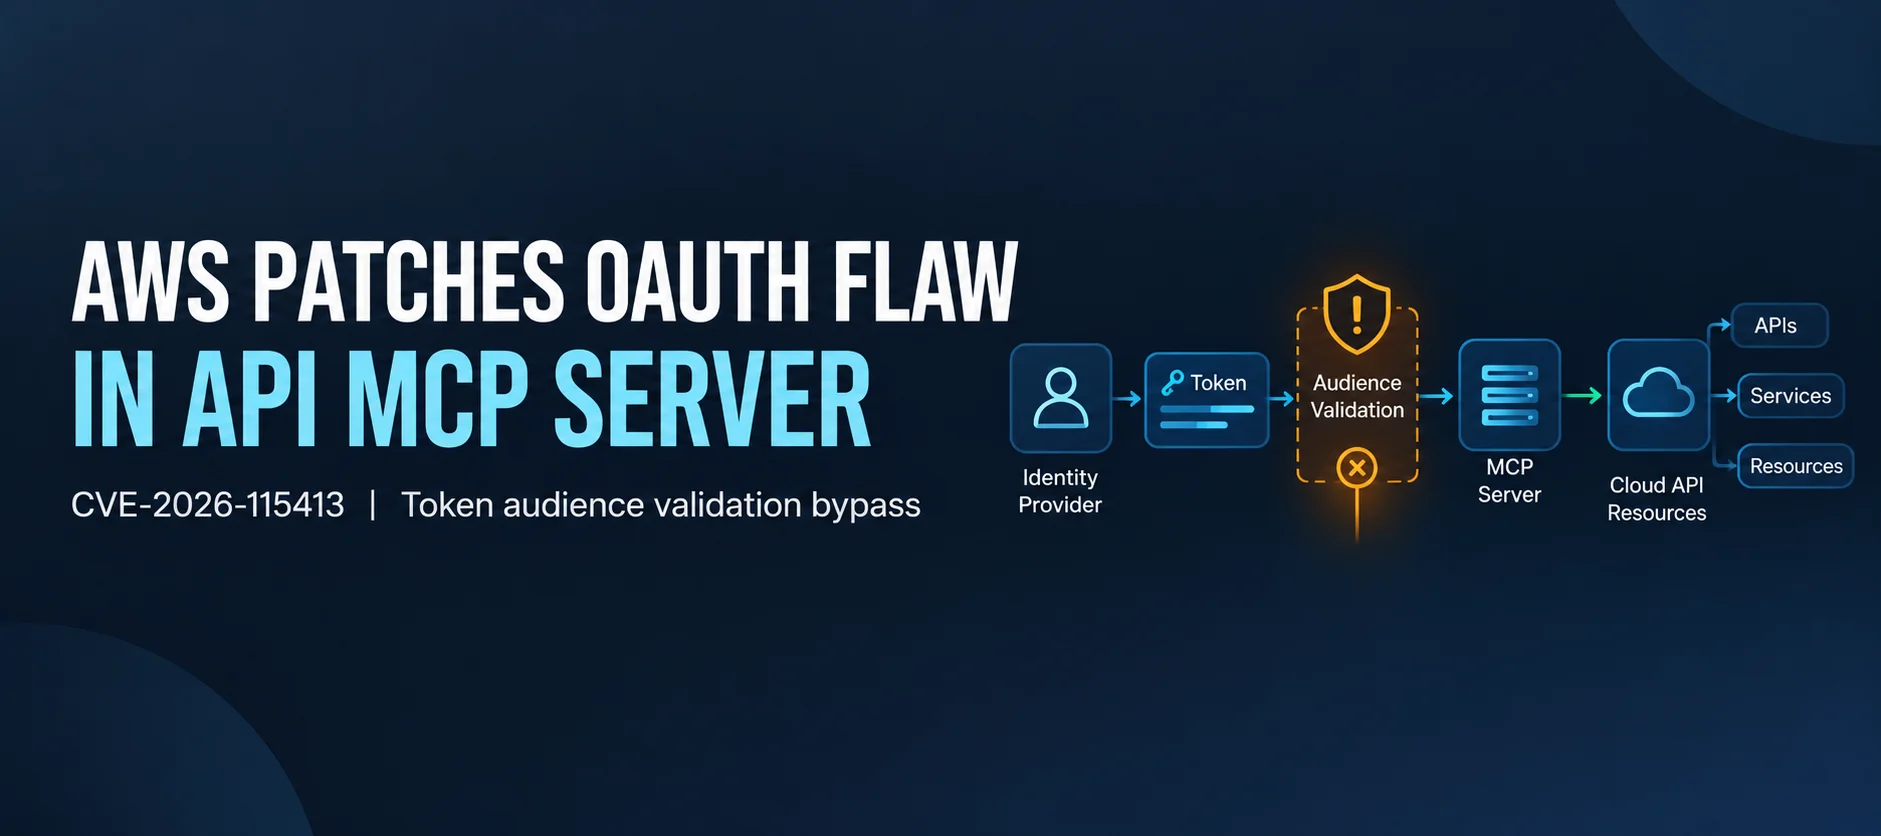
AWS Fixes OAuth Token Validation Bypass in API MCP Server
AWS has patched CVE-2026-115413, an OAuth token audience validation bypass affecting AWS API MCP Server versions 1.3.0 to before 1.6.0. The flaw could allow a token issued to another application in the same tenant to authorize AWS API calls.
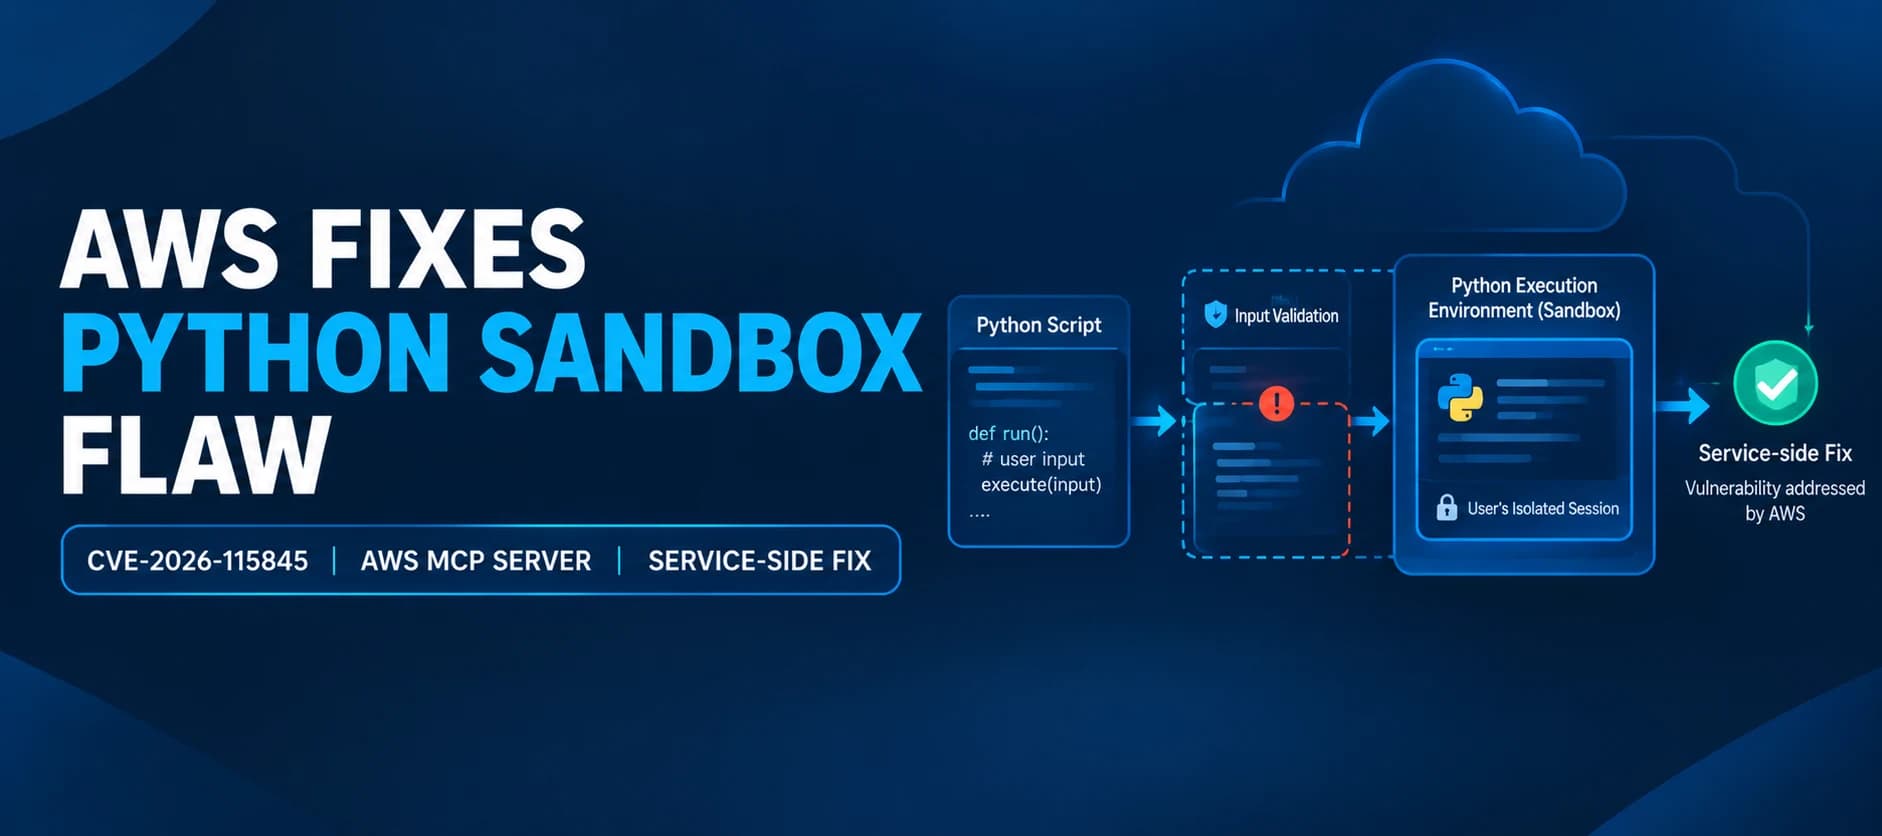
AWS Fixes Critical Python Sandbox Vulnerability in AWS MCP Server
AWS has fixed CVE-2026-115845 in the Python sandbox validator of AWS MCP Server. The flaw could allow an authenticated remote user to execute arbitrary code within their own isolated session environment.