
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 371
- Trending now
- 5
- Breaking
- Live
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
 Trending
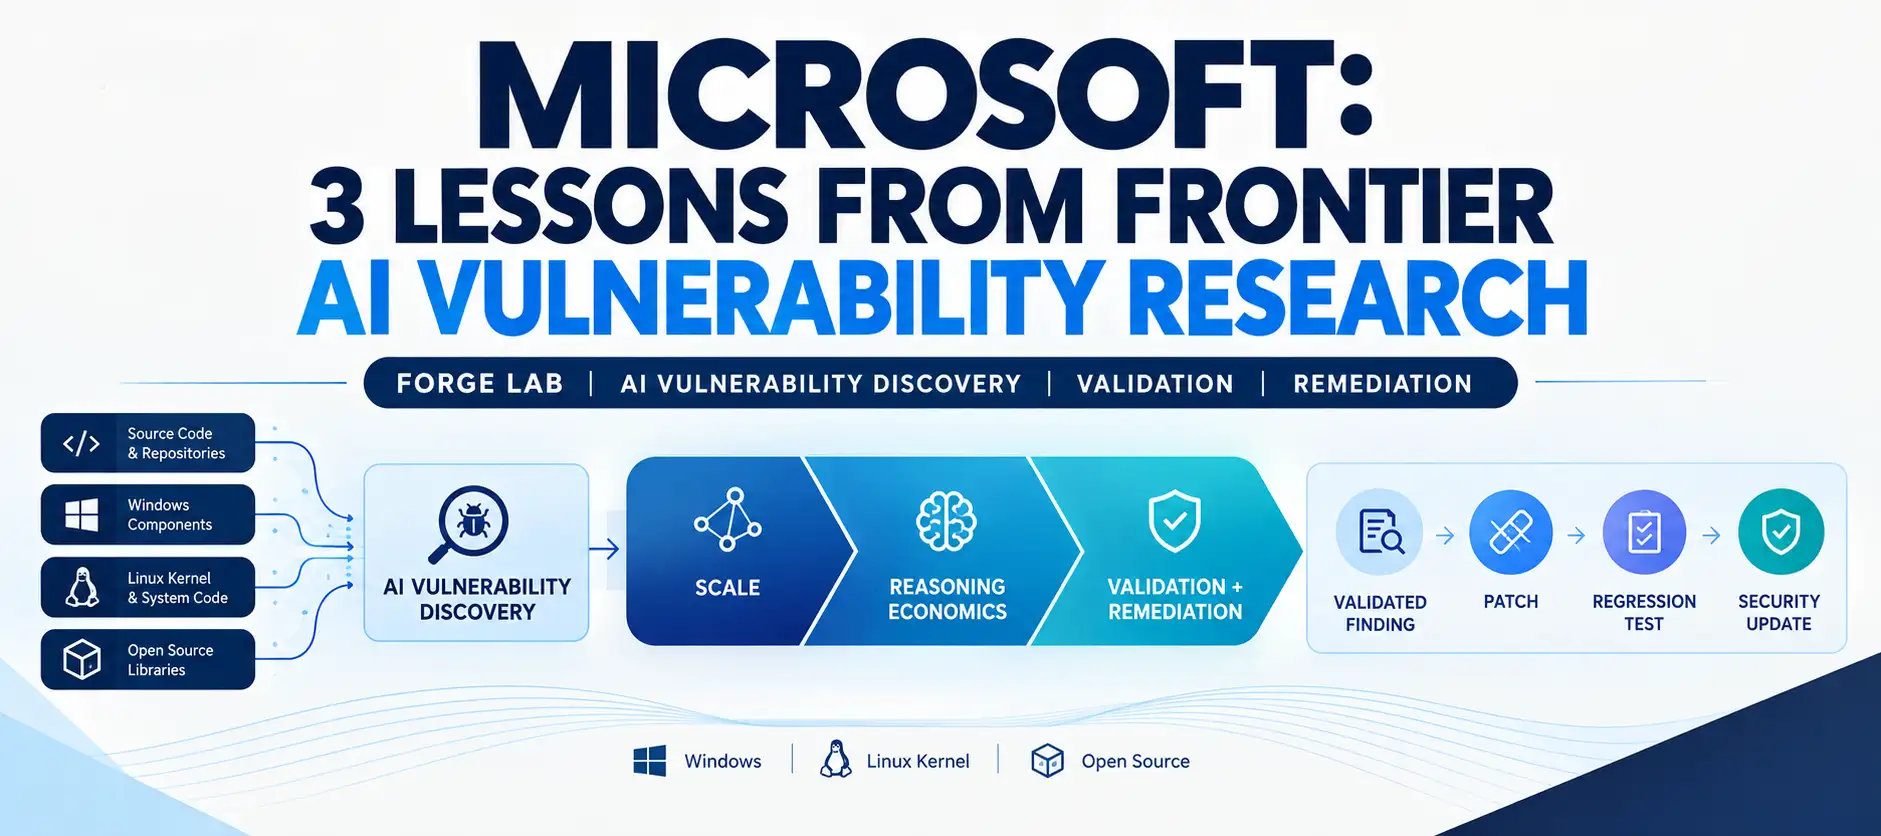
Microsoft Reveals 3 Lessons From AI-Powered Vulnerability Research
Microsoft's FORGE Lab says AI-driven vulnerability discovery is reaching meaningful scale, but validation, remediation, human review and engineering capacity are becoming critical constraints.
 Trending
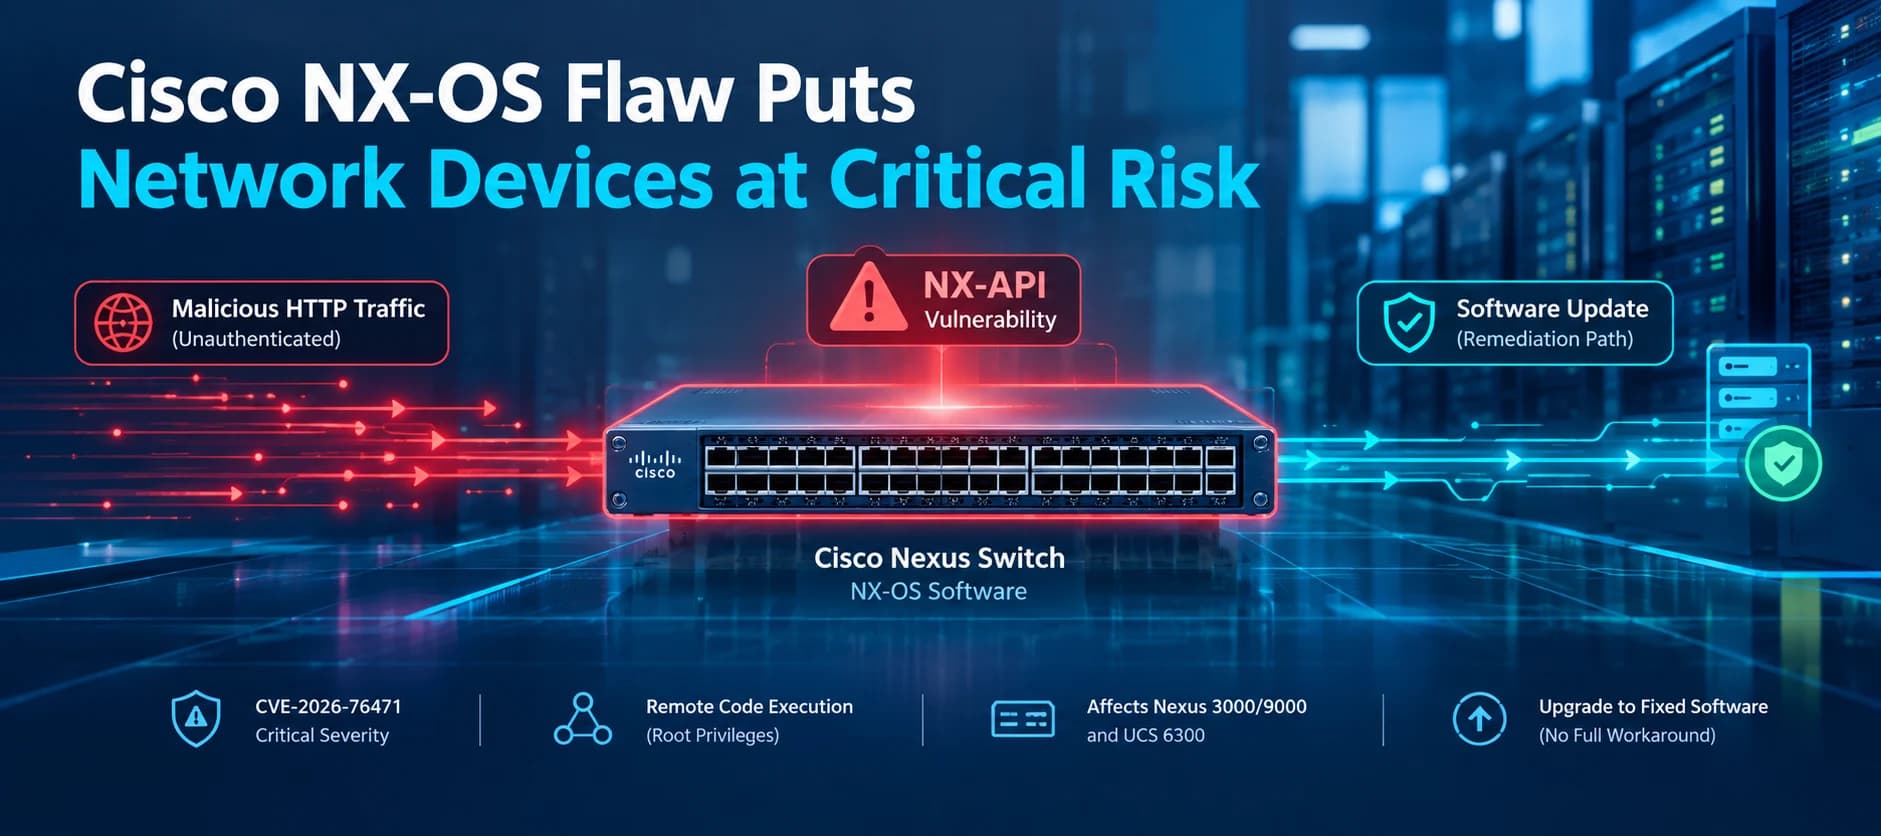
Cisco NX-OS NX-API Vulnerability Enables Critical Remote Code Execution
Cisco has disclosed a critical NX-OS NX-API vulnerability, CVE-2026-76471, that could allow unauthenticated remote code execution with root privileges on affected devices. Cisco recommends upgrading to fixed software.
 Trending
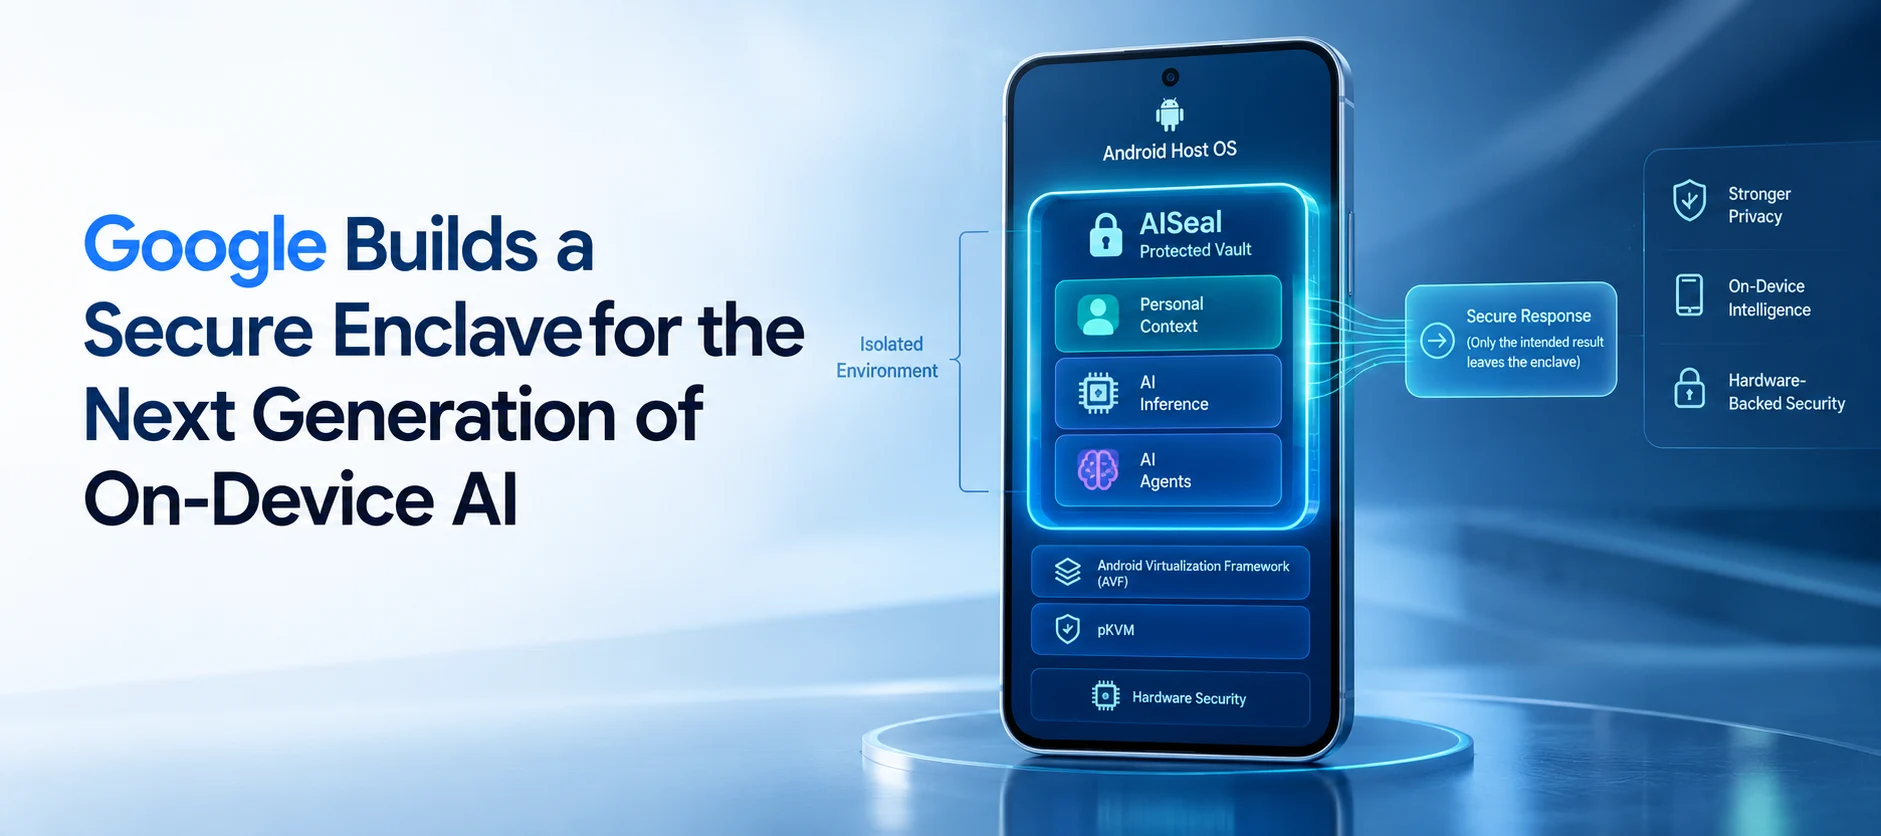
Google Introduces AISeal, a Hardware-Isolated Enclave for More Private On-Device AI on Android
Google has introduced AISeal, a hardware-isolated secure vault for personalized on-device AI. Built on Android virtualization and pKVM, it is designed to keep sensitive personal context isolated even if the host operating system is compromised.
 Trending
Cloudflare Builds Evidence-Grounded Agentic Security Operations Harness
Cloudflare has built a multi-agent security operations harness that combines deterministic evidence collection with specialist AI agents to investigate alerts, correlate findings and provide evidence-backed recommendations to Managed Defense Analysts.
 Trending
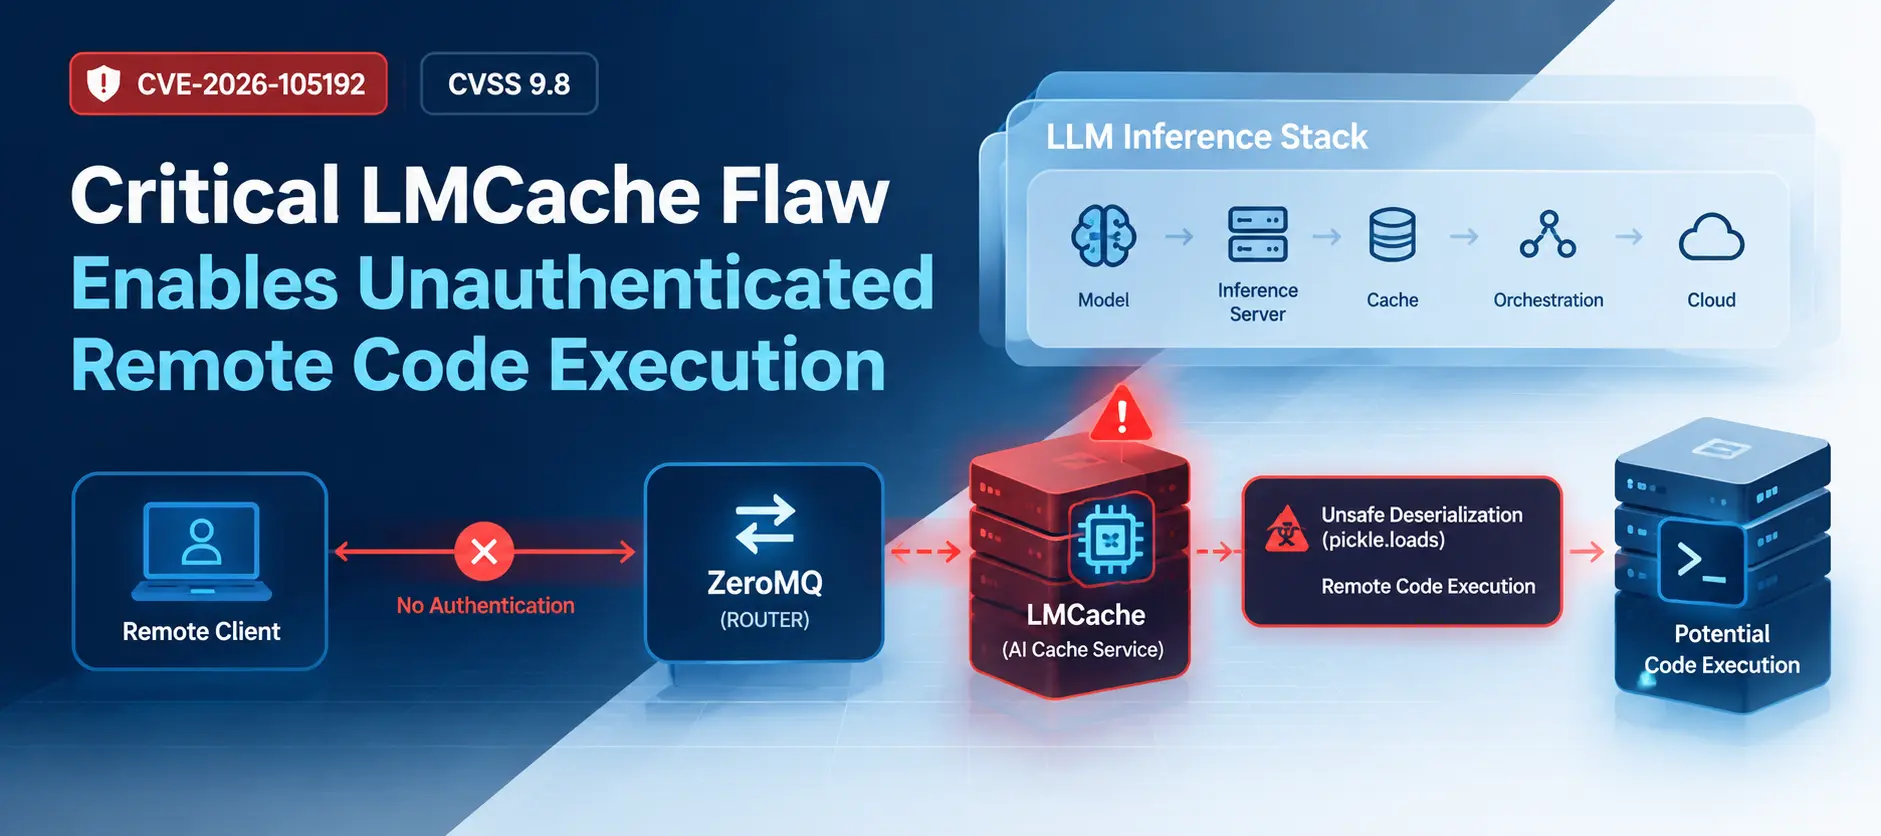
Critical LMCache Vulnerability Enables Unauthenticated Remote Code Execution
A critical LMCache flaw, CVE-2026-105192, allows unauthenticated remote code execution through unsafe Python pickle deserialization in its multiprocess ZeroMQ transport.
 Trending
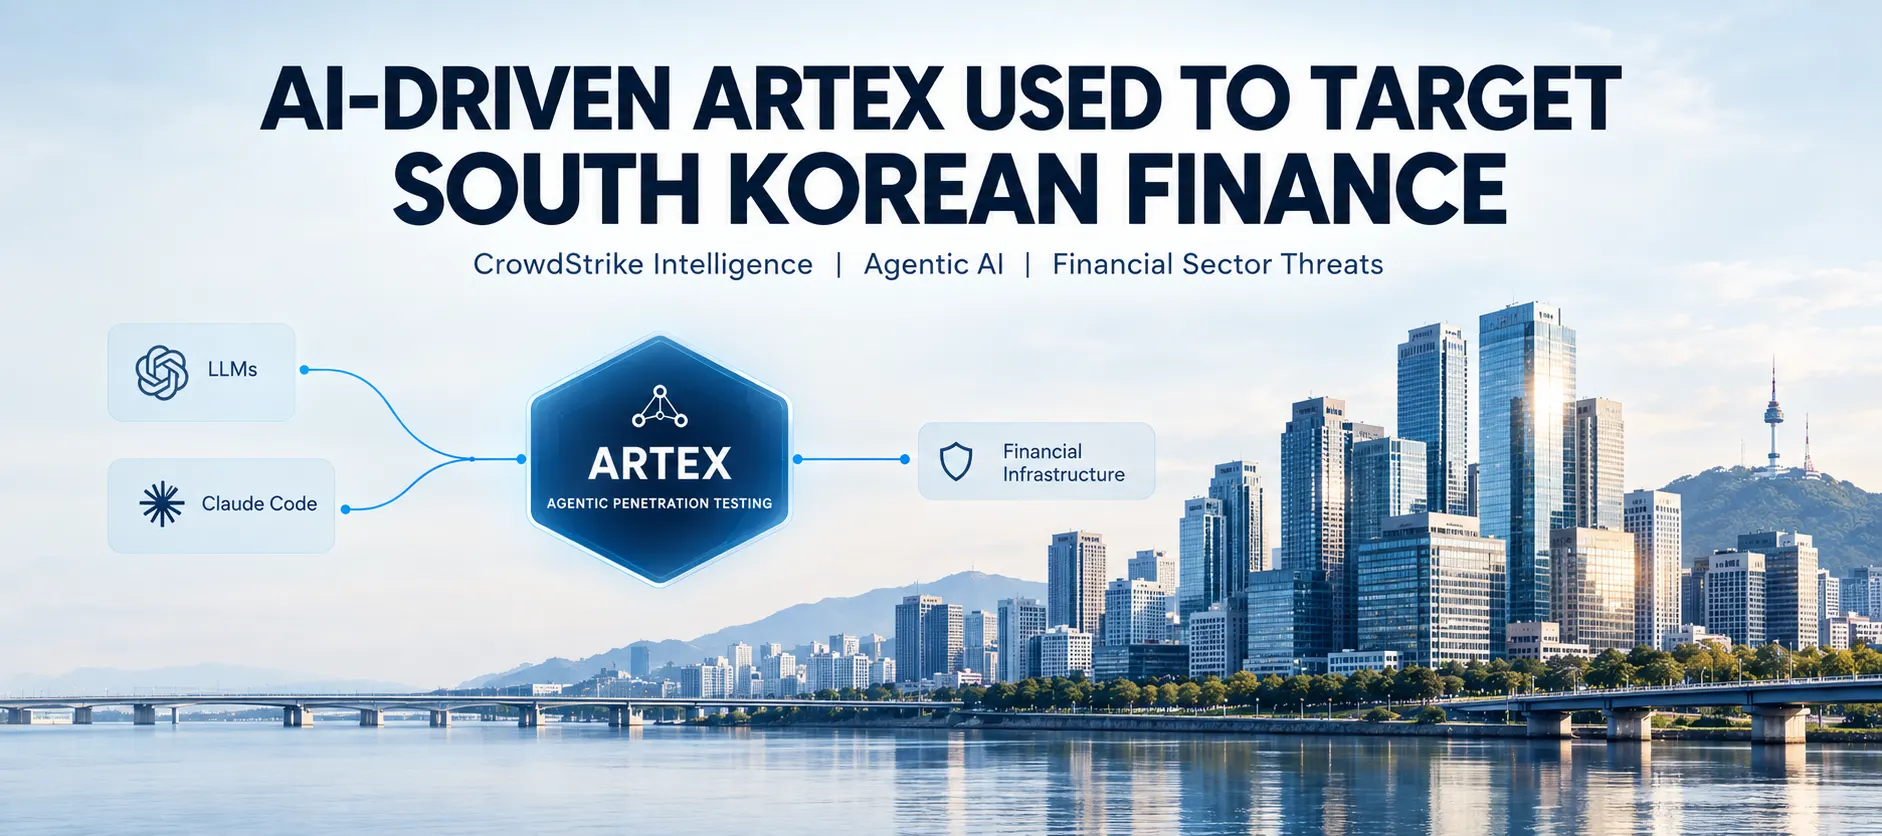
CrowdStrike Finds AI-Driven ARTEX Used Against South Korean Finance
CrowdStrike says an unidentified threat actor used the AI-driven ARTEX pentesting tool and multiple LLMs in a campaign targeting South Korean financial organizations from late September to early October 2026.
 Trending
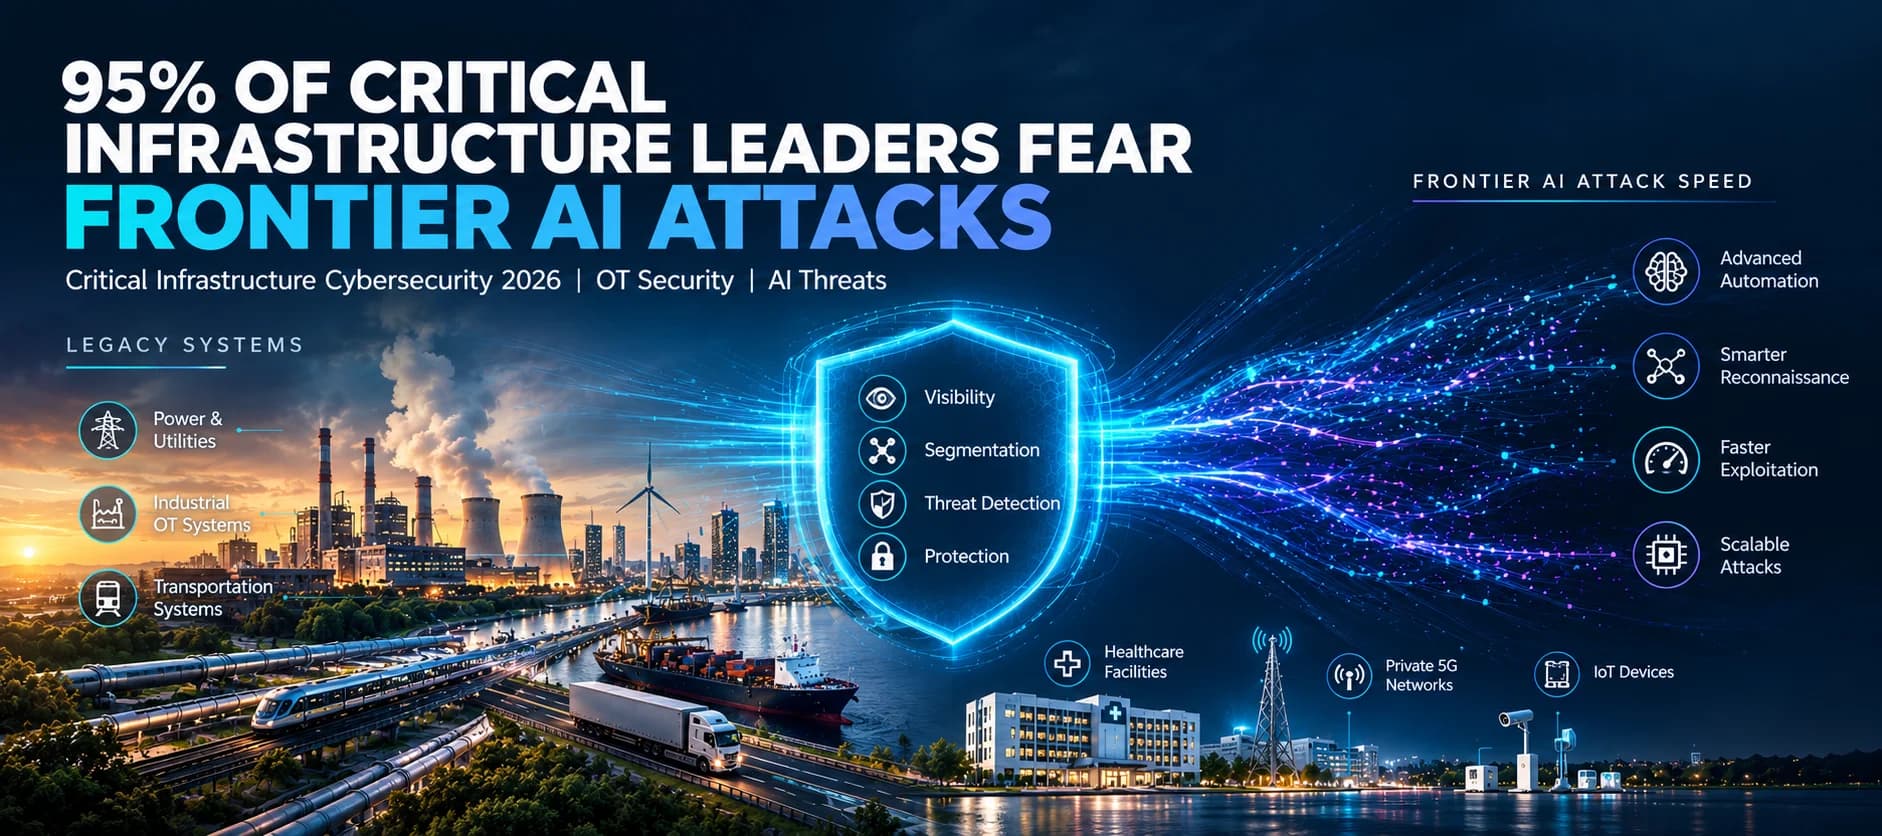
95% of Critical Infrastructure Leaders Are Concerned About Frontier AI Attacks
A Palo Alto Networks survey of more than 1,600 critical infrastructure security leaders finds 95% are concerned about Frontier AI-powered attacks, while legacy systems, visibility gaps and patching delays continue to challenge defenders.
 Trending
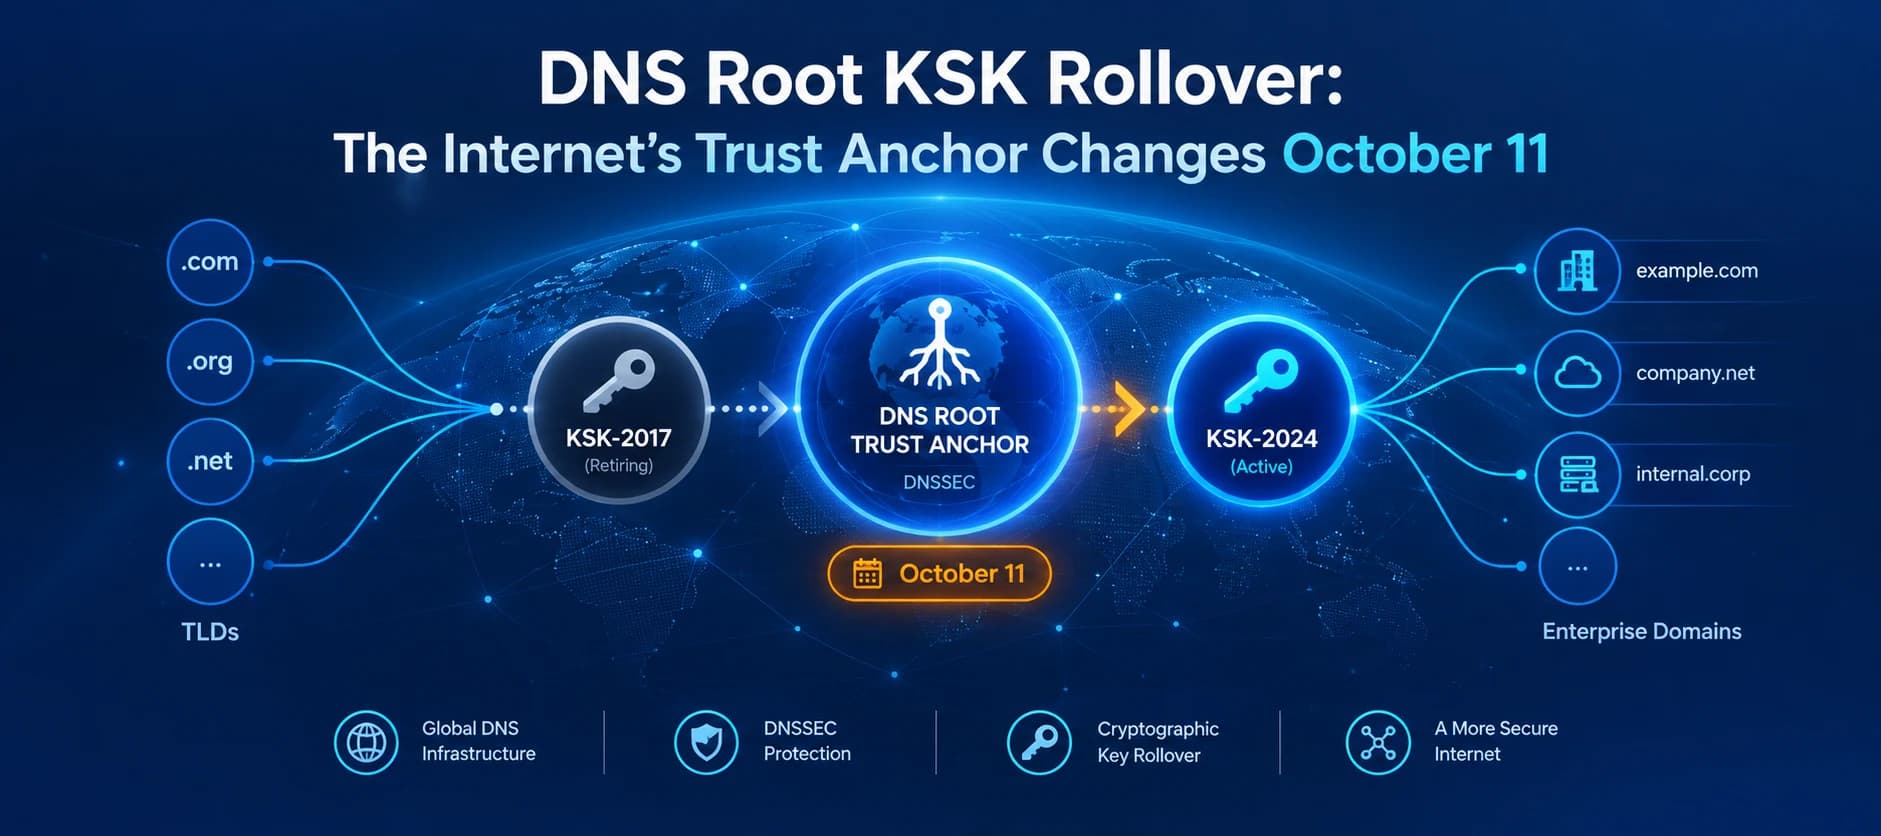
DNS Root Key Rollover Set for October 11: What Operators Need to Know
The DNS root will switch to a new key-signing key on October 11, 2026. Cloudflare explains why DNSSEC resolvers must trust KSK-2024 and how operators can test their readiness before the rollover.
 Trending
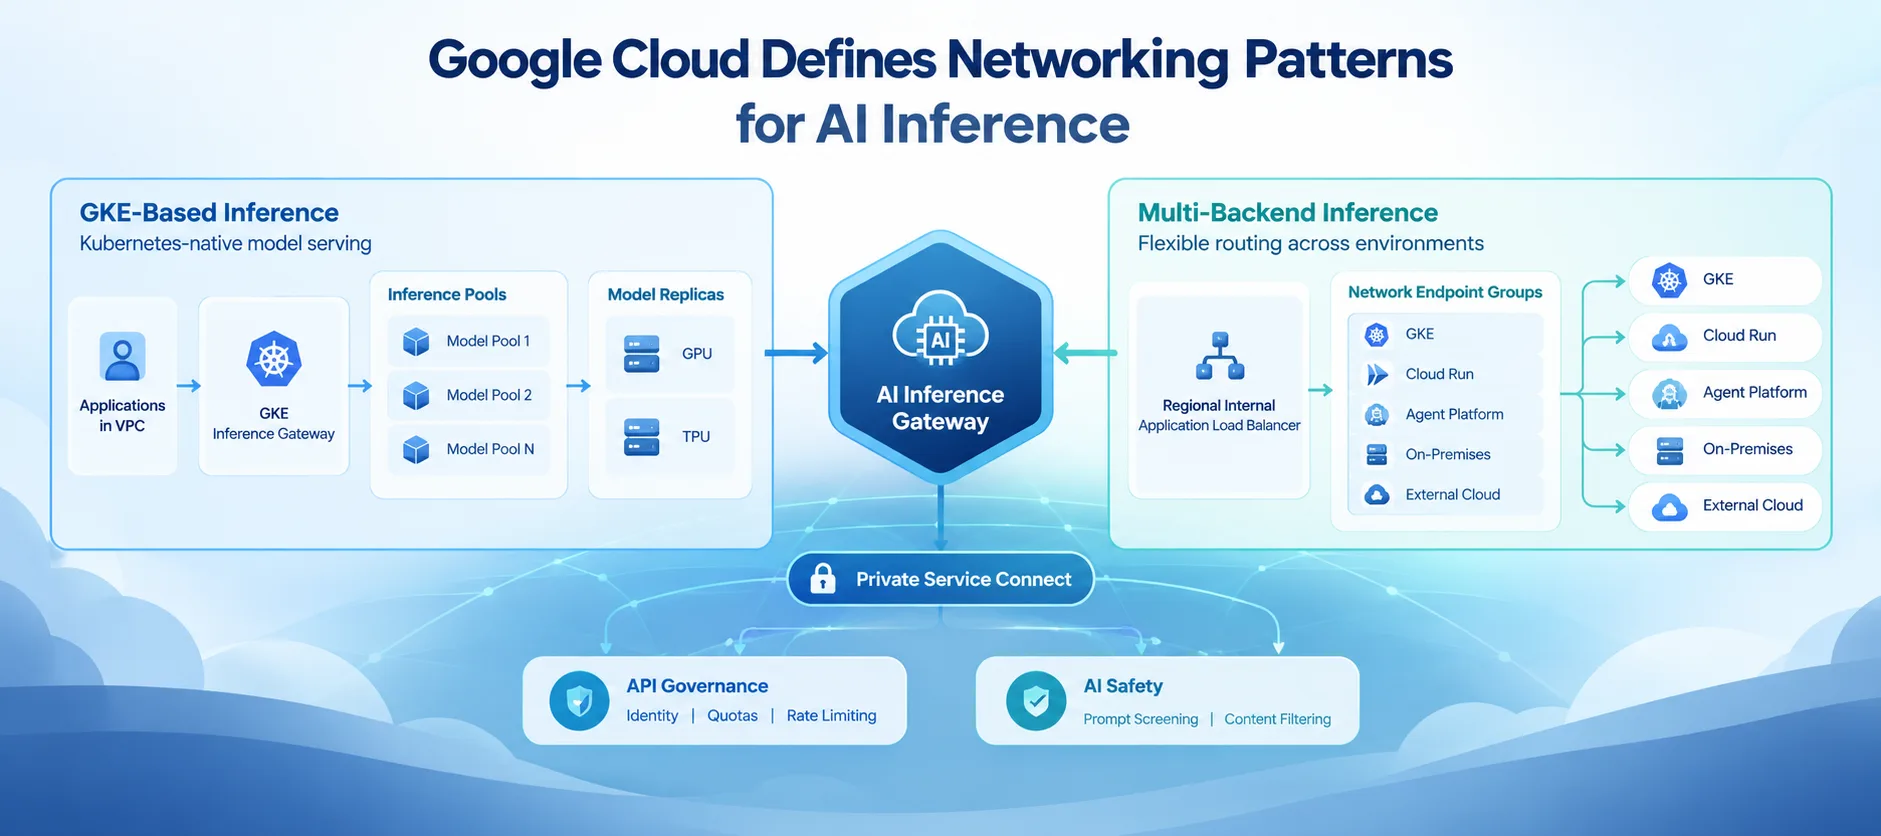
Google Cloud Outlines Secure Networking Architectures for AI Inference Across GKE and Hybrid Backends
Google Cloud has published two reference architectures for AI inference networking, covering GKE-only deployments and mixed backends such as Cloud Run, Agent Platform, on-premises systems and external clouds.
 Trending
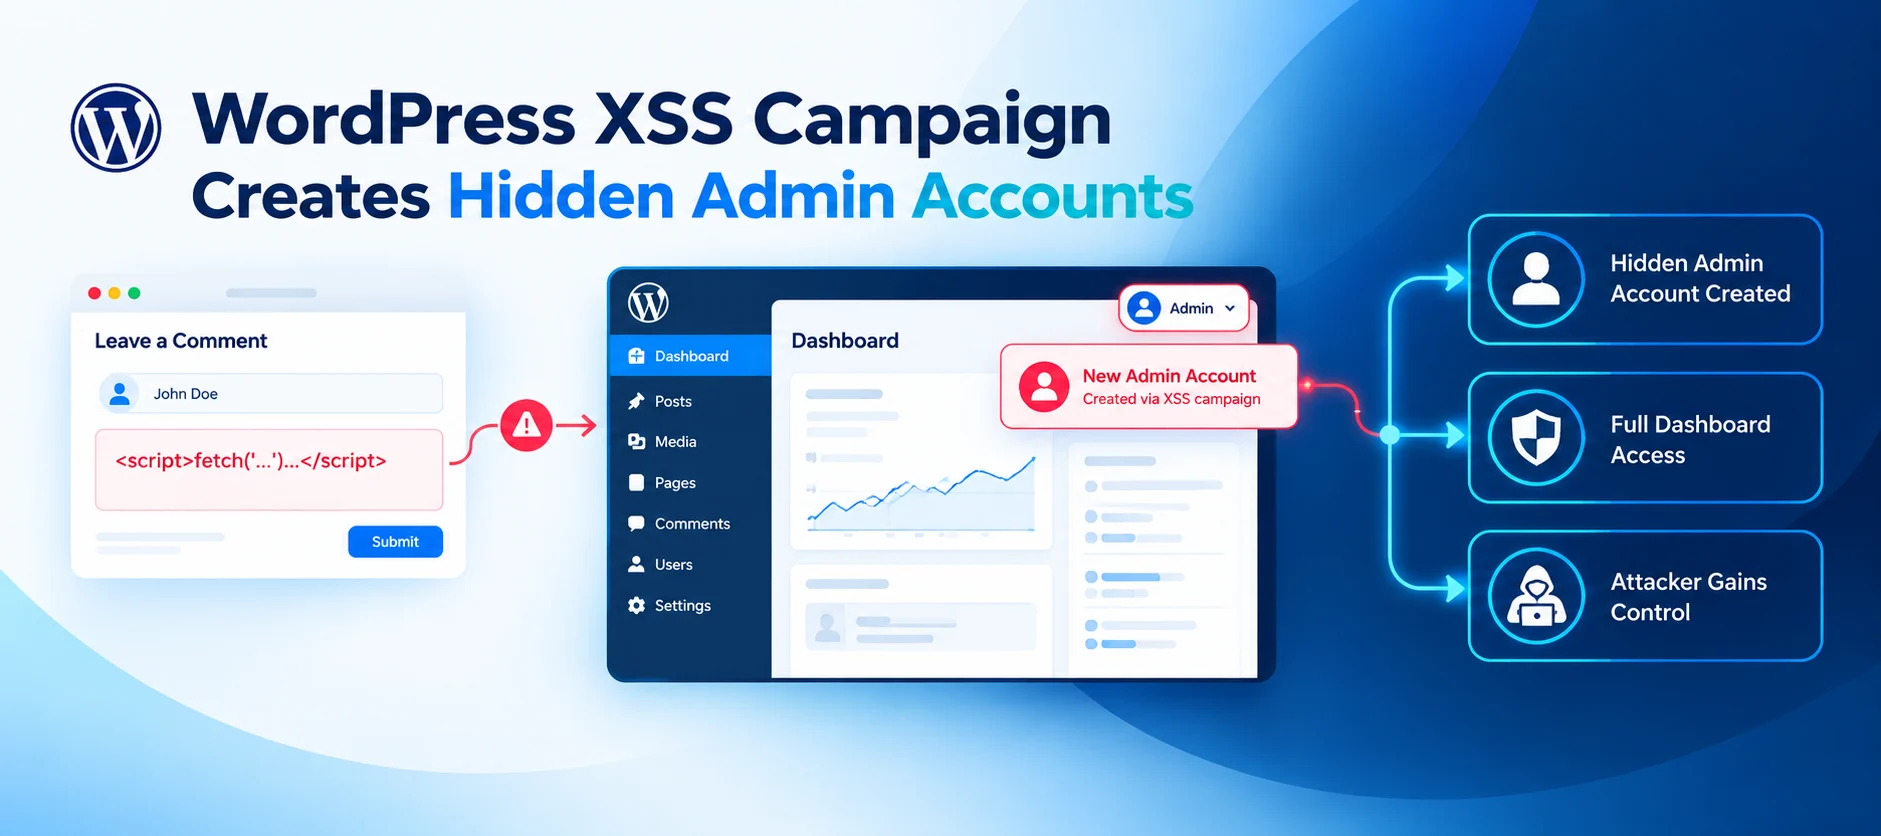
WordPress XSS Campaign Creates Hidden Admin Accounts and Multiple Backdoors
A new WordPress campaign is using stored XSS vulnerabilities in two plugins to compromise administrator sessions, install malicious plugins, create hidden admin accounts and establish multiple persistence mechanisms.
 Trending
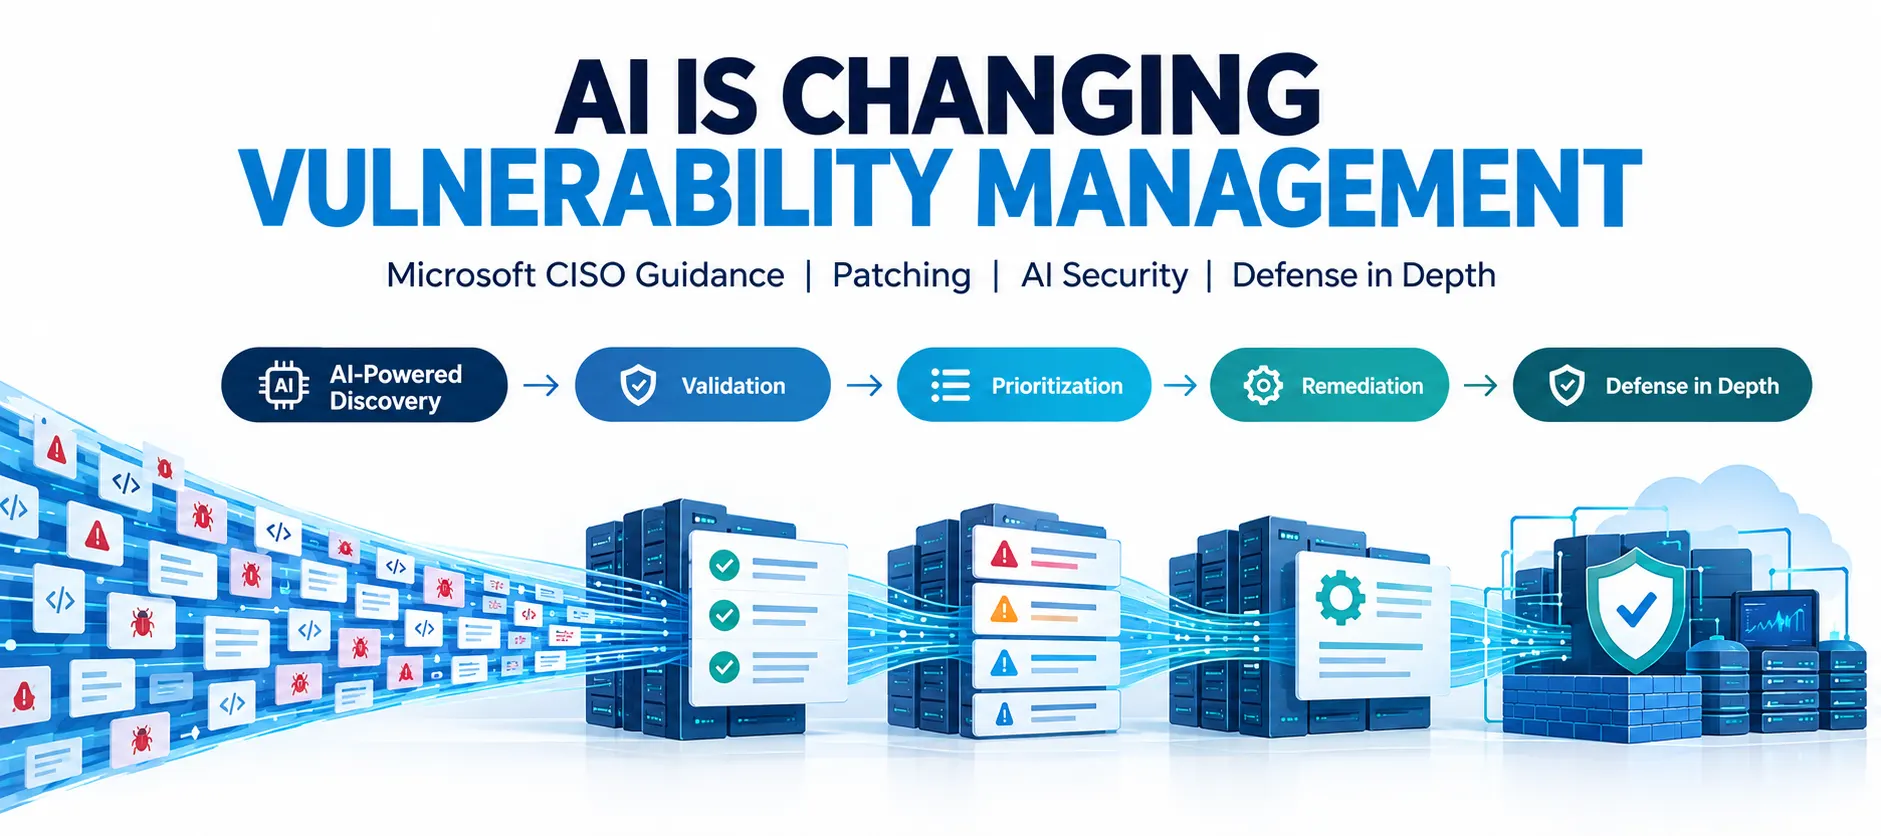
Microsoft Warns CISOs: AI Is Changing the Scale and Speed of Vulnerability Risk
Microsoft says frontier AI is increasing the volume and speed of vulnerability discovery, forcing CISOs to rethink patching, prioritization, defense in depth, and security controls as AI-assisted attacks accelerate.
 Trending
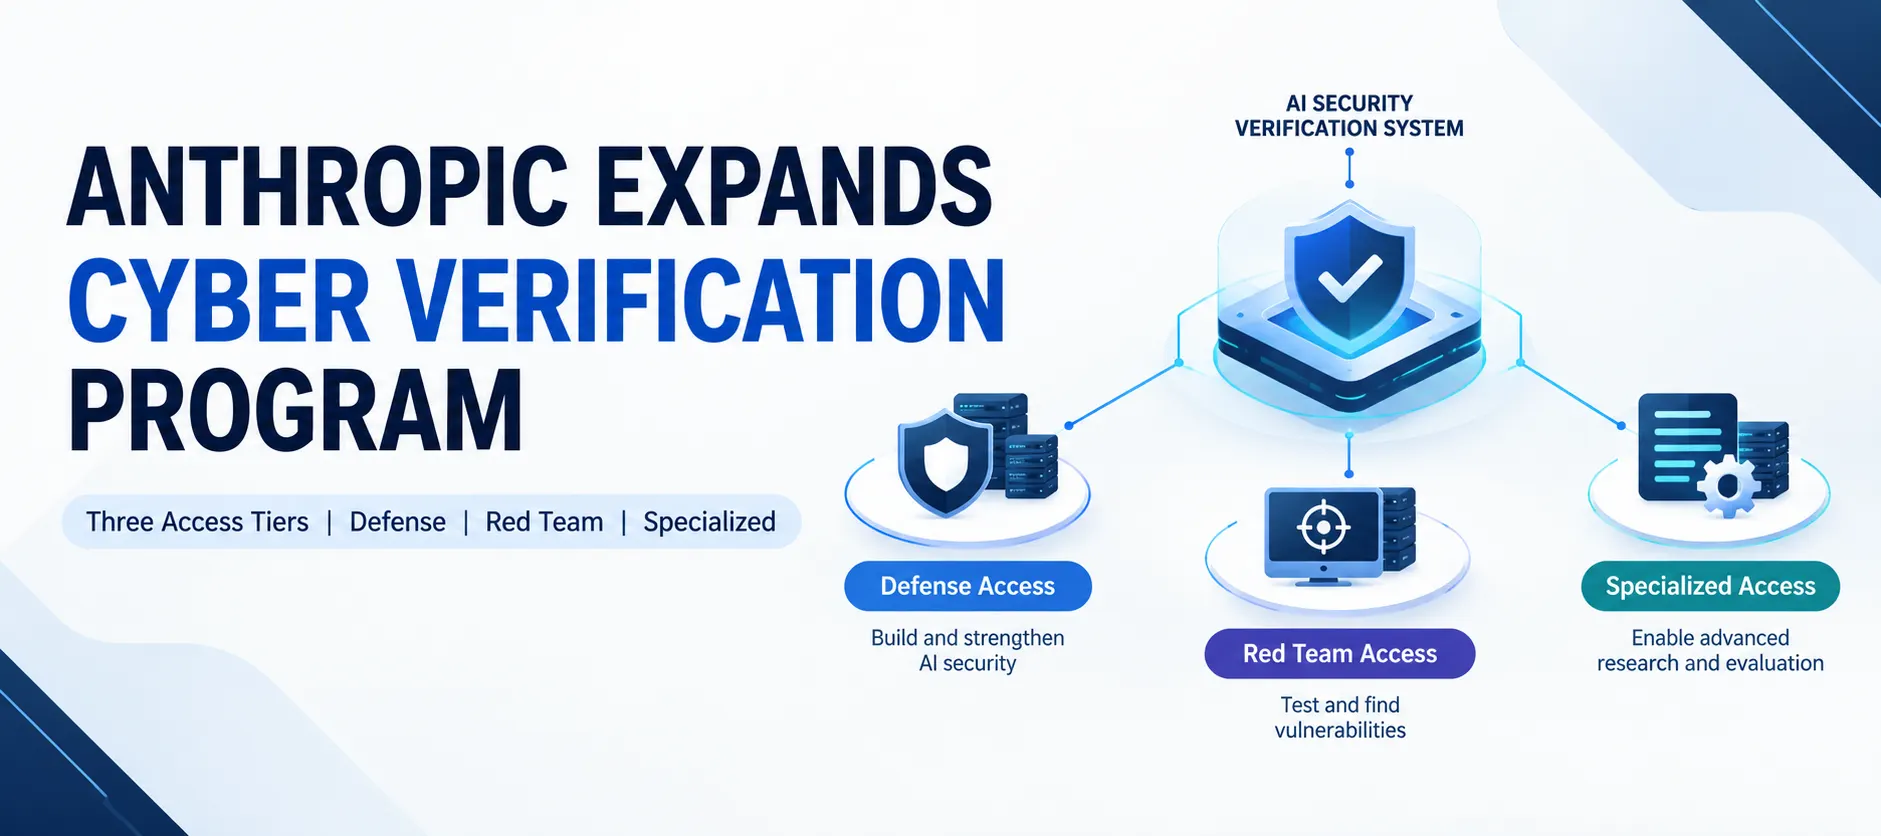
Anthropic Expands Cyber Verification Program With Three Access Tiers
Anthropic is expanding its Cyber Verification Program with three access tiers for security professionals, offering different levels of cyber capabilities and safeguards based on the type and risk of authorized security work.