
AWS Patches Critical File Access Flaw in Document Loader MCP Server
AWS has patched CVE-2026-130901, a path traversal vulnerability in its Document Loader MCP Server. Under specific configuration conditions, the flaw could allow unauthorized file reads outside the intended directory and PNG image writes to other locations.
Xcademia Team
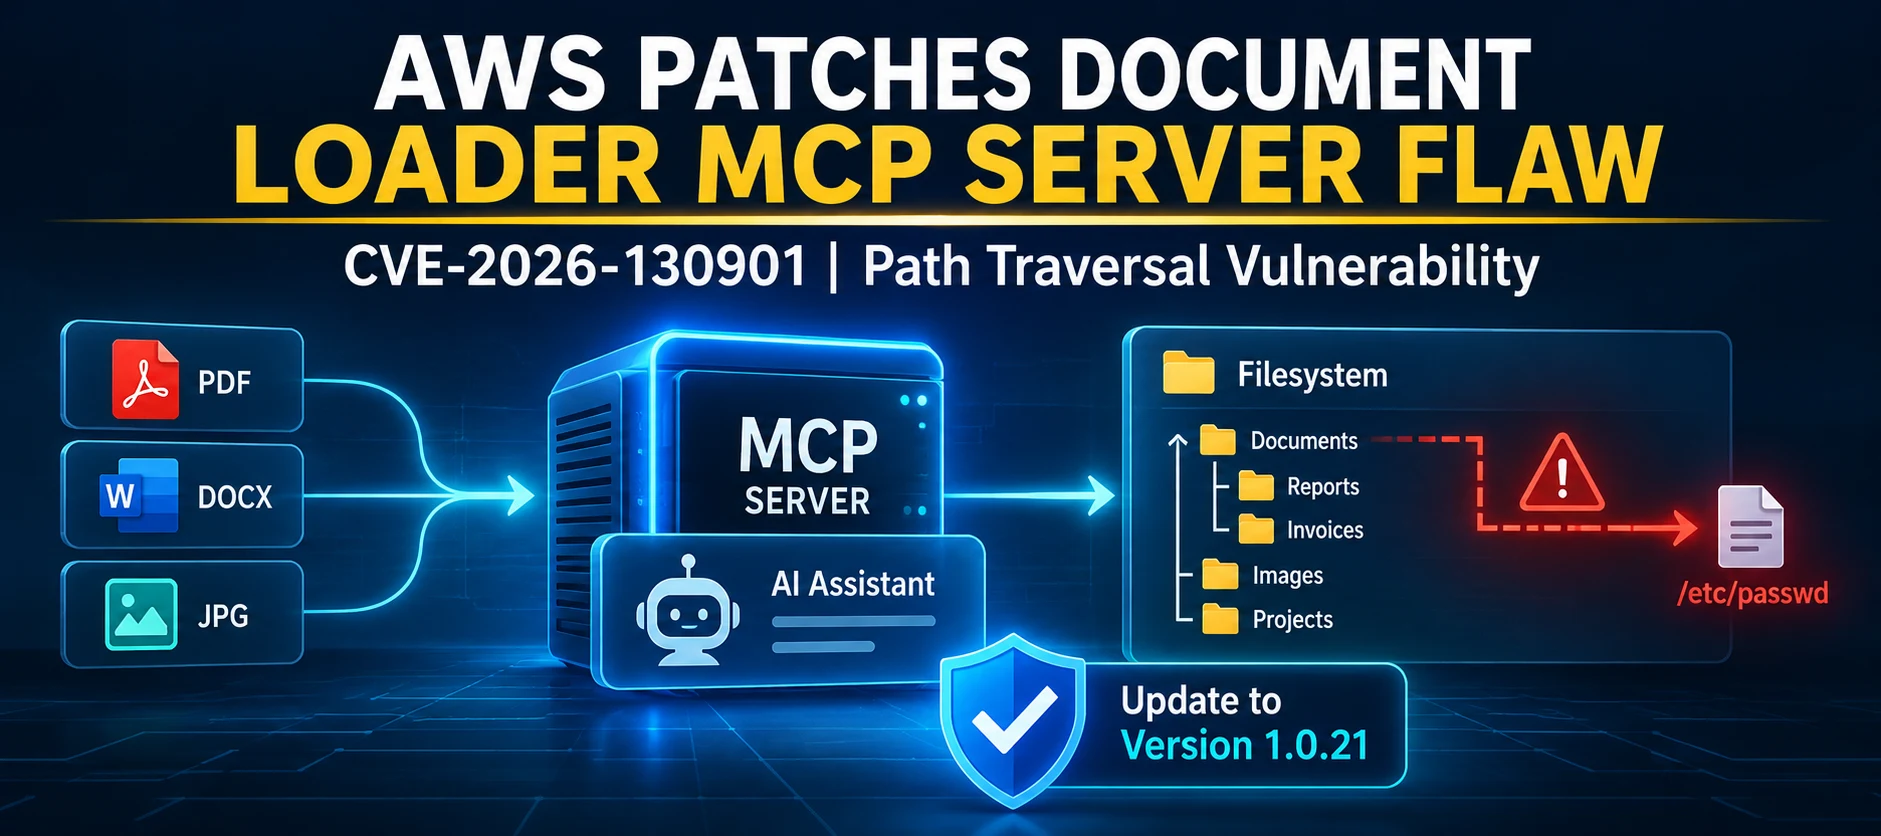
Amazon Web Services (AWS) has addressed a path traversal vulnerability in its open-source Document Loader Model Context Protocol (MCP) Server that could allow unauthorized access to files outside an intended directory under specific configuration conditions.
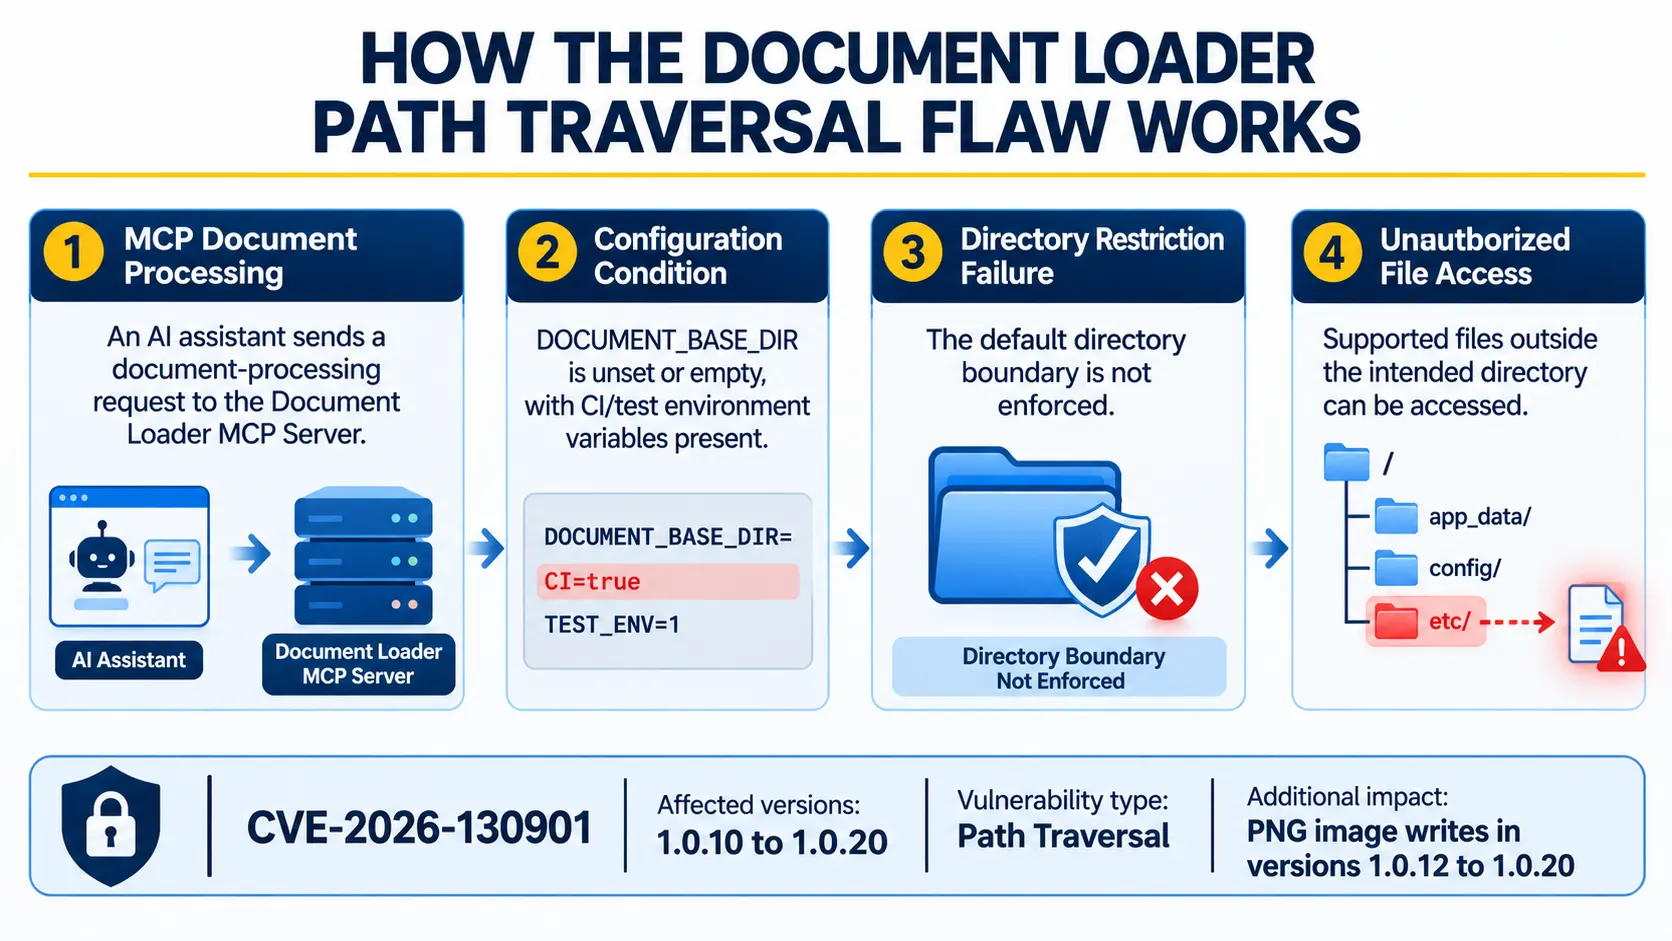
Tracked as CVE-2026-130901, the vulnerability affects Document Loader MCP Server versions 1.0.10 through 1.0.20. When the DOCUMENT_BASE_DIR environment variable is unset or empty and certain continuous integration or test environment variables are present, the server does not enforce its default base directory restriction.
An attacker who can influence the documents processed by an MCP client could potentially exploit this behavior to read supported files outside the designated directory. In versions 1.0.12 through 1.0.20, the issue could also allow PNG slide images to be written to other directories.
AWS disclosed the vulnerability in security bulletin 2026-195-AWS, published on November 20, 2026. The company has released a fix in awslabs.document-loader-mcp-server version 1.0.21 and recommends upgrading to the latest version.
What Is the AWS Document Loader MCP Server?
The Document Loader MCP Server is an open-source implementation of the Model Context Protocol (MCP) designed to help AI assistants process documents stored on a local filesystem.
It allows AI assistants to parse and extract content from different file formats, including:
PDF documents
Office files
Image files
The server provides a way for MCP-compatible clients to access document content through a standardized interface.
Because the software processes files from local storage, directory restrictions are important for controlling which documents the server can access.
The vulnerability disclosed by AWS affects how this directory restriction is enforced under specific environment configurations.
Understanding CVE-2026-130901
AWS identifies CVE-2026-130901 as an improper limitation of a pathname to a restricted directory.
This type of security weakness is associated with path traversal, where an application fails to properly restrict file paths to an intended directory.
In this case, the issue occurs when two conditions are present:
The
DOCUMENT_BASE_DIRenvironment variable is not configured or is set to an empty value.The server runs with continuous integration or test environment variables present.
Under these conditions, the default base directory restriction is not enforced.
As a result, an actor who can influence the documents an MCP client processes might be able to cause the server to access supported files outside the intended directory.
The issue therefore creates a potential file access boundary problem in environments running affected versions with the specified configuration.
Potential Impact: Unauthorized File Reads and PNG Image Writes
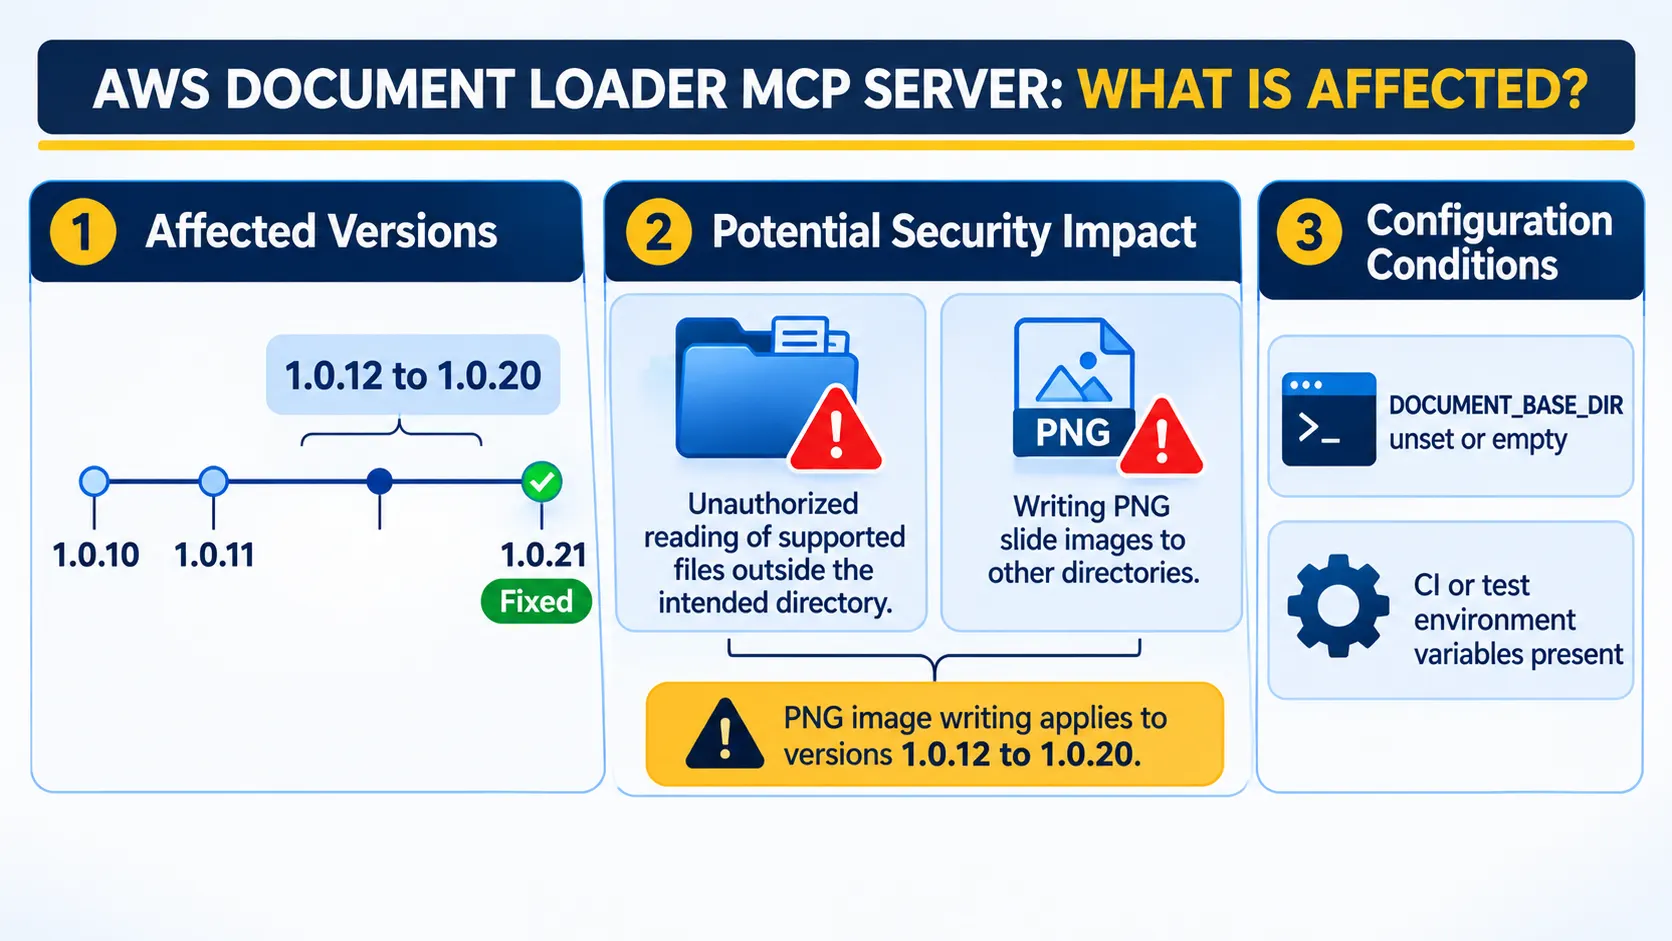
AWS identifies two potential consequences of exploiting the vulnerability.
1. Reading Files Outside the Intended Directory
An attacker who can influence the documents processed by an MCP client might be able to access supported files located outside the directory intended for document processing.
This behavior could expose files that should remain outside the server's permitted document access boundary.
The vulnerability is conditional. AWS specifically identifies the unset or empty DOCUMENT_BASE_DIR configuration and the presence of continuous integration or test environment variables as necessary circumstances for the described issue.
2. Writing PNG Slide Images to Other Directories
AWS also identifies an additional impact affecting a narrower range of releases.
In Document Loader MCP Server versions 1.0.12 through 1.0.20, the vulnerability might allow an attacker to write PNG slide images to directories outside the intended location.
This write capability is not listed for the entire affected version range. AWS specifically associates it with versions 1.0.12 through 1.0.20.
Affected Document Loader MCP Server Versions
According to AWS, the vulnerability affects the following version range:
Component | Affected Versions |
|---|---|
awslabs.document-loader-mcp-server | 1.0.10 through 1.0.20 |
The affected version condition is:
>= 1.0.10 AND < 1.0.21
The additional PNG slide image write issue applies specifically to versions 1.0.12 through 1.0.20.
Organizations using the affected package should review their installed versions and configuration settings to determine whether their deployments are exposed.
AWS Releases Version 1.0.21 to Address the Vulnerability
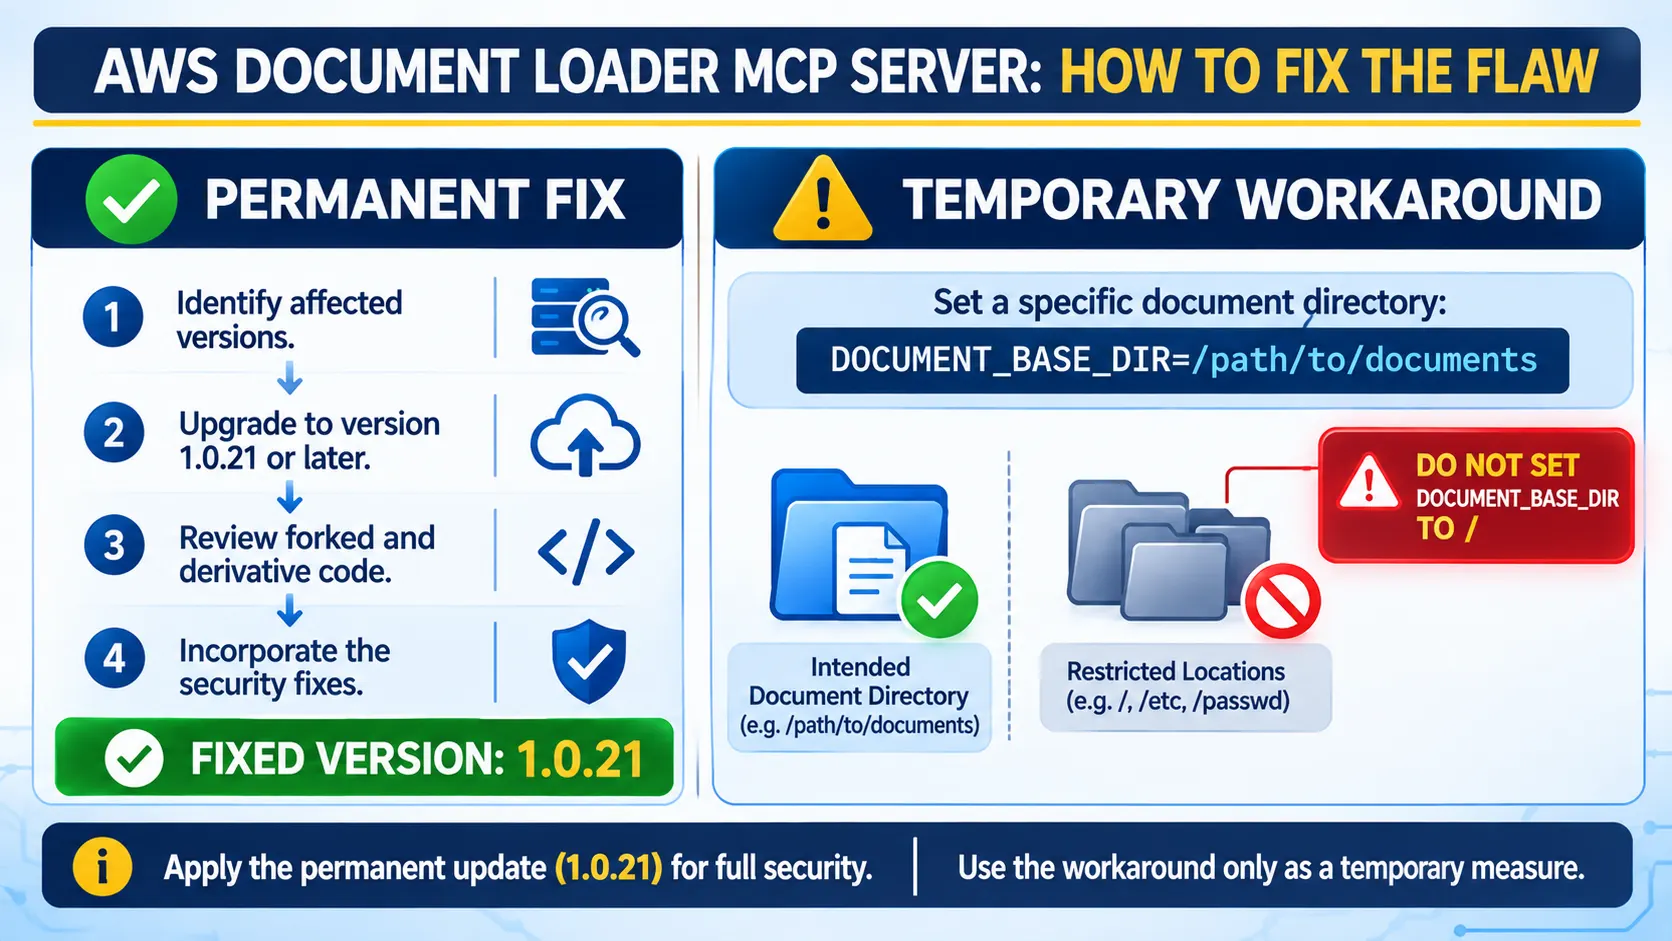
AWS has addressed CVE-2026-130901 in awslabs.document-loader-mcp-server version 1.0.21.
The company recommends upgrading to the latest available version and ensuring that any forked or derivative implementations also incorporate the security fixes.
The fixed release is available through the Python Package Index (PyPI):
Package: awslabs.document-loader-mcp-server
Fixed version: 1.0.21
Package release:
https://pypi.org/project/awslabs.document-loader-mcp-server/1.0.21/
Organizations maintaining modified versions or forks of the project should also review their code and apply the corresponding fixes rather than assuming that updating the original package automatically addresses derivative implementations.
Workaround for Organizations Unable to Upgrade Immediately
For environments where an immediate upgrade is not possible, AWS provides a configuration-based workaround.
Administrators should set the DOCUMENT_BASE_DIR environment variable to the directory that contains the documents the server is intended to process.
For example:
DOCUMENT_BASE_DIR=/path/to/documents
The configured path should point to the appropriate document directory.
AWS explicitly warns against setting this variable to /, because doing so removes the directory restriction.
This workaround helps restore the intended directory boundary while organizations prepare to upgrade to the fixed release.
However, AWS recommends upgrading to the latest version rather than relying solely on the workaround.
What Organizations Using MCP-Based Document Processing Should Do
The vulnerability highlights the importance of reviewing filesystem access restrictions in AI-connected tools, particularly those that process documents from local storage.
Organizations using the affected Document Loader MCP Server should consider the following actions based on AWS's advisory:
1. Identify Affected Installations
Check whether environments use awslabs.document-loader-mcp-server versions 1.0.10 through 1.0.20.
Pay particular attention to deployments operating in continuous integration or test environments.
2. Review the DOCUMENT_BASE_DIR Setting
Verify that the environment variable is configured with the intended document directory and is not empty.
3. Upgrade to Version 1.0.21
Install the fixed release or a later available version to address the reported vulnerability.
4. Review Forked and Derivative Implementations
Organizations that maintain customized versions should ensure that the corresponding security fixes are incorporated into their code.
5. Apply the Temporary Workaround if Necessary
If an immediate upgrade is not possible, configure DOCUMENT_BASE_DIR to the directory containing the documents. Do not use / as the configured path.
Security Disclosure and Research Acknowledgement
AWS published the issue under security bulletin 2026-195-AWS on November 20, 2026.
The company acknowledged Rishaank Gupta for collaborating on the vulnerability through its coordinated disclosure process.
The advisory identifies the affected package versions, the configuration conditions associated with the vulnerability, the potential file access impacts and the available remediation.
AWS does not provide a specific CVSS score, exploitation statistics or details of confirmed attacks in this bulletin.
Conclusion
CVE-2026-130901 highlights a filesystem access control weakness in AWS's open-source Document Loader MCP Server.
Under specific environment configurations, the vulnerability could allow an actor who influences documents processed by an MCP client to read supported files outside the intended directory. Certain affected versions could also permit PNG slide images to be written to other directories.
AWS has addressed the issue in version 1.0.21 and recommends upgrading, including updating forked and derivative implementations.
Organizations unable to upgrade immediately should configure DOCUMENT_BASE_DIR to the intended document directory and avoid setting it to /.
For teams using MCP-based document processing, reviewing filesystem boundaries and keeping document-processing components updated remain important security considerations.
Source: AWS Security Bulletins
About the Author