
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 189
- Trending now
- 5
- Breaking
- Live
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
 Trending
P7 DarkSword: New iOS Spyware Variant Adds Stealth and Crypto Wallet Theft
iVerify has identified P7 DarkSword, a modified iOS spyware variant that reduces its on-device footprint, targets keychain and cryptocurrency wallet data, and supports two-way communication with attacker infrastructure.
 Trending
AWS Fixes Sensitive Information Logging Issue in Tools for PowerShell
AWS has patched CVE-2026-107783, a vulnerability in AWS Tools for PowerShell that could expose IAM users' cleartext AWS Management Console passwords through command output and log files. Users of versions 5.0.305 and earlier should upgrade to version 5.0.306 or later.
 Trending
GitHub Strengthens Code Security Analysis With CodeQL 2.27.2
GitHub has released CodeQL 2.27.2 with improved security analysis across C++, Go, Rust, and JavaScript. The update also introduces changes to Go control-flow analysis and clarifies macOS compatibility limitations for compiled-language scanning.
 Trending
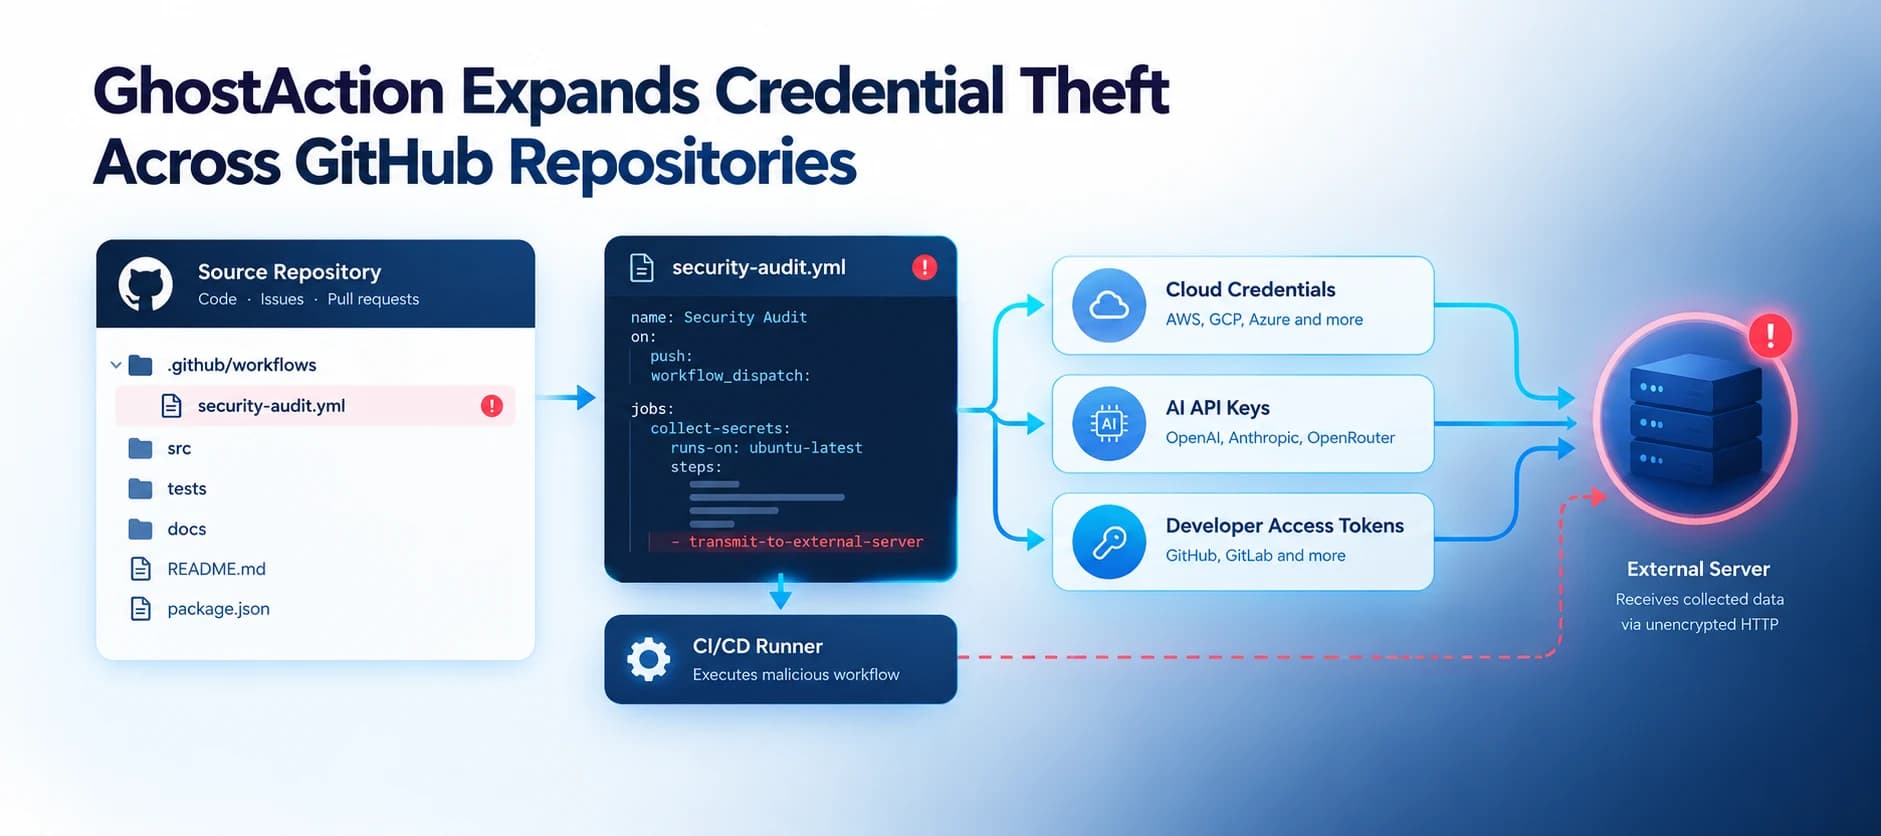
GhostAction Campaign Expands to Steal Cloud Credentials and AI API Keys From GitHub Repositories
GhostAction targets GitHub Actions secrets, cloud credentials and AI API keys through malicious workflows, exposing sensitive data in source code and Git history.
 Trending
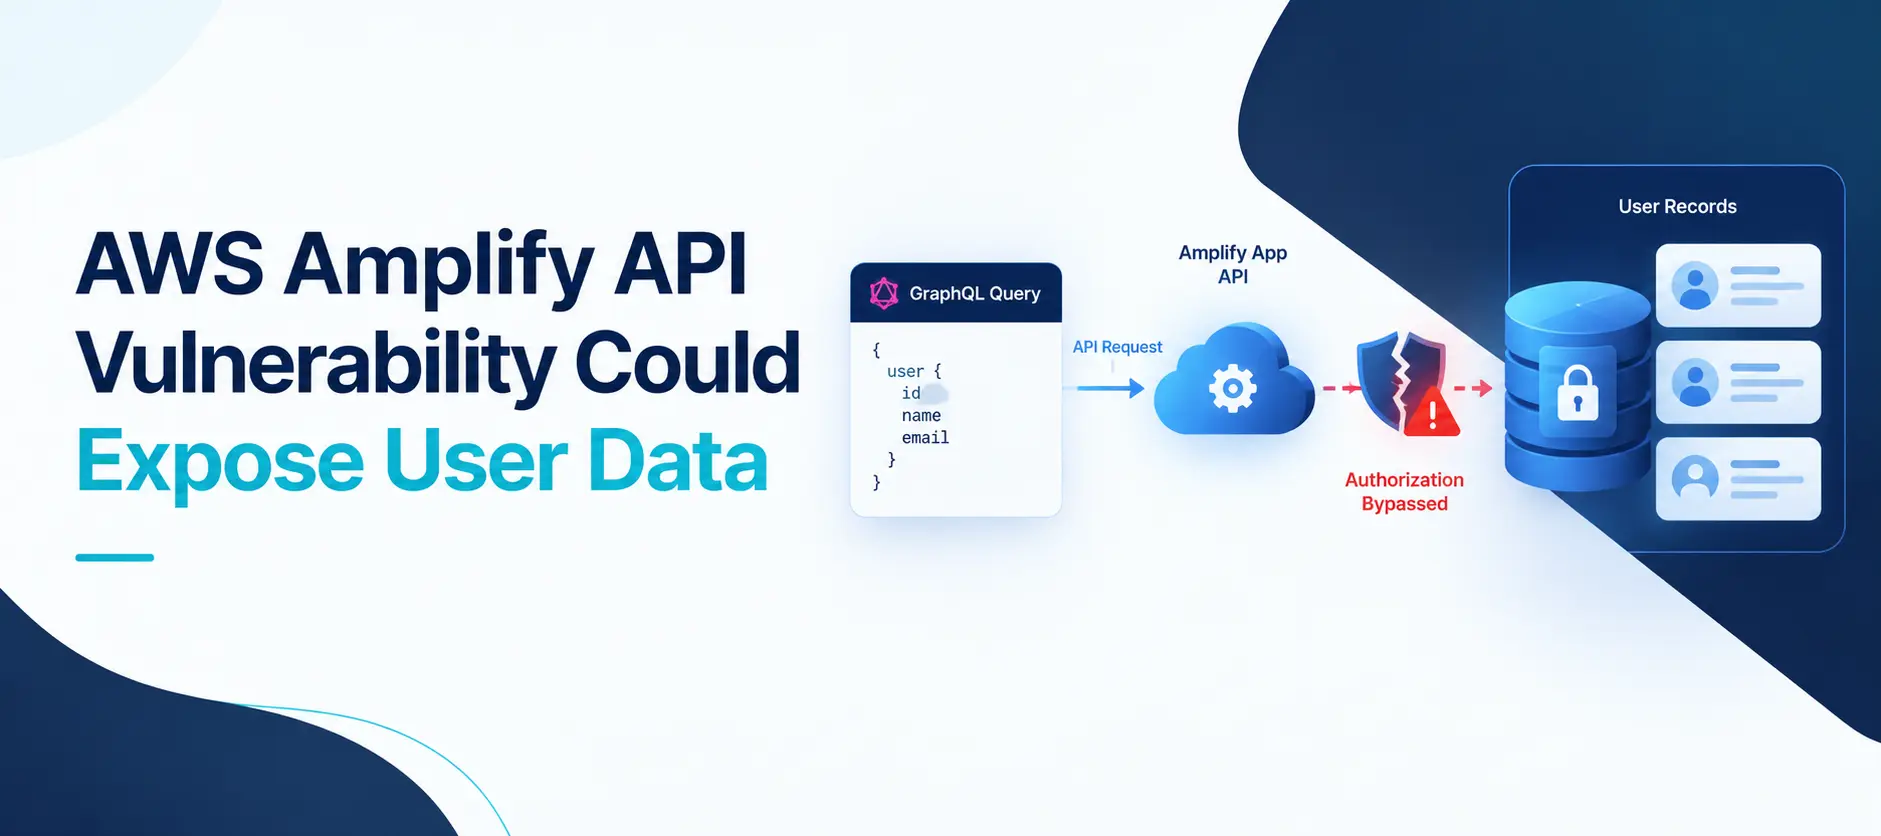
AWS Amplify API Vulnerability Could Expose Other Users' Data: CVE-2026-108096
AWS has disclosed CVE-2026-108096, an authorization vulnerability affecting AWS Amplify API components that could allow authenticated users to read other users' records through crafted GraphQL queries. Developers should upgrade affected packages and redeploy their backends.
 Trending
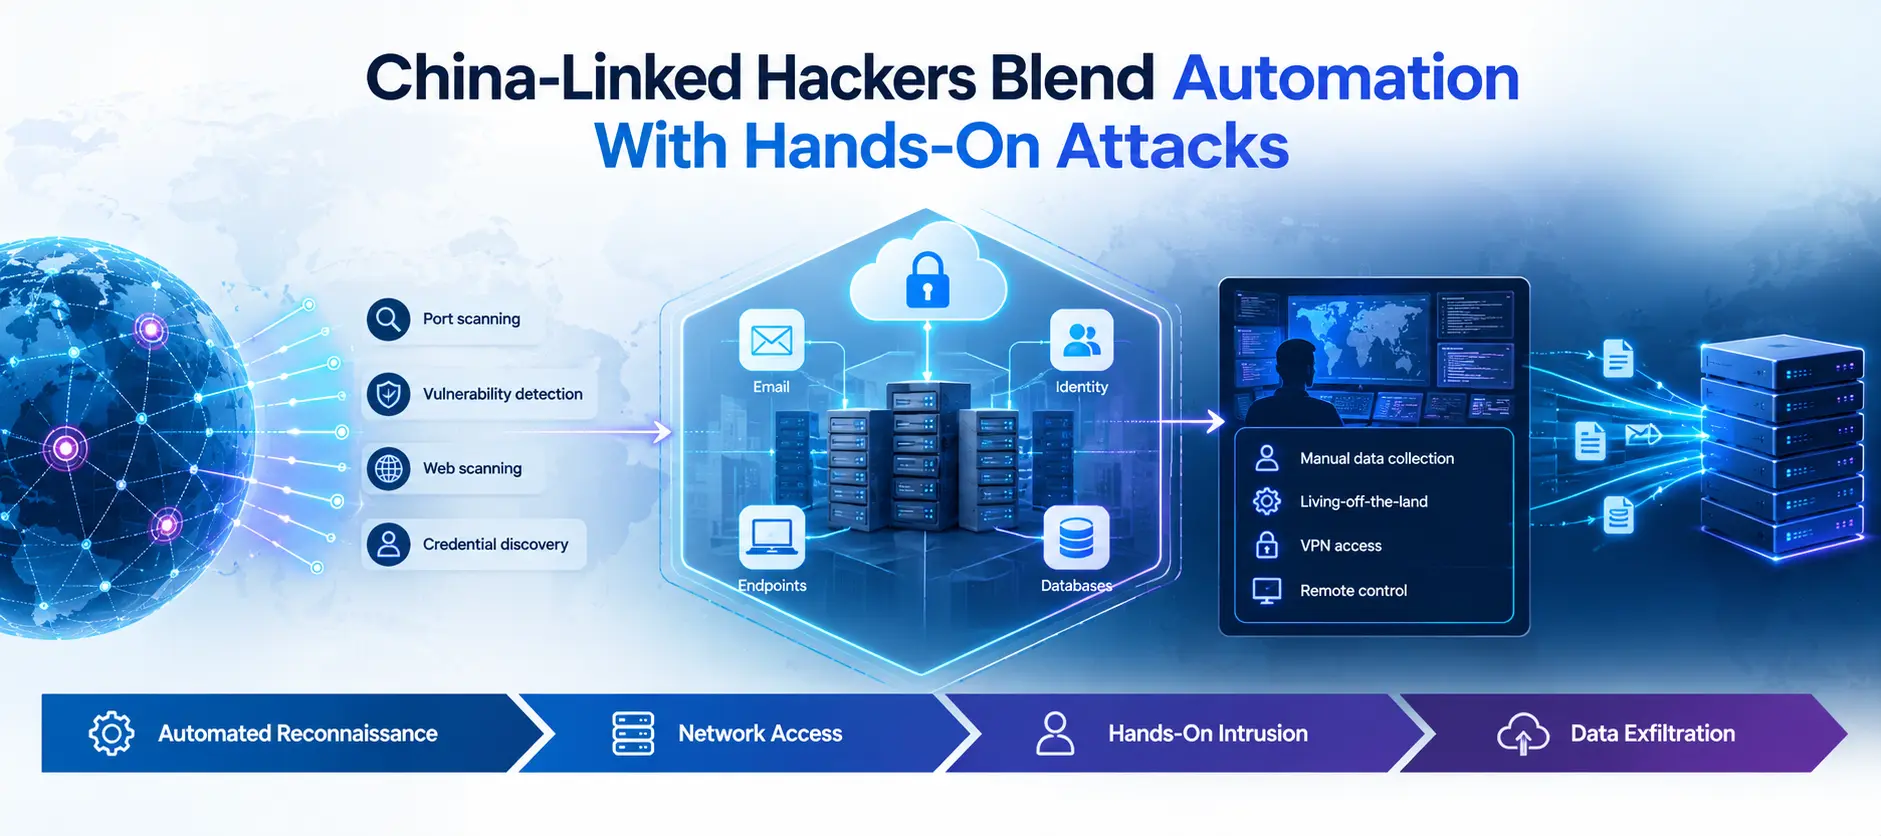
Chinese Government-Linked Cyber Actors Use Automation and Manual Hacking to Steal Data
A joint cybersecurity advisory warns that China-linked threat actors are combining large-scale scanning, botnets, exploitation tools and hands-on techniques to compromise networks and steal sensitive data.
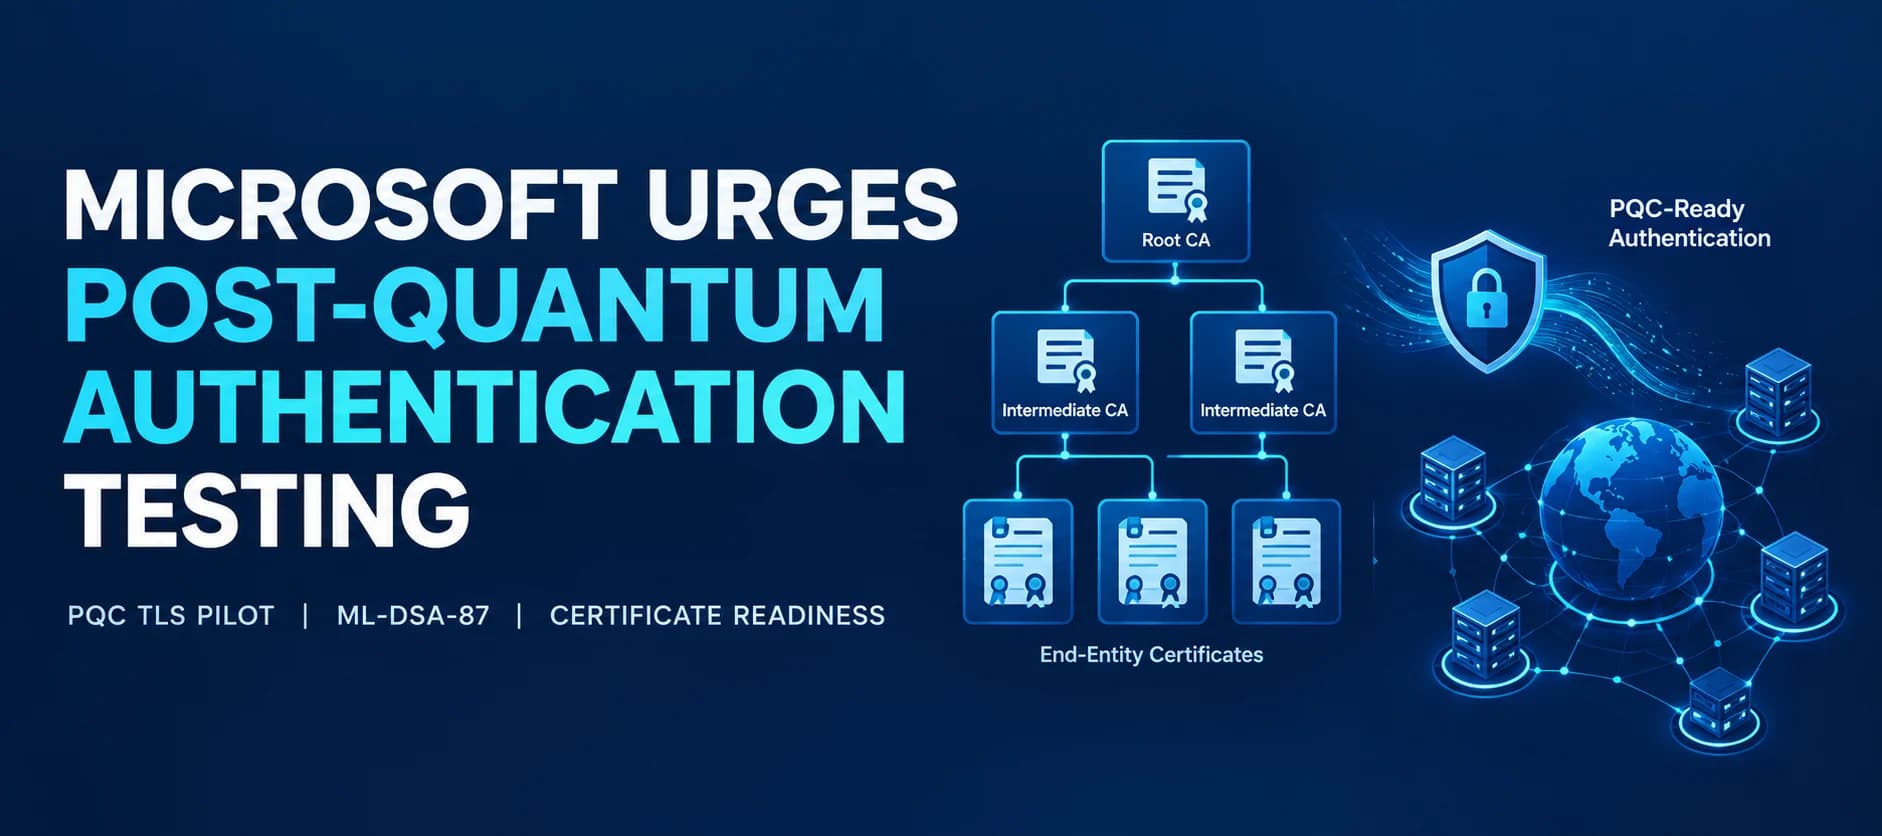
Microsoft Urges Organizations to Test Post-Quantum Certificate Systems
Microsoft is urging organizations to test post-quantum authentication before wider adoption. Its PQC TLS Pilot Program helps eligible certificate authorities evaluate certificate interoperability, compatibility, performance, and operational readiness in controlled environments.
 Trending
OpenAI Disrupts Russian and Iranian AI-Enabled Influence Operations
OpenAI has banned two covert influence operations linked to Russia and Iran that used AI-generated content, fabricated identities and deceptive publishing tactics to spread geopolitical narratives. The cases highlight how AI can amplify traditional disinformation campaigns.
 Trending
DOJ and FBI Seize Microscan and FishHub Tools Linked to Flax Typhoon
The U.S. Justice Department and FBI seized two cyber tools allegedly used by China-linked actors to scan networks and facilitate spear-phishing intrusions targeting critical infrastructure and organisations worldwide.
 Trending
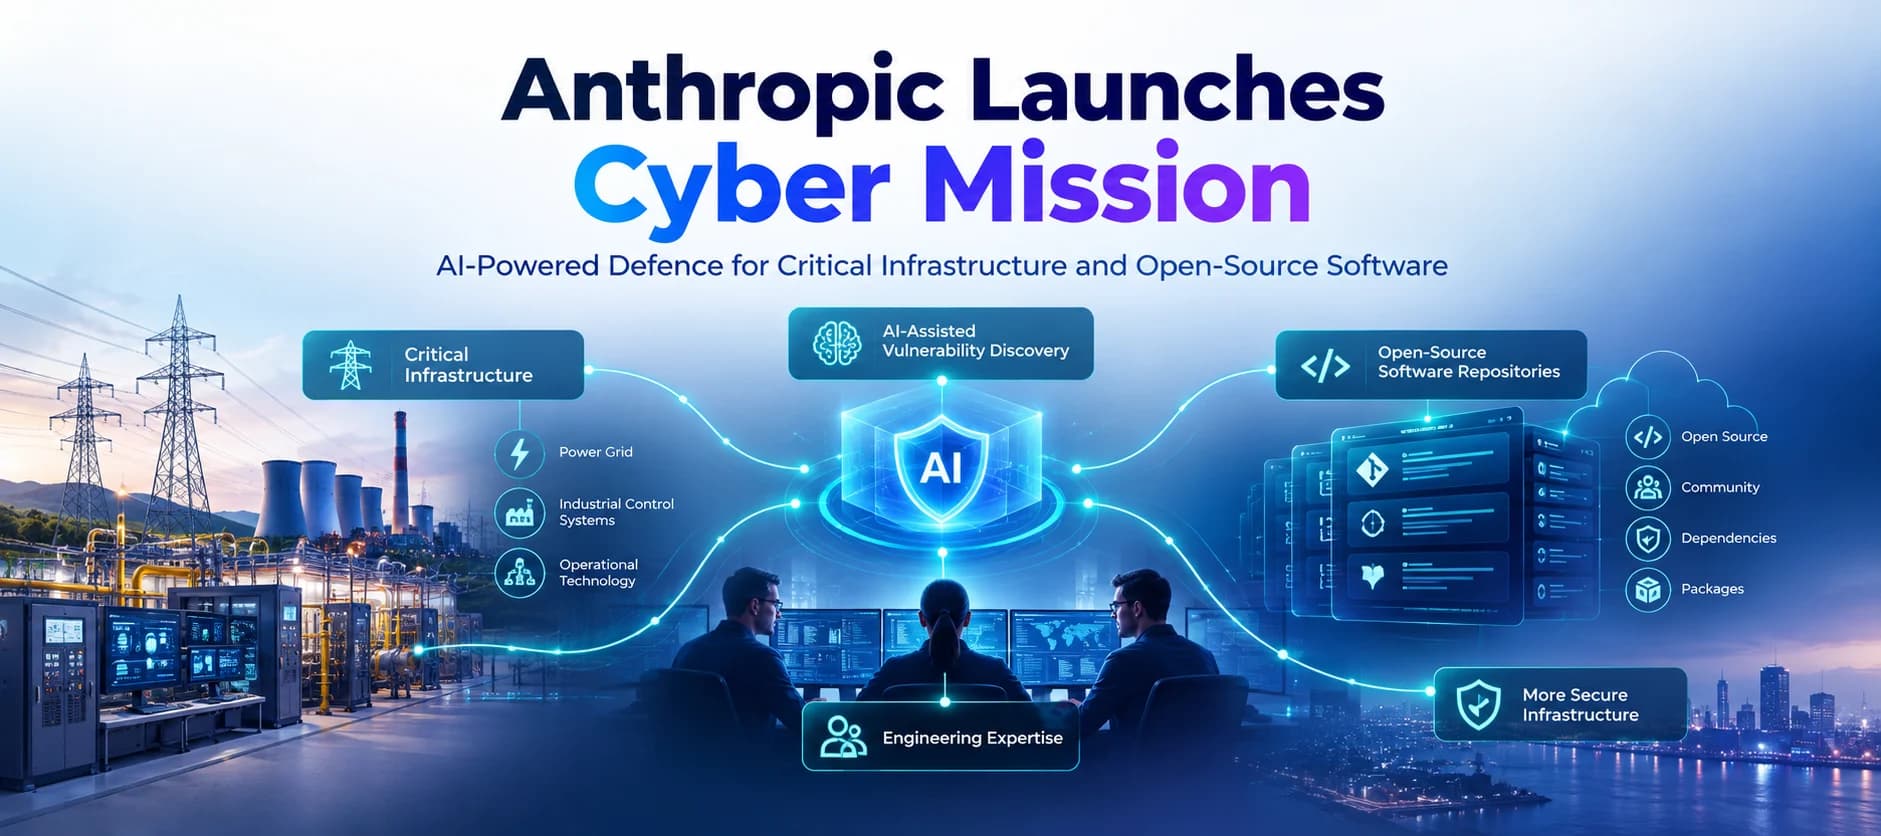
Anthropic Launches Cyber Mission to Protect Critical Infrastructure and Open-Source Software
Anthropic has launched its Cyber Mission, a long-term initiative combining AI models, engineering expertise and free vulnerability scanning to strengthen critical infrastructure and open-source software security.
 Trending
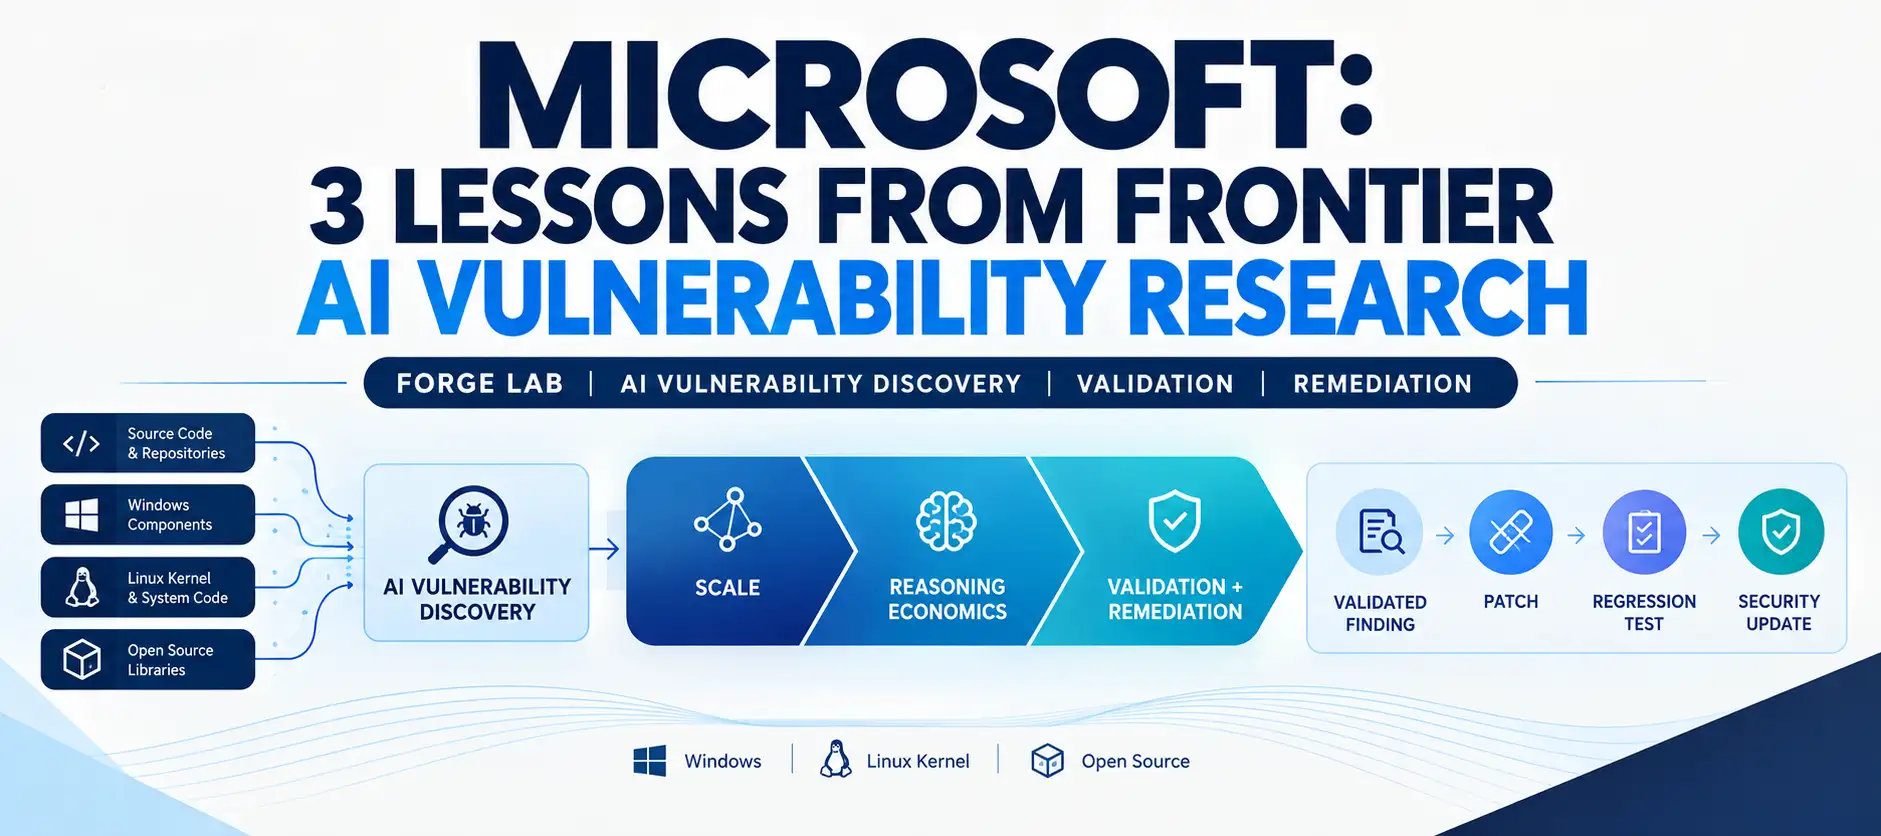
Microsoft Reveals 3 Lessons From AI-Powered Vulnerability Research
Microsoft's FORGE Lab says AI-driven vulnerability discovery is reaching meaningful scale, but validation, remediation, human review and engineering capacity are becoming critical constraints.