
AWS Fixes Sensitive Information Logging Issue in Tools for PowerShell
AWS has patched CVE-2026-107783, a vulnerability in AWS Tools for PowerShell that could expose IAM users' cleartext AWS Management Console passwords through command output and log files. Users of versions 5.0.305 and earlier should upgrade to version 5.0.306 or later.
Xcademia Team
AWS Patches Password Exposure Vulnerability in Tools for PowerShell
Amazon Web Services (AWS) has addressed a security vulnerability in AWS Tools for PowerShell that could allow local users to recover an IAM user's cleartext AWS Management Console password from command output and log artifacts.
Tracked as CVE-2026-107783, the issue affects AWS Tools for PowerShell versions 5.0.305 and earlier. AWS published the security bulletin on October 9, 2026, identifying the issue as an important security matter requiring attention.
The vulnerability involves the insertion of sensitive information into log files. AWS has released a fix in version 5.0.306 and recommends upgrading to the latest version.
What Is CVE-2026-107783?
AWS Tools for PowerShell enables developers and administrators to manage AWS services through the PowerShell scripting environment.
According to the AWS security bulletin, the vulnerability could allow local users to recover an IAM user's cleartext AWS Management Console password from command output and log artifacts.
The issue is associated with the handling of sensitive information in logging-related output. The bulletin identifies the affected software versions but does not disclose additional technical details about the underlying implementation or specific exploitation conditions.
Vulnerability details:
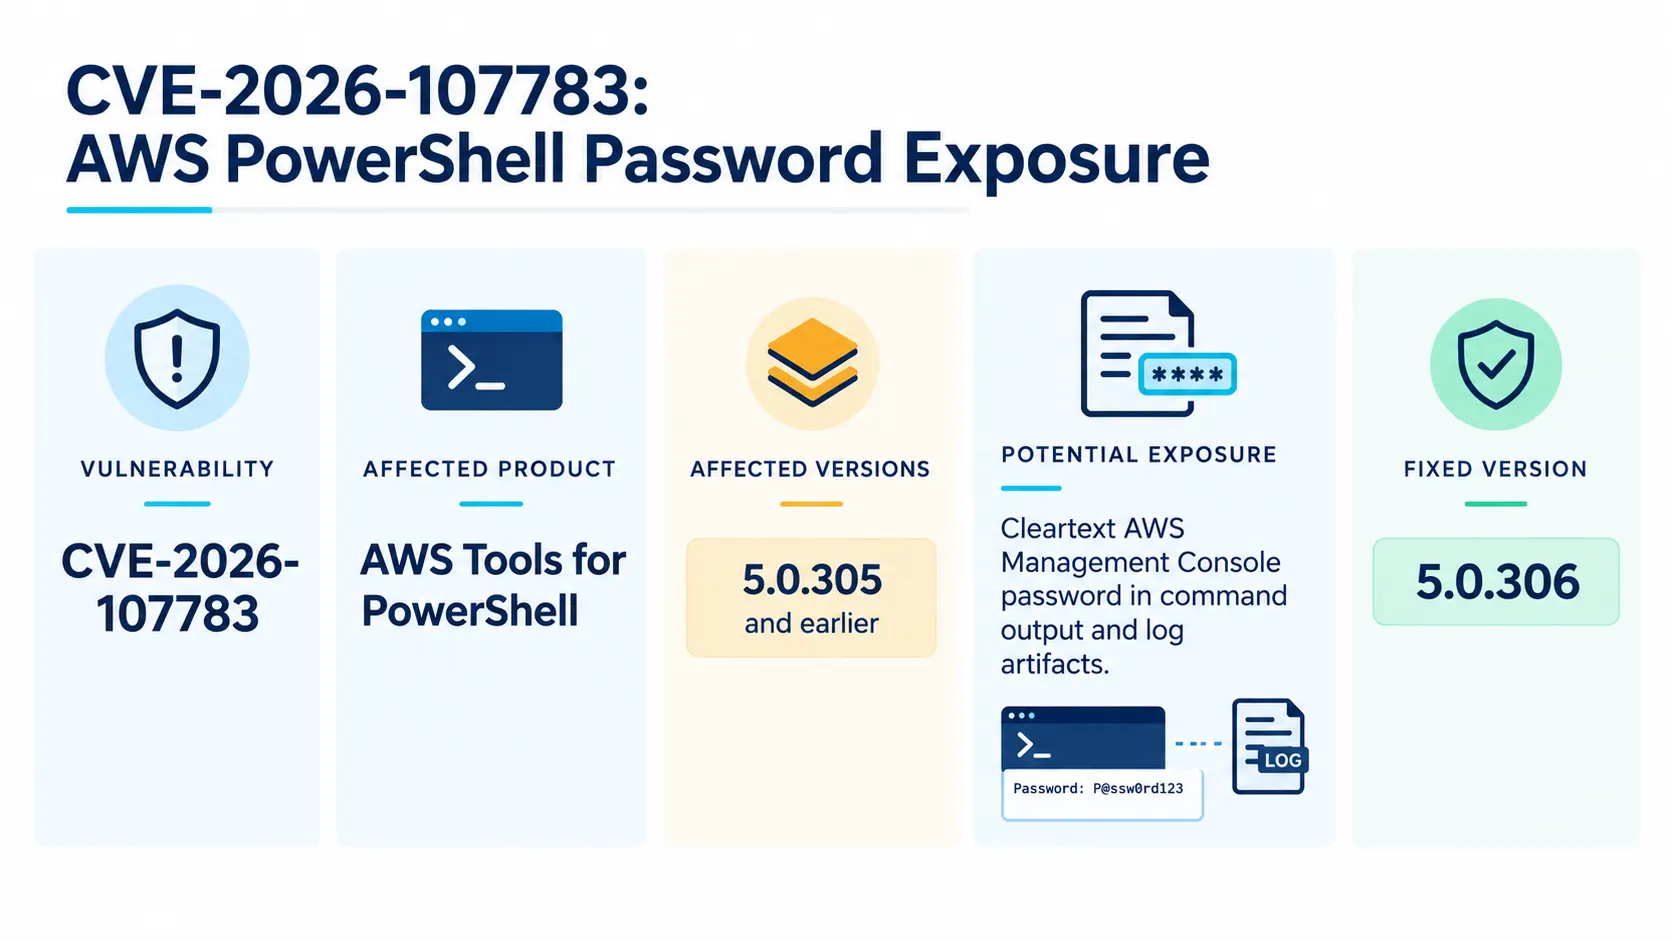
CVE ID: CVE-2026-107783
Bulletin ID: 2026-132-AWS
Affected product: AWS Tools for PowerShell
Affected versions: Version 5.0.305 and earlier
Fixed version: 5.0.306
Publication date: October 9, 2026
Severity classification: Important, according to the AWS bulletin
How the Vulnerability Could Expose Passwords
The reported issue concerns sensitive information appearing in command output and log artifacts. If an IAM user's cleartext AWS Management Console password is present in these artifacts, a local user could potentially recover it.
This makes the vulnerability relevant to administrators who use PowerShell commands to manage AWS environments, particularly when command arguments contain sensitive information.
AWS specifically warns against using the -WhatIf or -Confirm parameters with cmdlets that contain sensitive information in their arguments when running affected versions.
These parameters are commonly associated with previewing or confirming command operations. For the affected AWS Tools for PowerShell versions, AWS advises avoiding their use with commands containing sensitive arguments.
The bulletin does not provide further details about the exact circumstances required to recover a password or the extent of any exploitation observed in the wild.
AWS Releases Version 5.0.306 Fix
AWS has addressed CVE-2026-107783 in AWS Tools for PowerShell version 5.0.306.
The company recommends upgrading to the latest available version. It also advises organizations maintaining forked or derivative versions of the code to incorporate the new fixes.
Administrators should review the versions installed across their environments and prioritize updating systems that run version 5.0.305 or earlier.
Organizations that maintain customized versions should also verify that their changes include the relevant security fix rather than relying solely on the upstream release.
Temporary Workaround for Affected Versions
For environments that cannot immediately upgrade, AWS provides a specific workaround.
Users running AWS Tools for PowerShell version 5.0.305 or earlier should avoid using -WhatIf or -Confirm with cmdlets whose arguments contain sensitive information.
This is a temporary precaution, not a replacement for installing the patched release. Upgrading to version 5.0.306 or later remains the recommended remediation.
What AWS Administrators Should Do
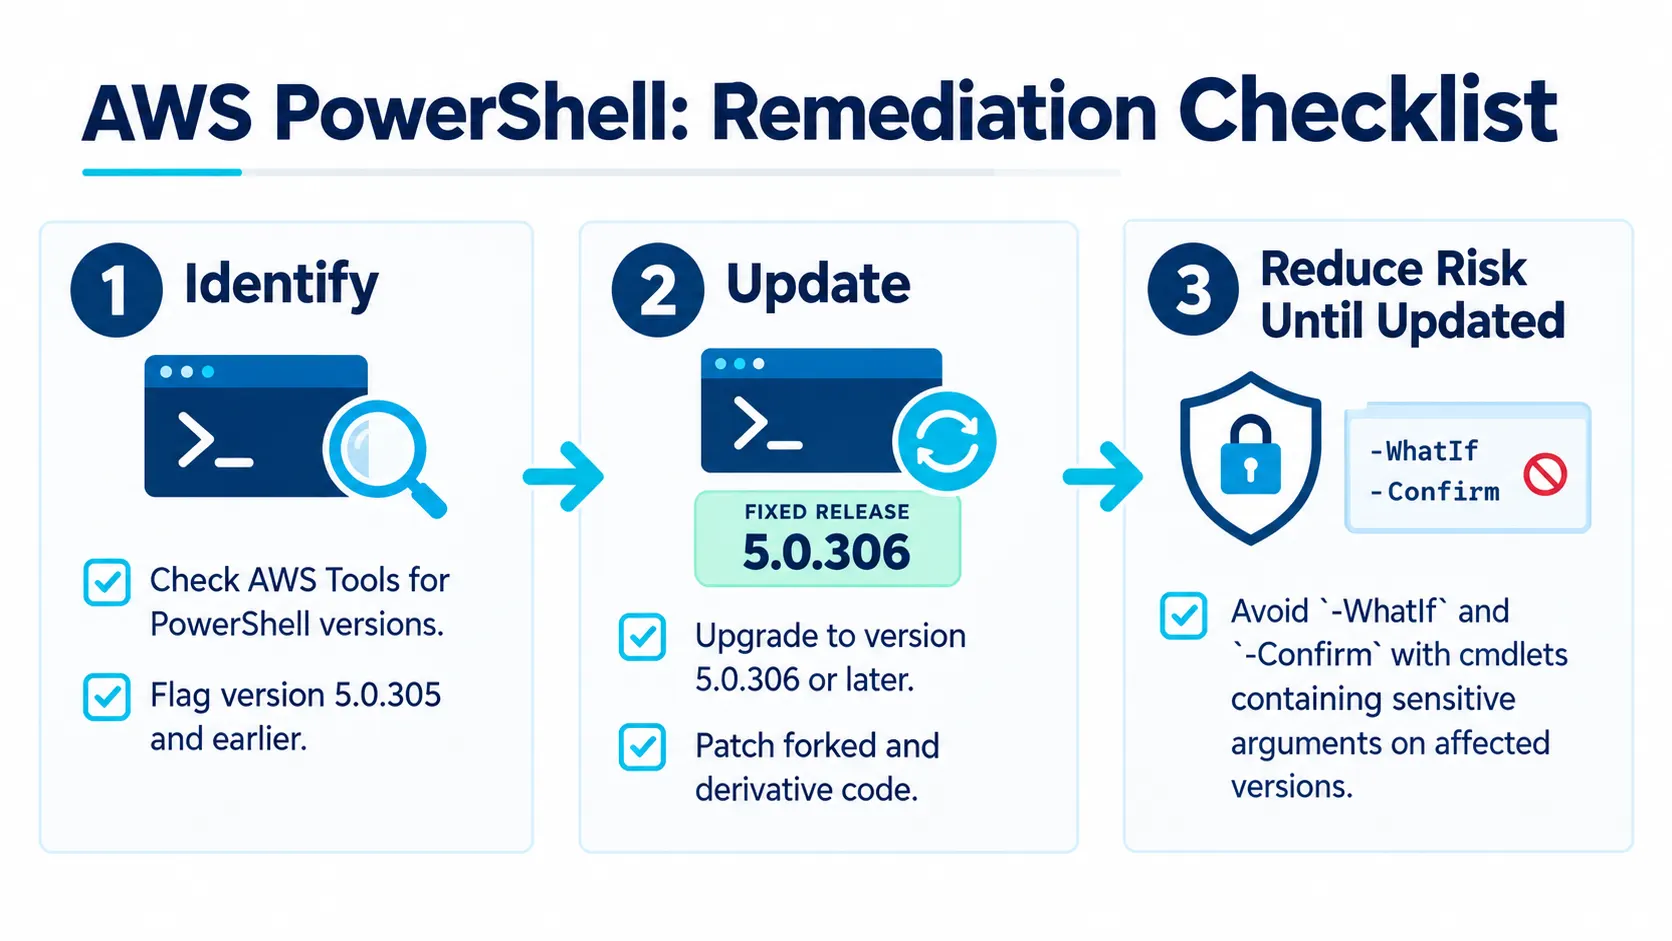
Organizations using AWS Tools for PowerShell should take the following steps:
Check installed versions. Identify systems running AWS Tools for PowerShell version 5.0.305 or earlier.
Upgrade the affected installations. Install version 5.0.306 or the latest available release.
Review customized code. Ensure forked and derivative versions incorporate the security fix.
Apply the workaround if necessary. Until an upgrade is completed, avoid using
-WhatIfor-Confirmwith cmdlets containing sensitive arguments on affected versions.Review relevant logs and command output. As a precaution, assess whether sensitive information may have been recorded in accessible artifacts. AWS does not specify a separate log-review procedure in the bulletin.
The bulletin does not disclose whether attackers have exploited the vulnerability in real-world environments or provide a confirmed count of affected users or systems.
Conclusion
CVE-2026-107783 highlights the security risks that can arise when sensitive credentials appear in command output or log artifacts. AWS has released a fix in AWS Tools for PowerShell version 5.0.306 and recommends upgrading to the latest version.
Administrators should check their installed versions, patch affected environments, and apply AWS's temporary workaround wherever immediate remediation is not possible.
Official references:
Source: Amazon Web Services (AWS)
About the Author