
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 371
- Trending now
- 5
- Breaking
- Live
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
 Trending
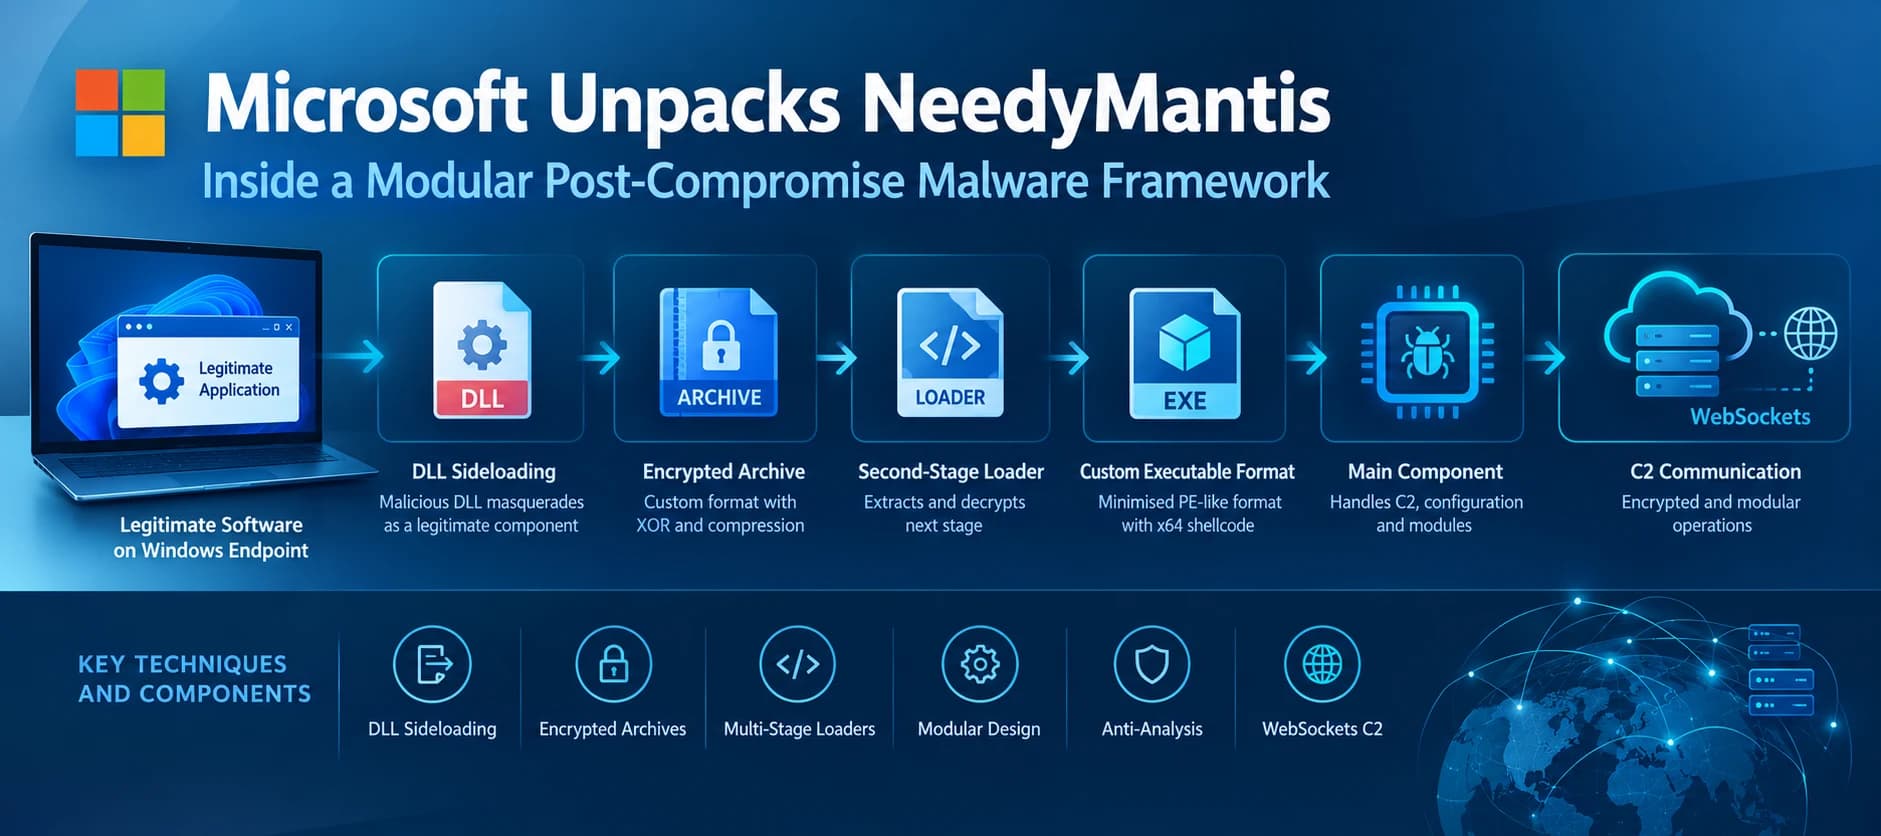
Microsoft Unpacks NeedyMantis, a Modular Post-Compromise Malware Family
Microsoft Threat Intelligence has detailed NeedyMantis, a modular post-compromise malware family used in targeted operations. The malware combines DLL sideloading, custom encrypted archives, multi-stage loaders and modular C2 capabilities.
 Trending
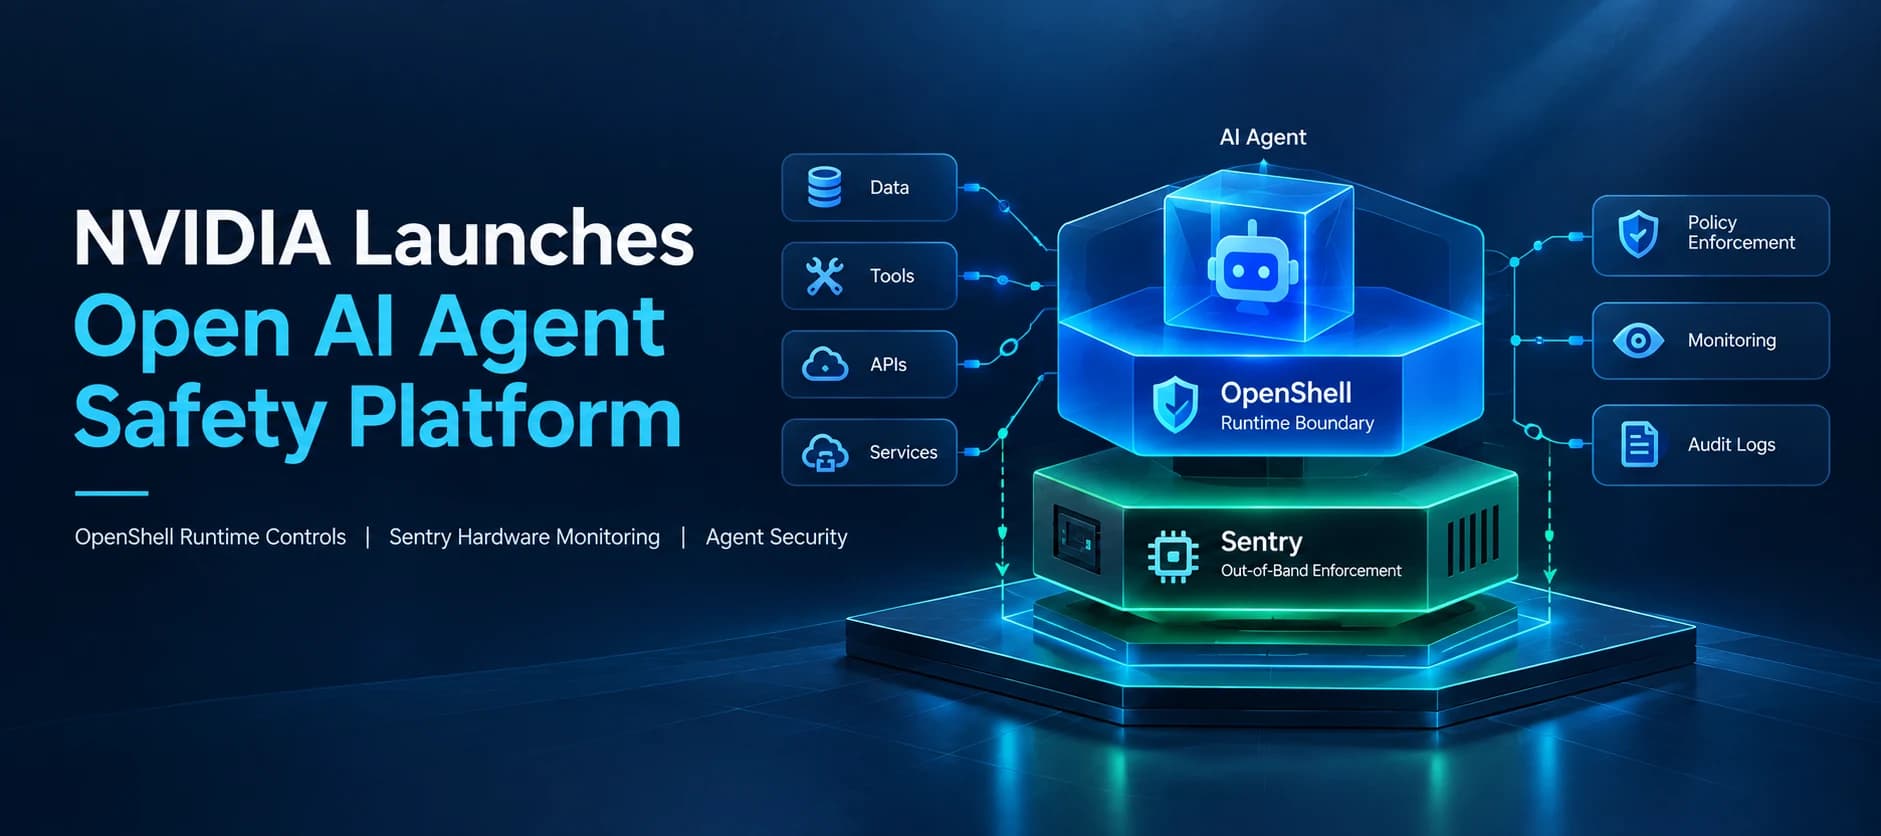
NVIDIA Launches Open Agent Safety Platform to Secure AI Agents From Testing to Deployment
NVIDIA has launched an open agent safety platform combining OpenShell runtime controls with the Sentry reference design to enforce boundaries, monitor behavior and govern AI agents across software, compute and robotics.
 Trending
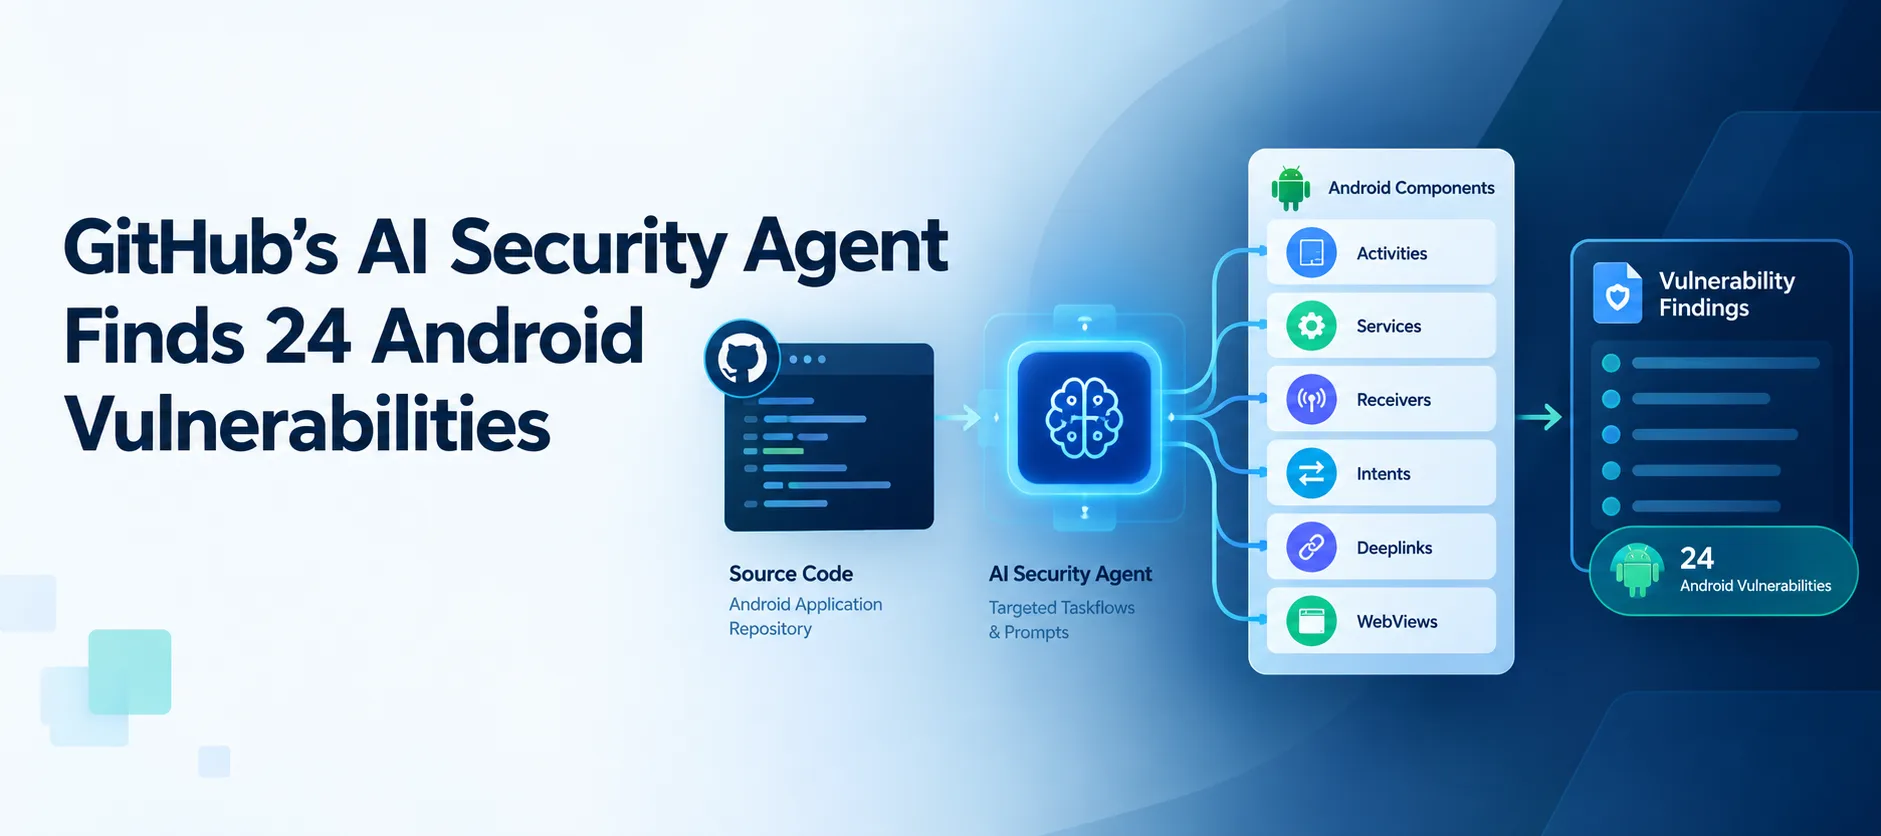
GitHub’s Open-Source AI Security Agent Finds 24 Android Vulnerabilities
GitHub Security Lab reports 24 Android vulnerabilities found with targeted AI security taskflows, showing how structured LLM workflows can support vulnerability research while still requiring human validation.
 Trending
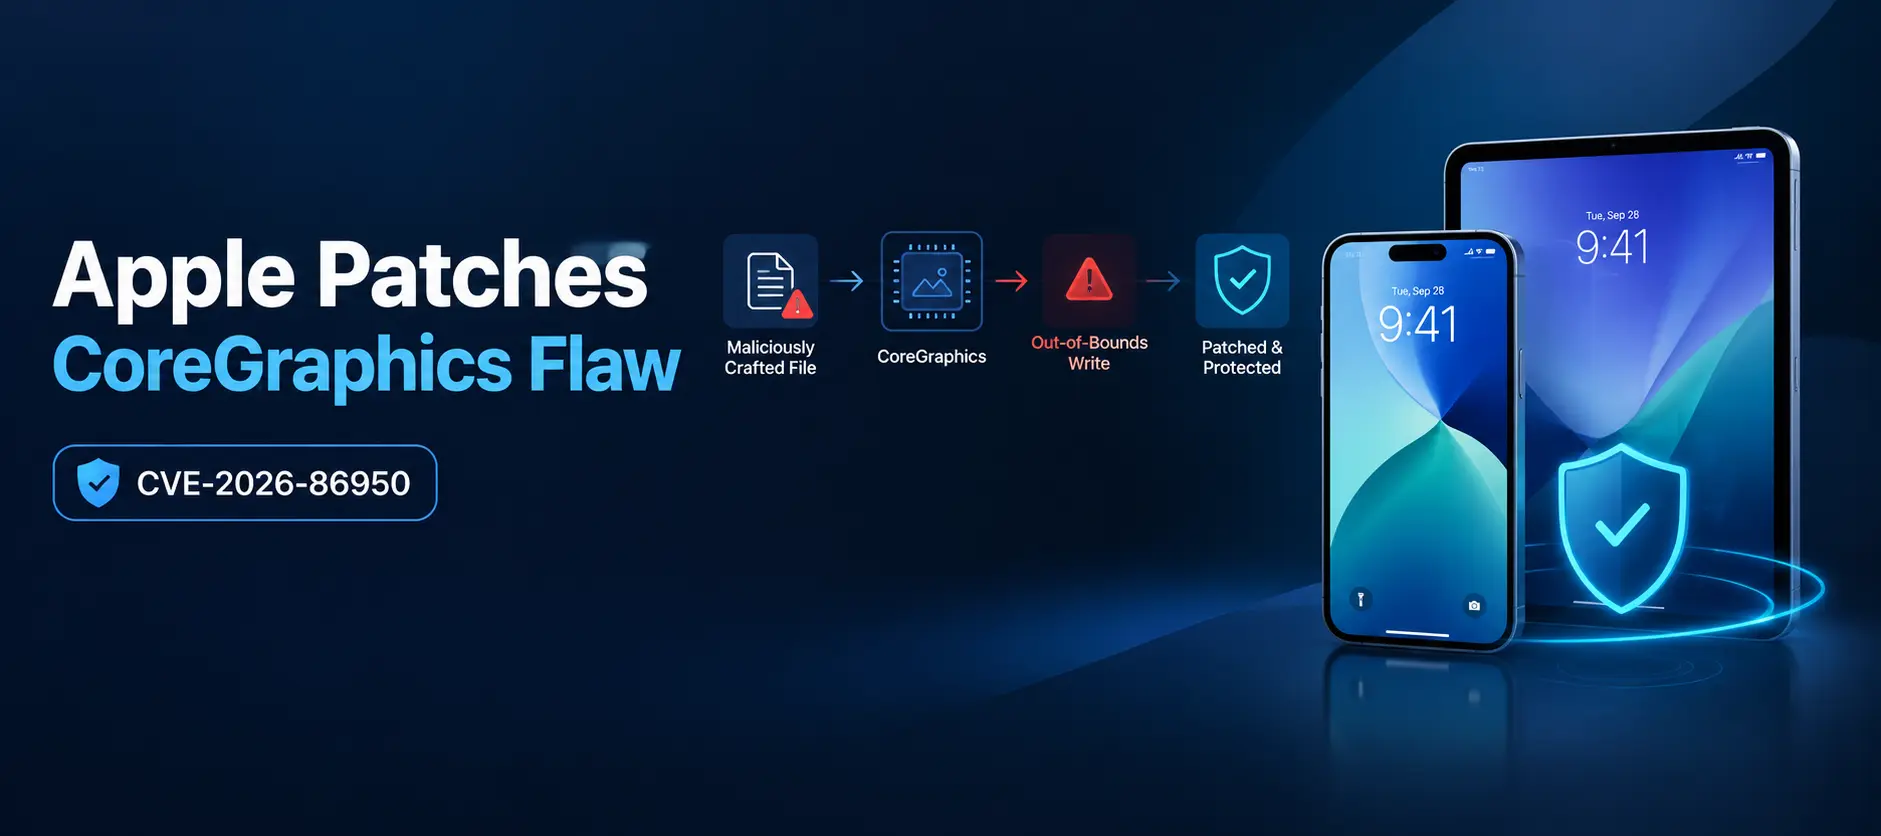
Apple Patches CoreGraphics Vulnerability in iOS 26.7.1 and iPadOS 26.7.1
Apple has released iOS 26.7.1 and iPadOS 26.7.1 to address a CoreGraphics vulnerability that could enable arbitrary code execution. Apple says the flaw may have been exploited in a sophisticated targeted attack.
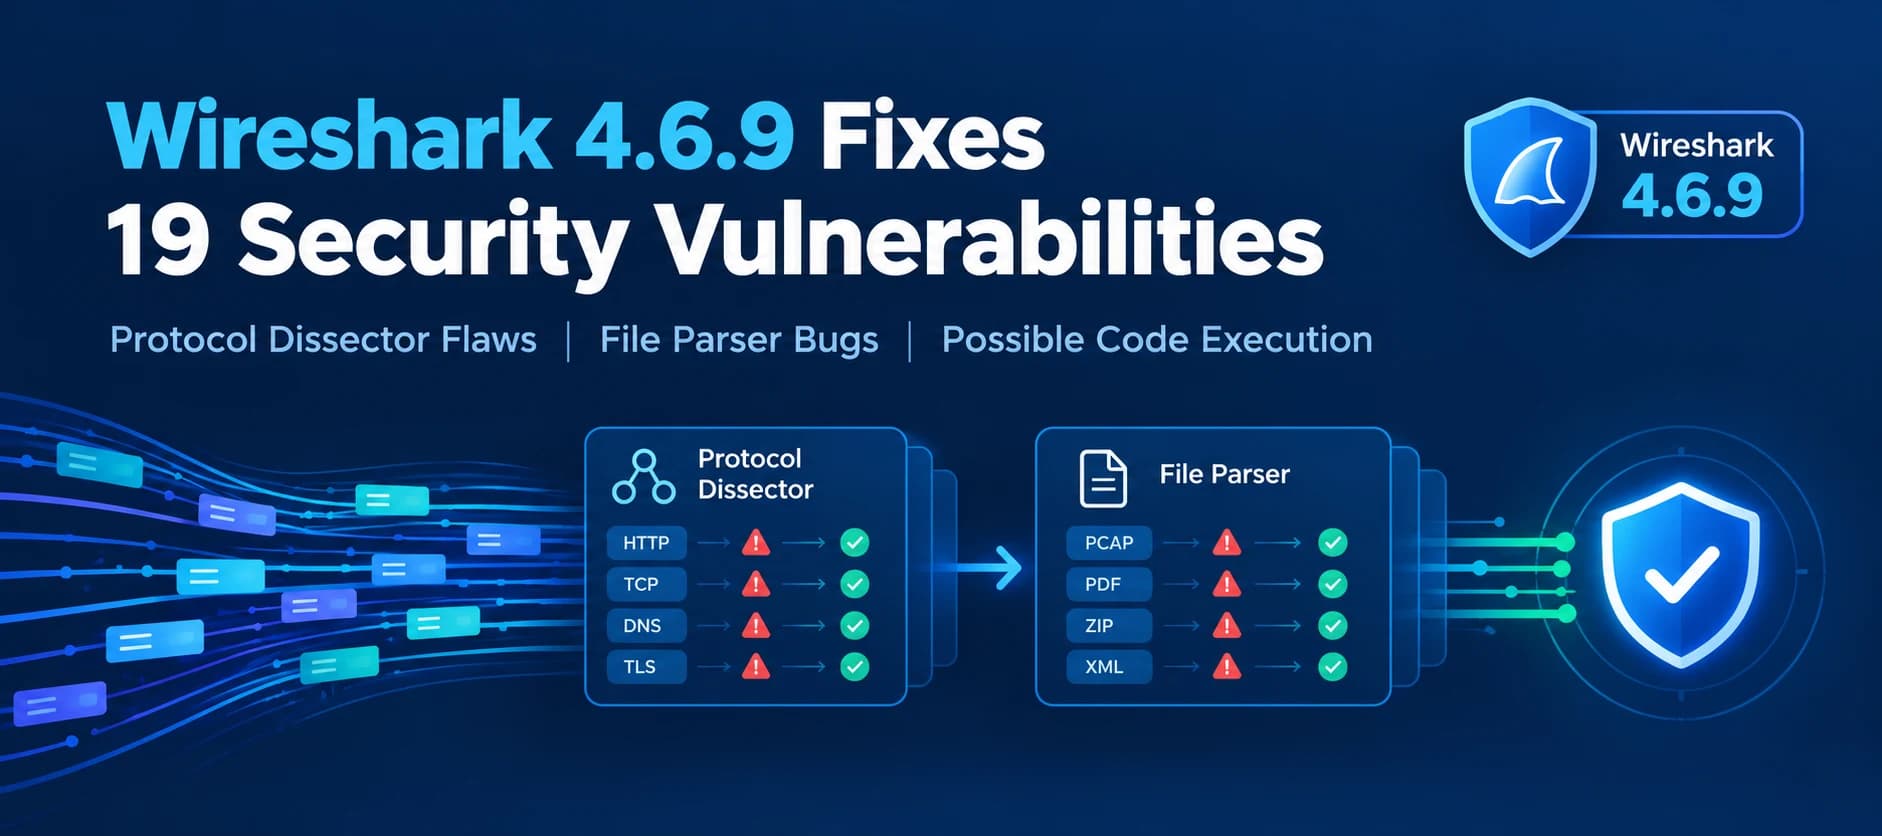
Wireshark 4.6.9 Fixes 19 Security Vulnerabilities, Including a Profile Import Flaw
Wireshark 4.6.9 addresses 19 security vulnerabilities, including crashes, infinite loops, memory leaks, and a profile import flaw with possible code execution. The release also fixes additional bugs across protocol analysis and capture-file handling.
 Trending
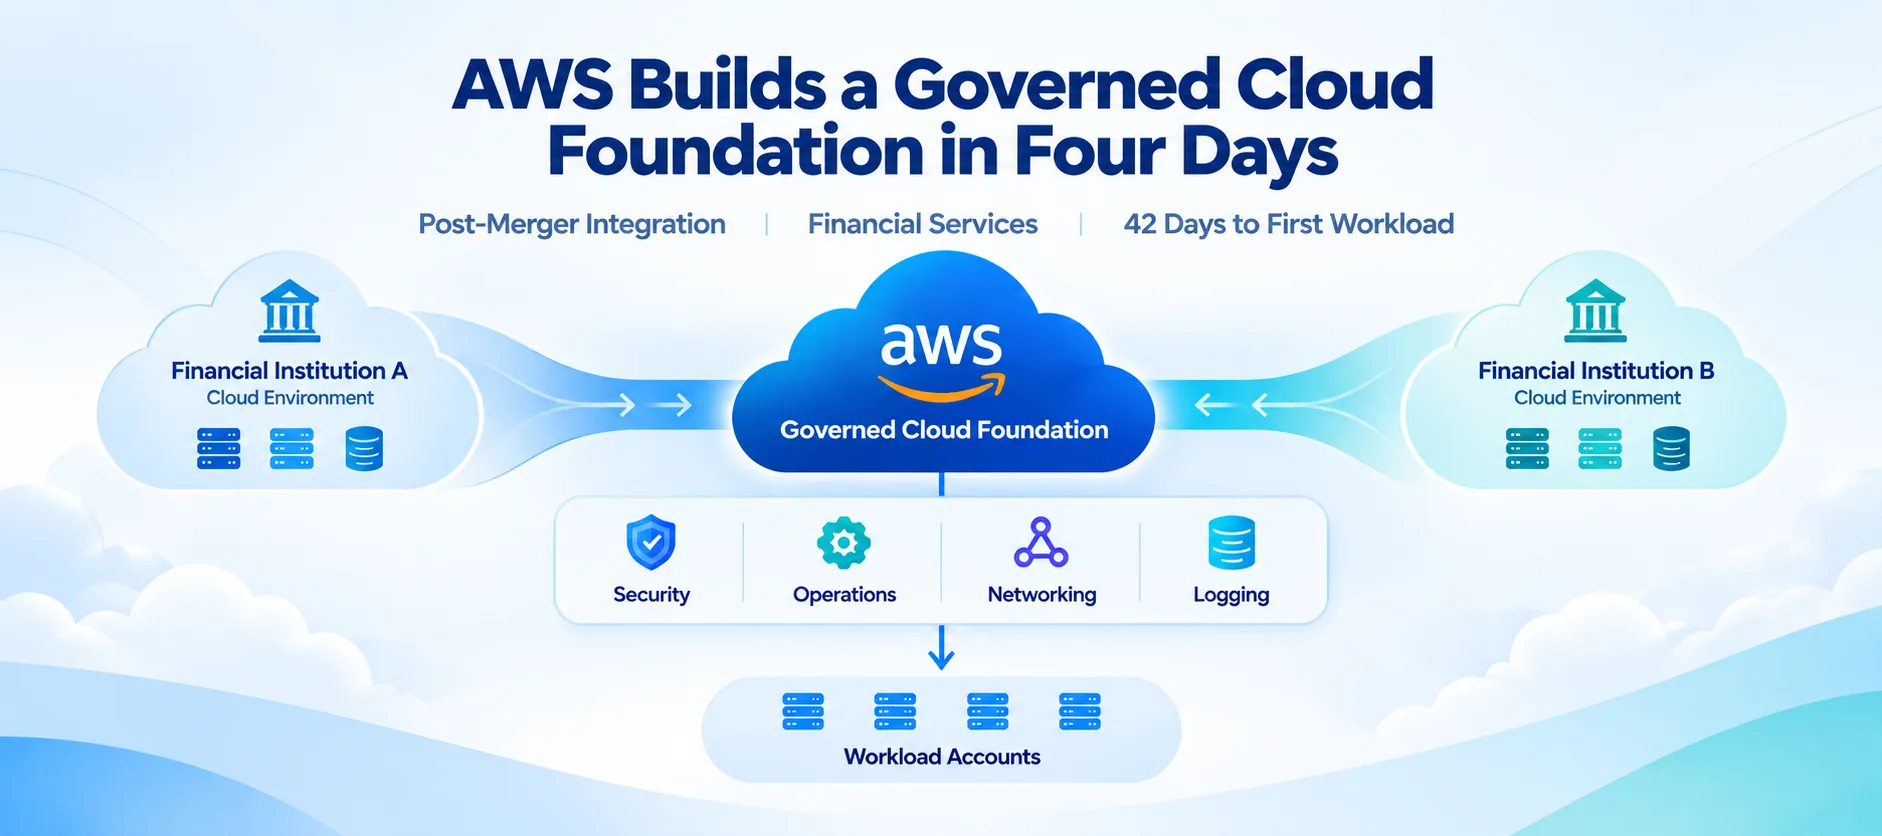
AWS Details Post-Merger Cloud Foundation Built in Four Days for a U.S. Bank
AWS describes how a U.S. bank established a governed cloud organization four days after a merger closed, enabled a nine-service security baseline in under 10 minutes, and vended its first workload accounts after 42 days.
 Trending
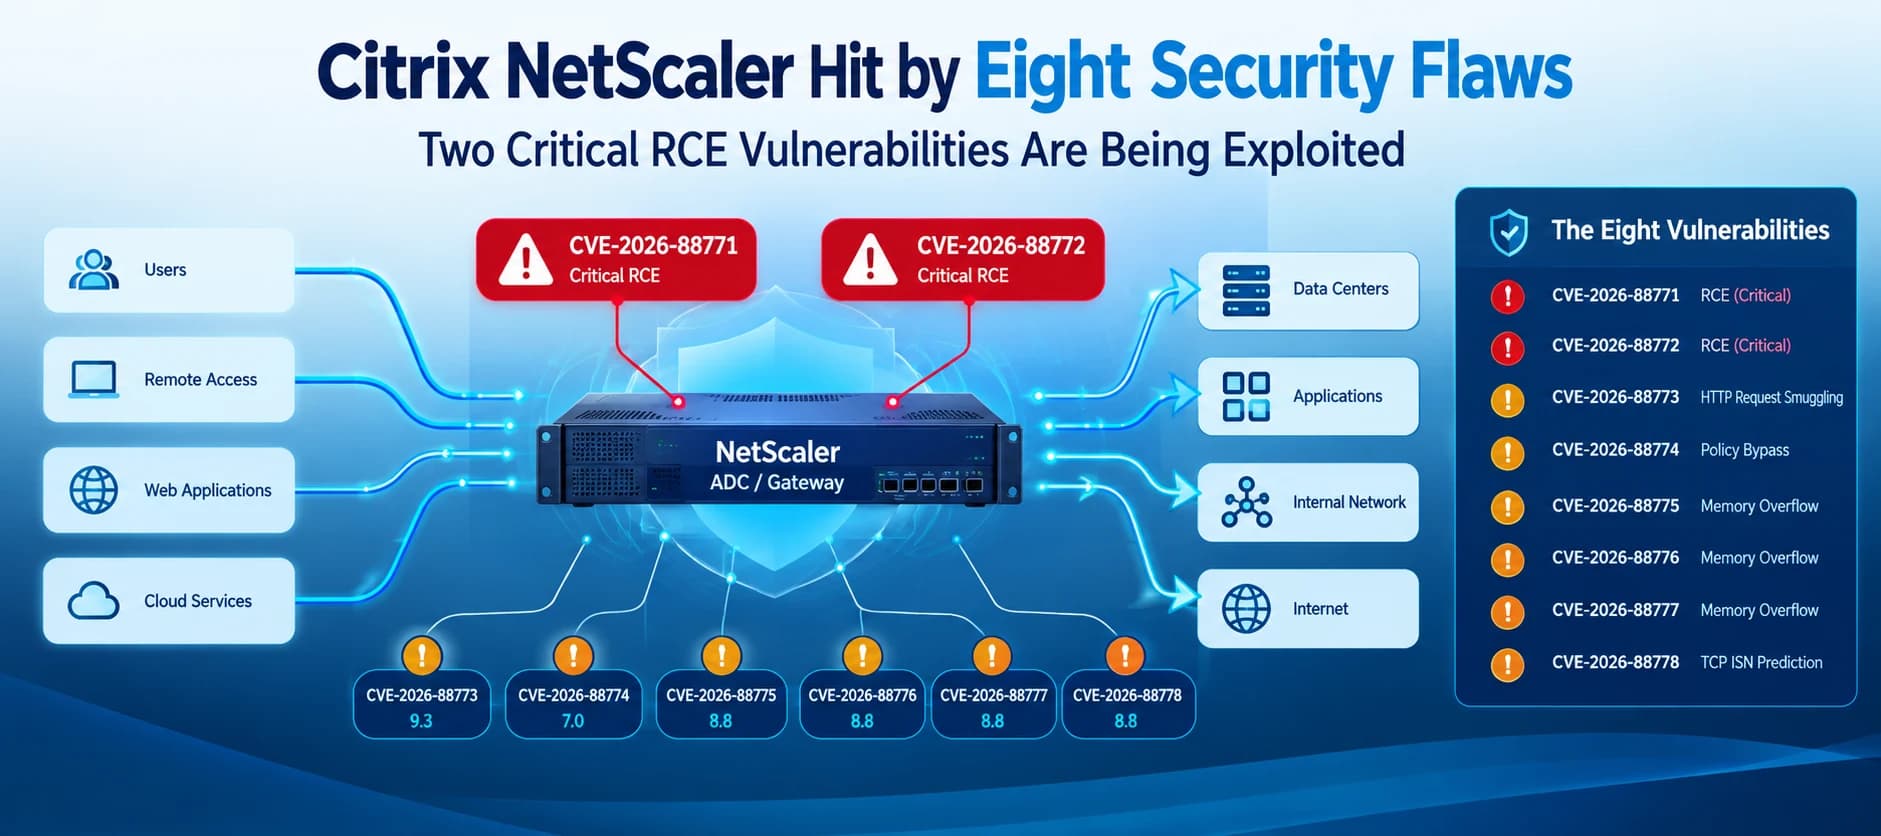
Citrix NetScaler Security Update Fixes Eight Vulnerabilities, Including Two Exploited RCE Flaws
Citrix has disclosed eight NetScaler ADC and Gateway vulnerabilities, including two critical remote code execution flaws that have been exploited on unmitigated deployments. Customers are urged to upgrade to fixed builds.
 Trending
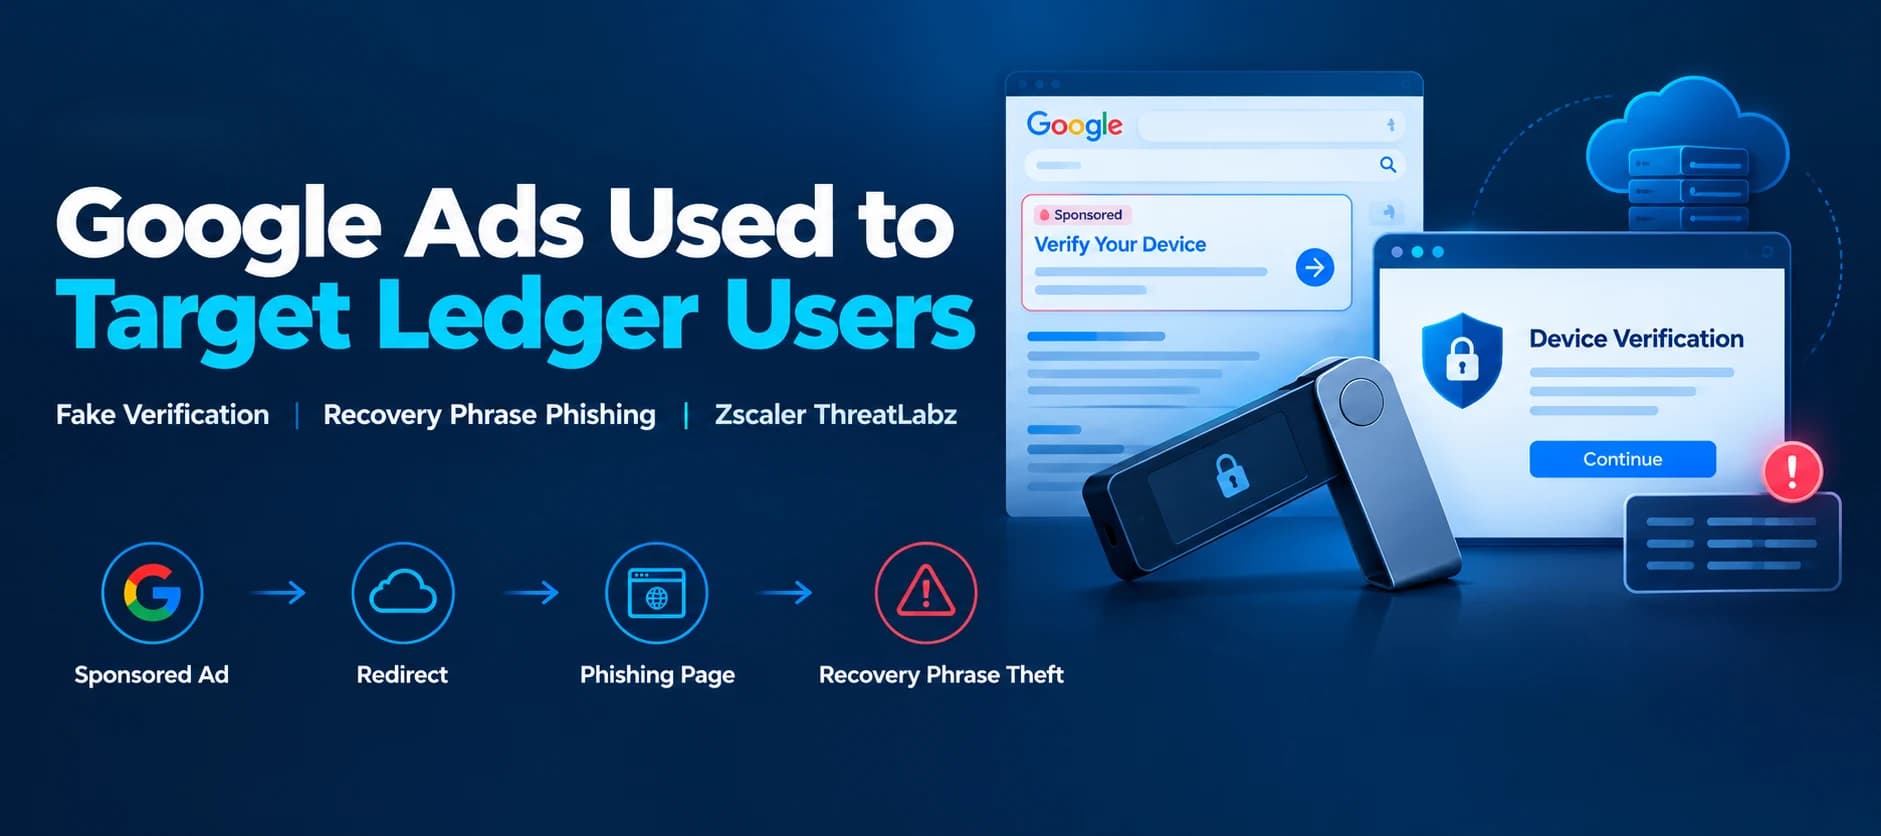
Threat Actors Use Google Ads to Target Ledger Users With Recovery Phrase Phishing
Zscaler ThreatLabz has uncovered a phishing campaign using fraudulent Google ads, Google Cloud Storage, Vercel and Google Sites to impersonate Ledger and trick users into submitting secret recovery phrases.
 Trending
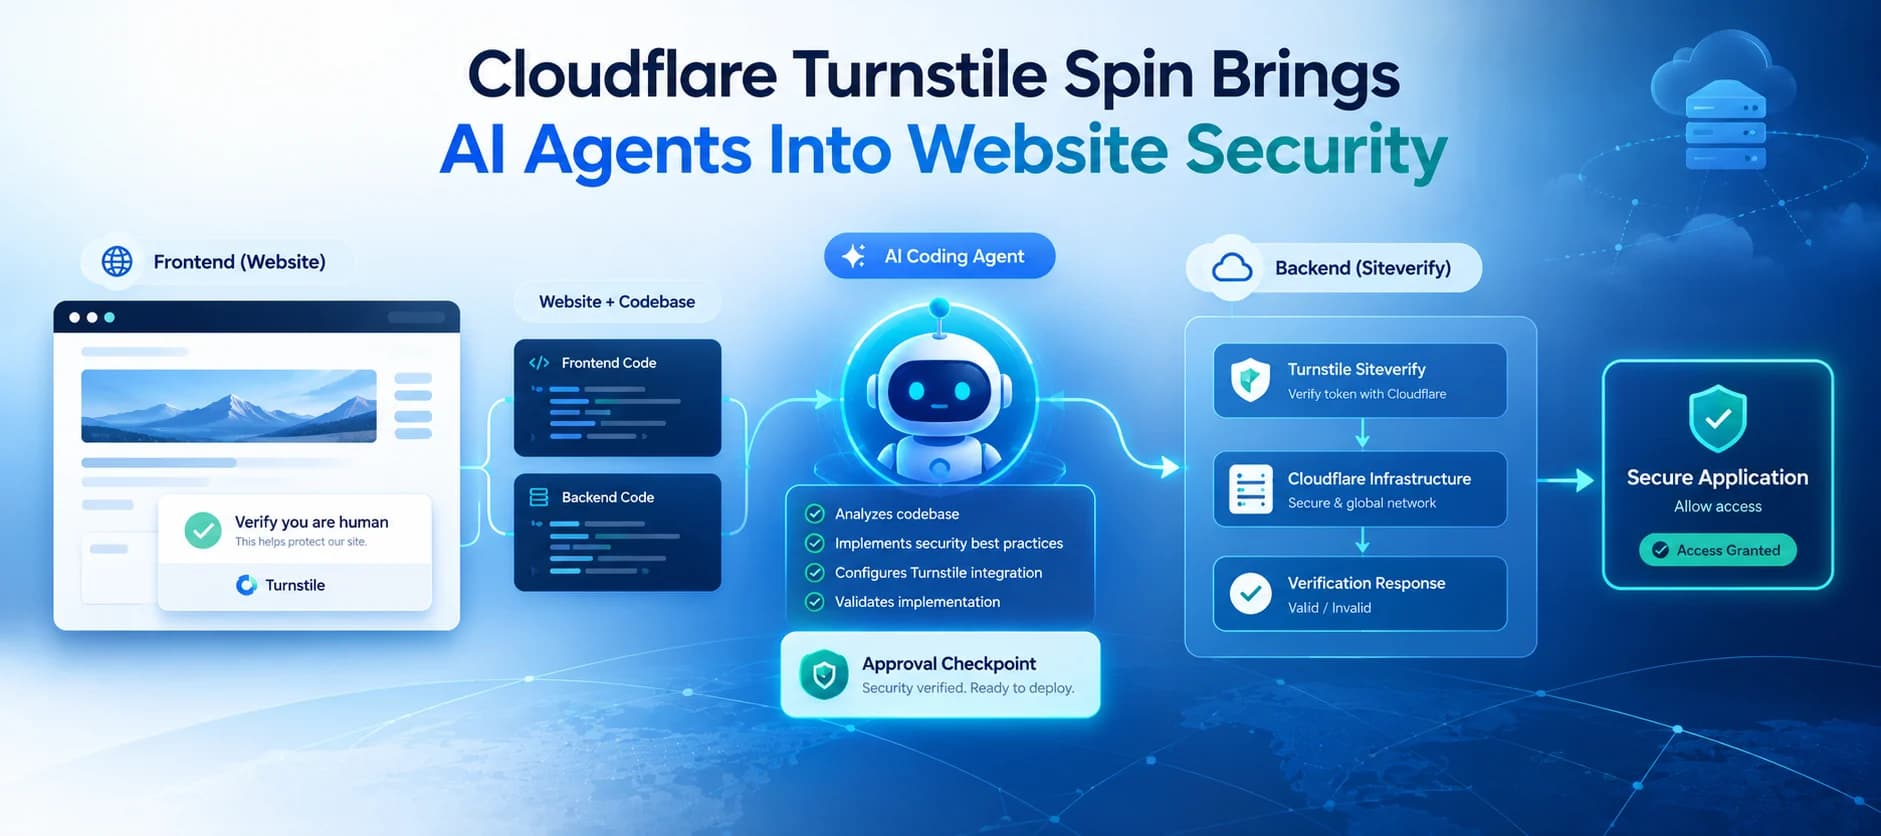
Cloudflare Launches Turnstile Spin to Help AI Agents Secure Websites
Cloudflare has introduced Turnstile Spin, an agent-mediated workflow that lets AI coding agents install, repair, or migrate Turnstile protection across a website's frontend and backend.
 Trending
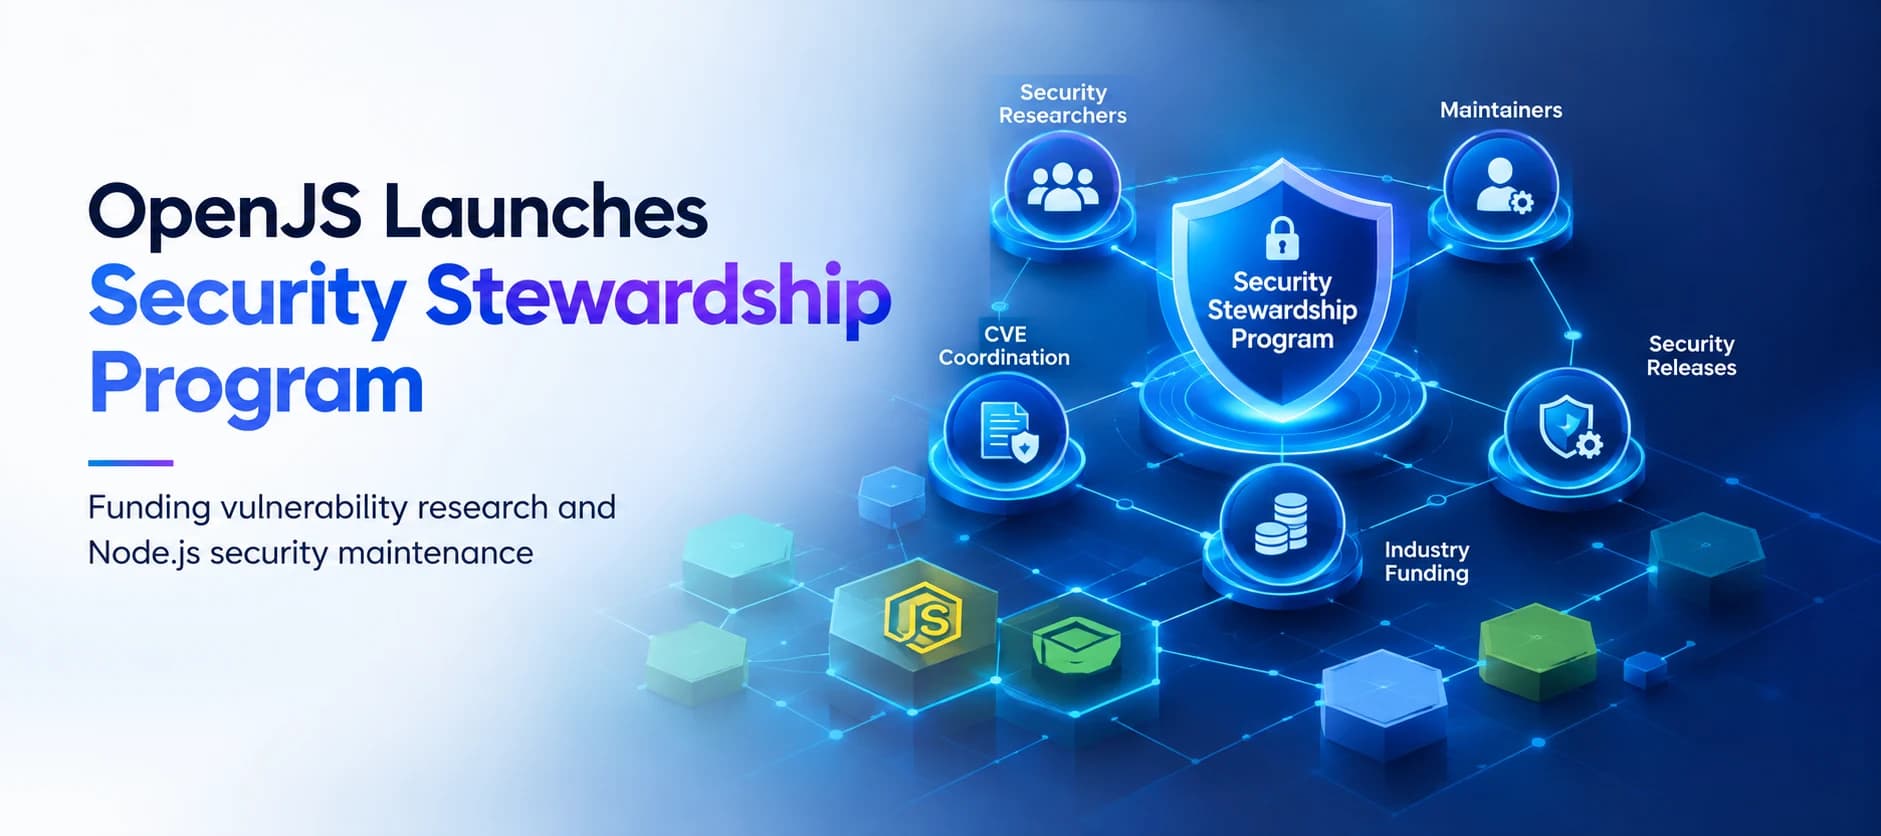
OpenJS Foundation Launches Security Stewardship Program to Fund Node.js Vulnerability Work
The OpenJS Foundation has launched a Security Stewardship Program that funds vulnerability research, CVE coordination and maintainer support, with Node.js as its initial focus.
 Trending
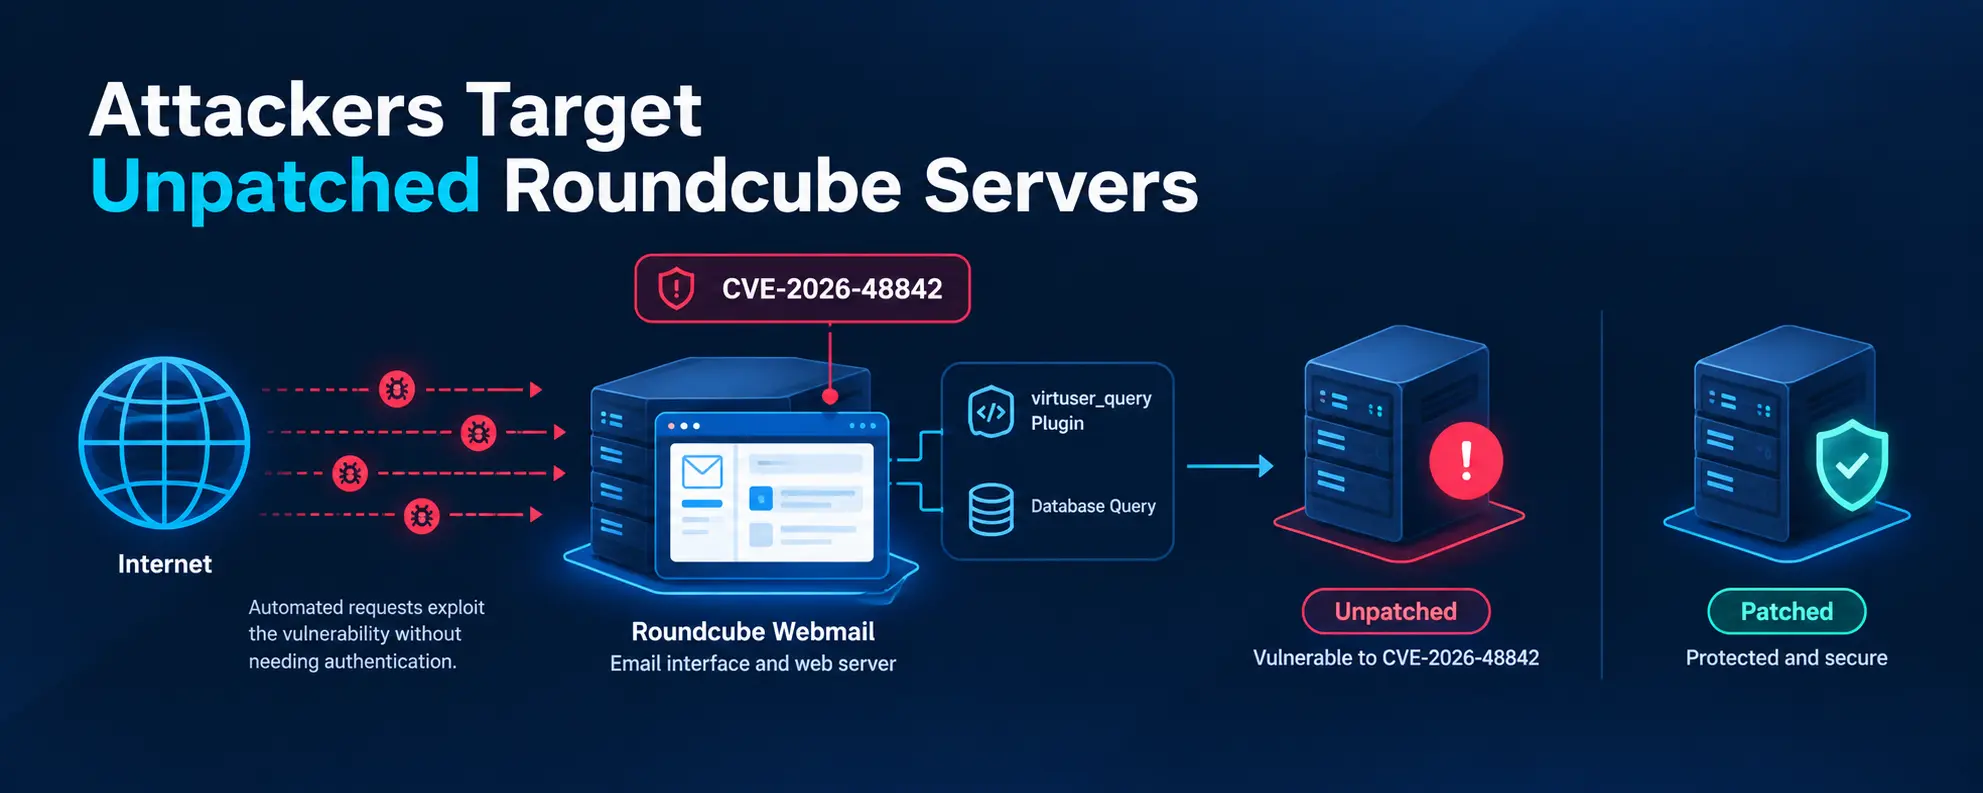
Attackers Target Unpatched Roundcube Servers With CVE-2026-48842
Attackers are actively exploiting CVE-2026-48842 against unpatched Roundcube servers. The high-severity flaw allows pre-authentication SQL injection, putting outdated webmail installations at risk.
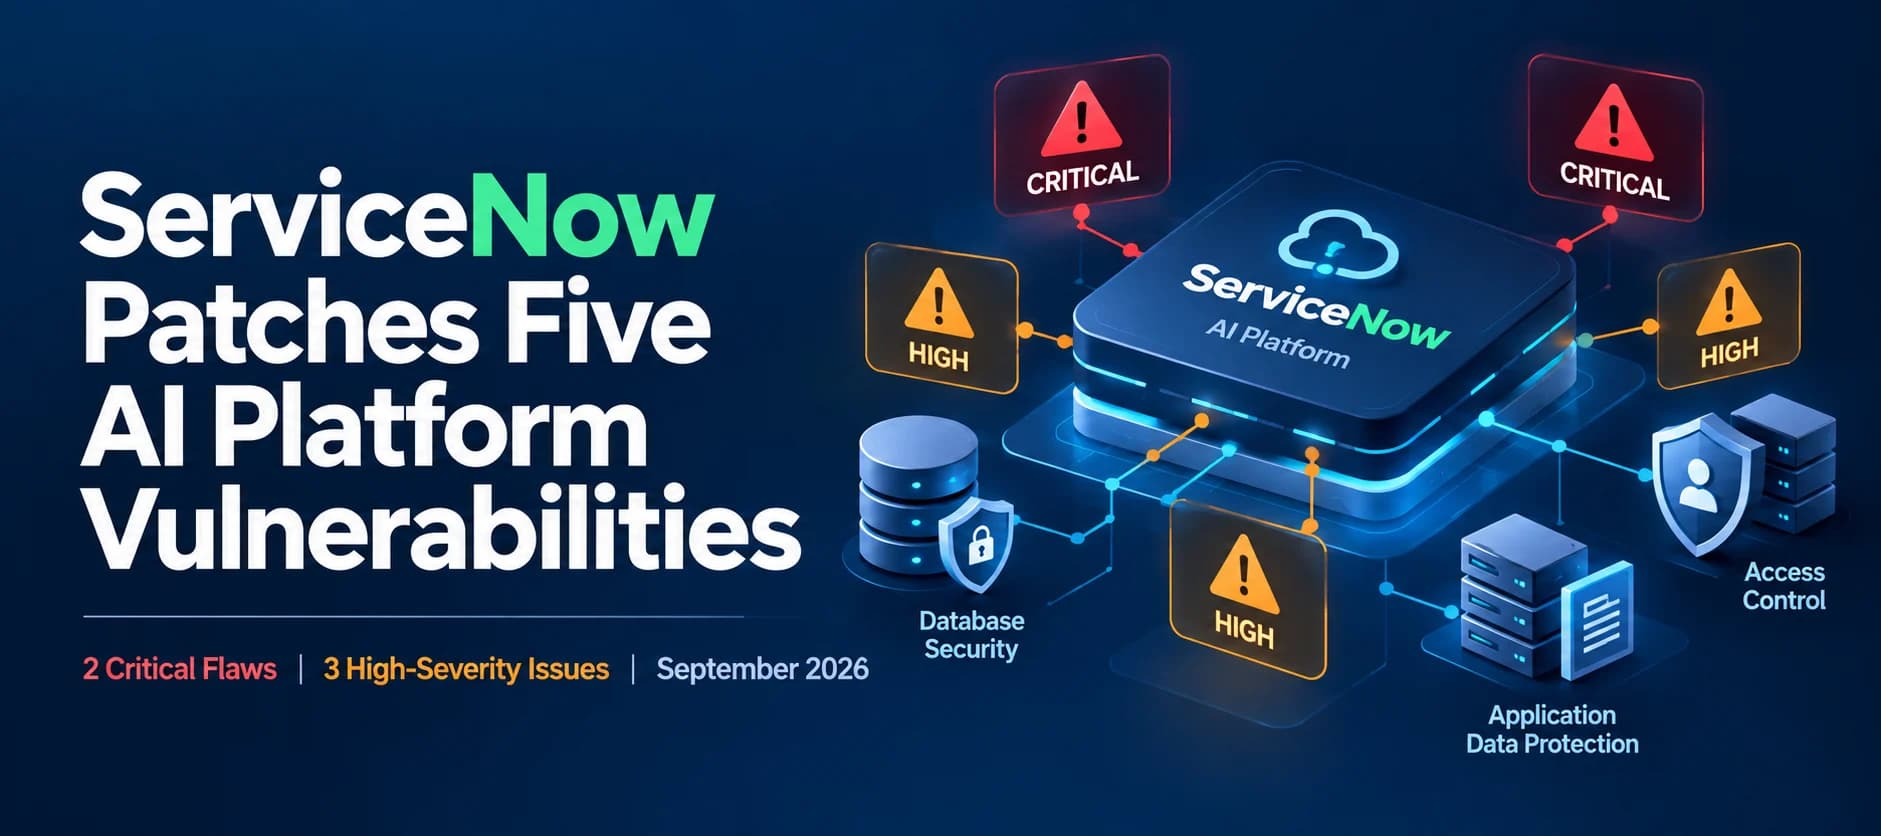
ServiceNow Patches Five AI Platform Vulnerabilities, Including Two Critical Flaws
ServiceNow has addressed five AI Platform vulnerabilities, including two critical flaws involving SQL injection and missing authorization. Canada's Cyber Centre urges administrators to check affected versions and apply the available security updates.