
Stay Ahead of the Tech Curve
Breaking cybersecurity threats, technology updates, and IT industry insights, curated by our editors.
- Stories published
- 371
- Trending now
- 5
- Breaking
- Live
Citrix Issues Critical NetScaler Security Update for CVE-2026-107406
Citrix has warned of a critical memory overflow vulnerability in NetScaler ADC and NetScaler Gateway that could lead to remote code execution or denial of service. The flaw carries a CVSS v4.0 score of 9.5, and affected customers are urged to upgrade.
 Trending
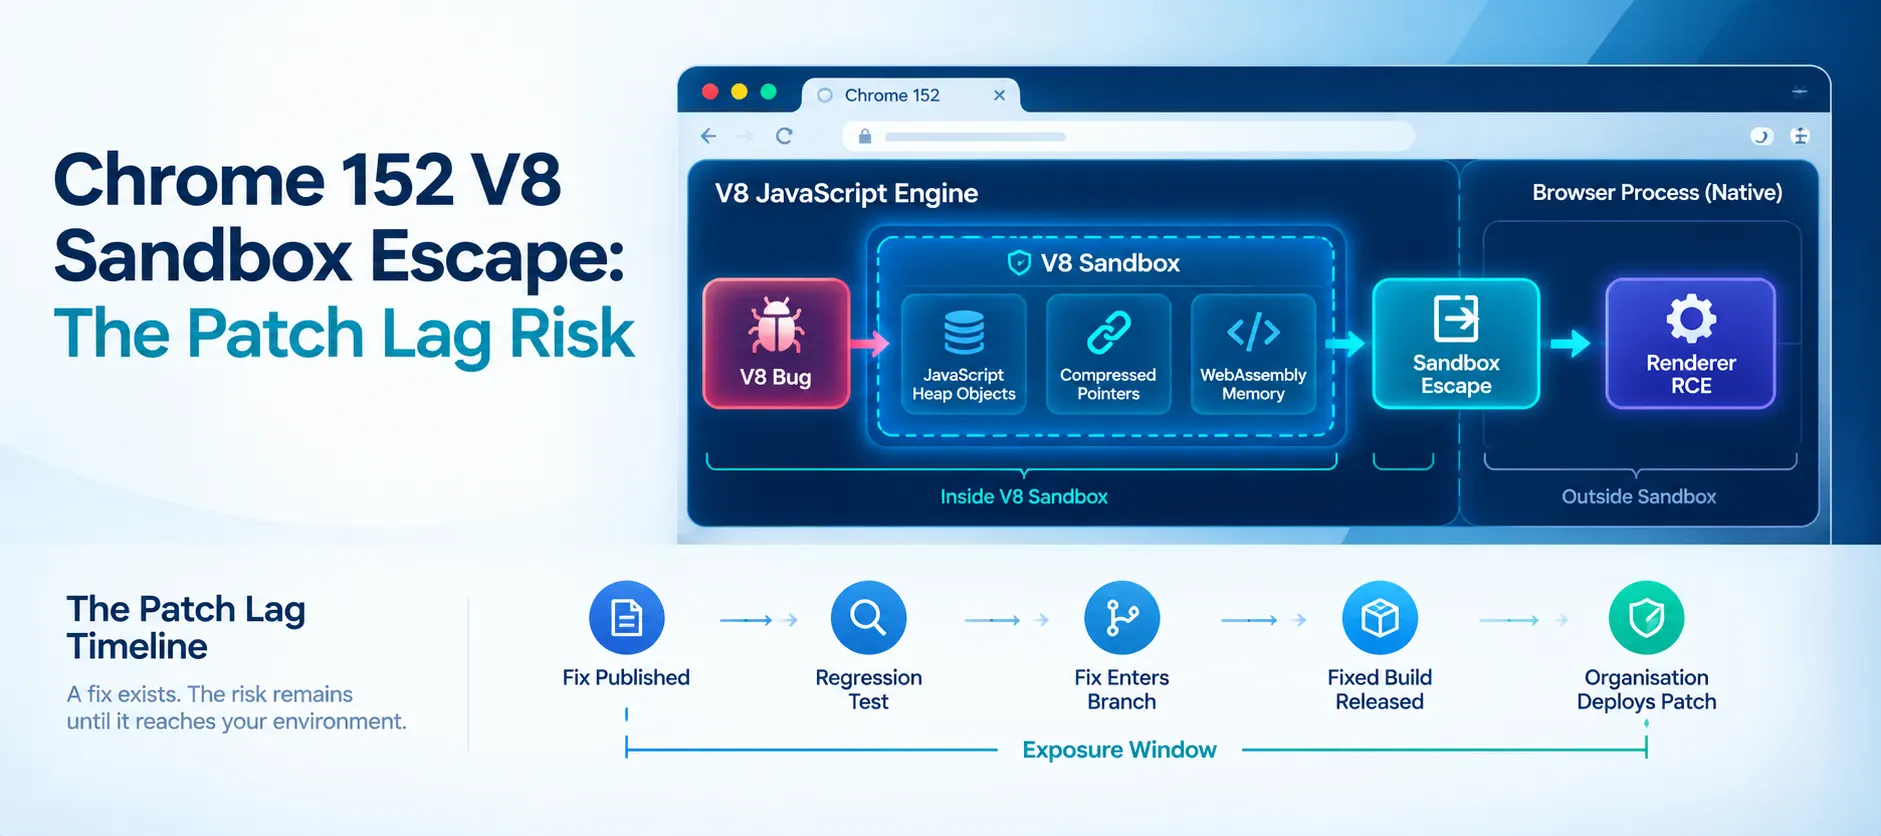
Chrome 152 V8 Sandbox Escape Shows the Risk of Patch Lag
BackBox AI says it built a complete Chrome 152 V8 exploit chain that moved from an address leak to sandbox escape, renderer RCE and file access, highlighting the security risks created by delayed patch deployment.
 Trending
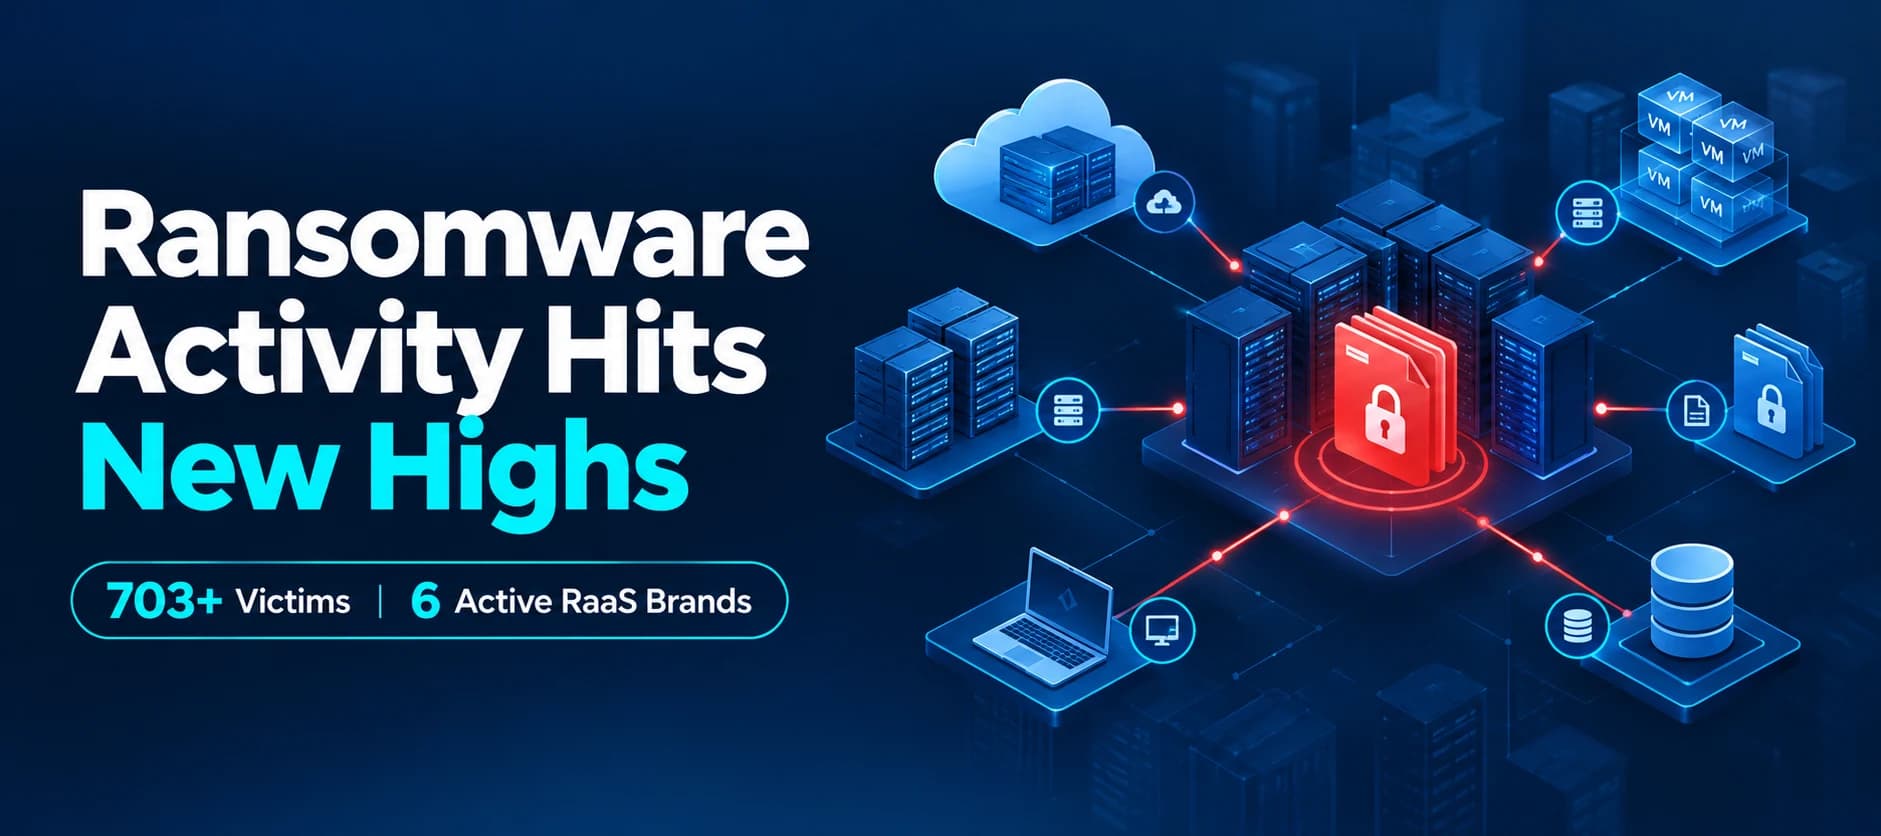
Ransomware Quarterly Report: 703+ Victims Across Six Active RaaS Brands
Insomnia's latest ransomware report tracks 703+ publicly named victims, six active RaaS brands and a 13-hour median time-to-encrypt, while highlighting intermittent encryption, Rust-based lockers and ESXi targeting.
 Trending
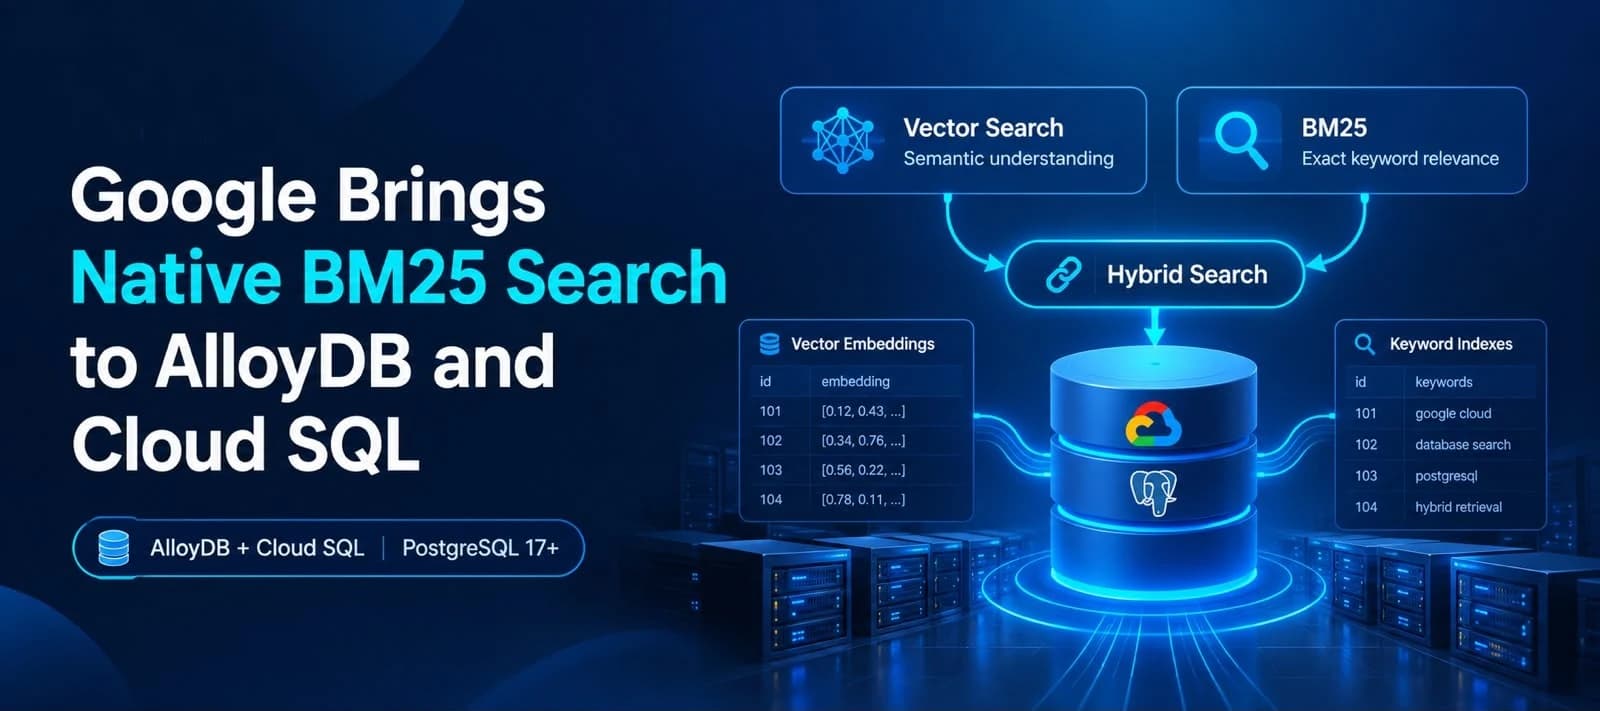
Google Brings Native BM25 Search to AlloyDB and Cloud SQL
Google is previewing native BM25 indexing in AlloyDB and Cloud SQL for PostgreSQL 17+, bringing keyword and vector search into the same database for hybrid AI search applications.
 Trending
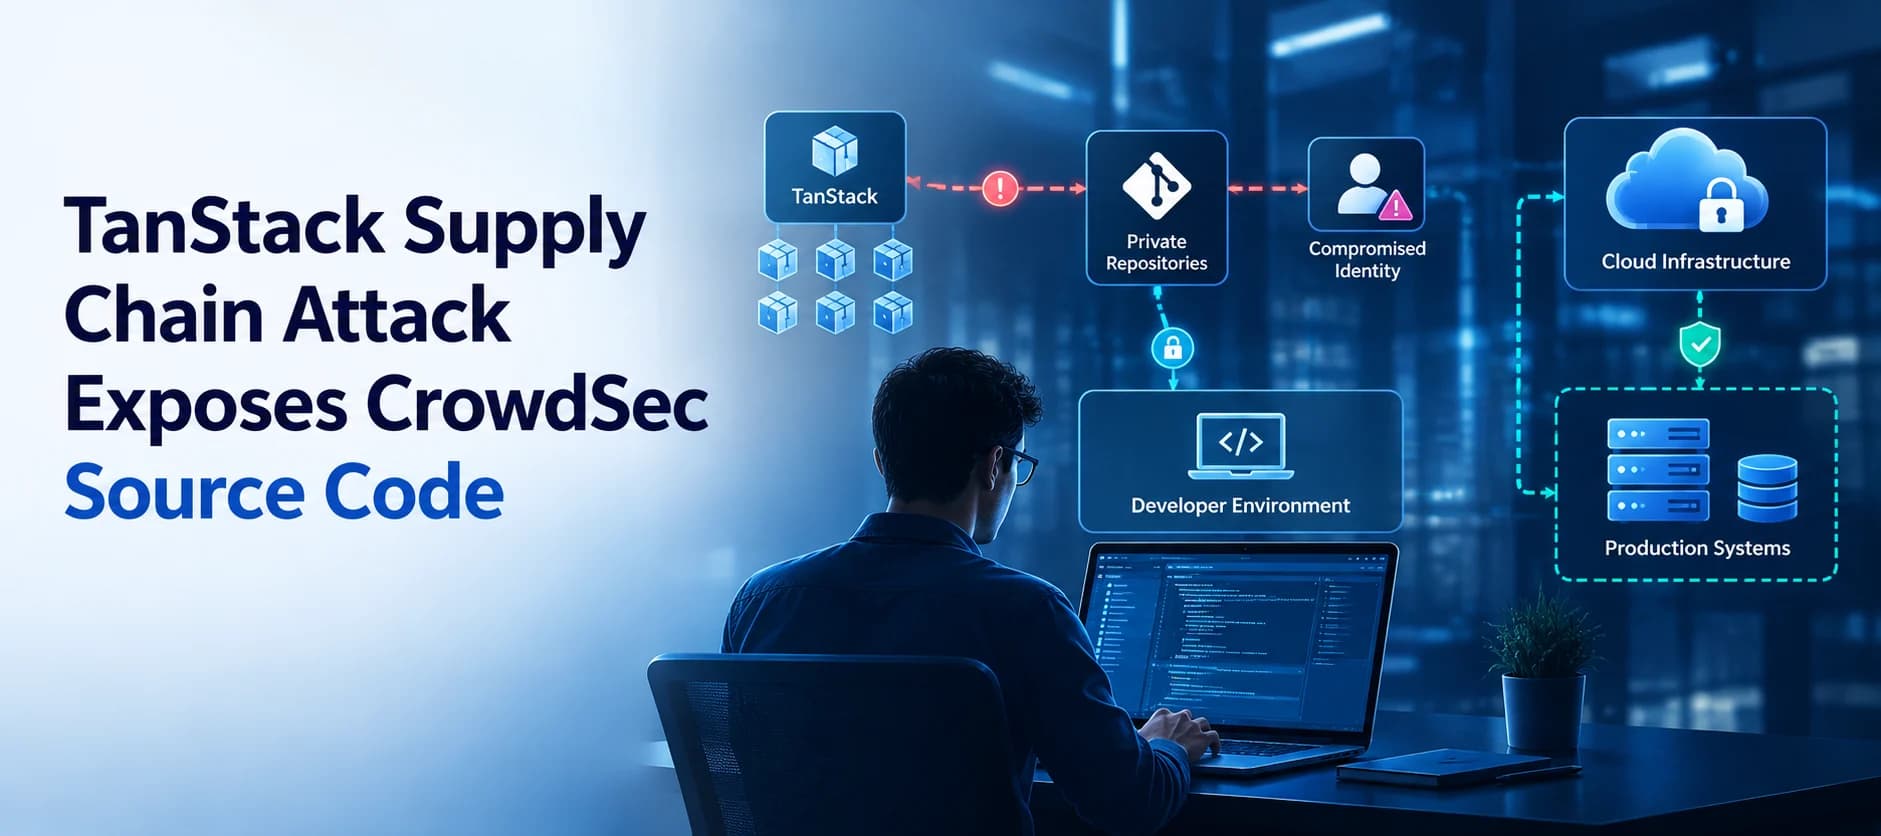
TanStack Supply Chain Attack Led to CrowdSec Source Code Leak, Investigation Finds
CrowdSec has traced its May 2026 source code exposure to a compromised former employee account linked to the TanStack supply chain attack. The company says its infrastructure, customer databases and code integrity remained unaffected.
 Trending
Click2Shell: WordPress Patches Theme Preview Flaw That Can Lead to Remote Code Execution
WordPress 7.1.1 fixes Click2Shell, a theme-preview flaw that can trigger unauthorised theme installation. Researchers at pwn.ai demonstrated how it could be chained with vulnerable theme code to achieve server-side PHP execution.
 Trending
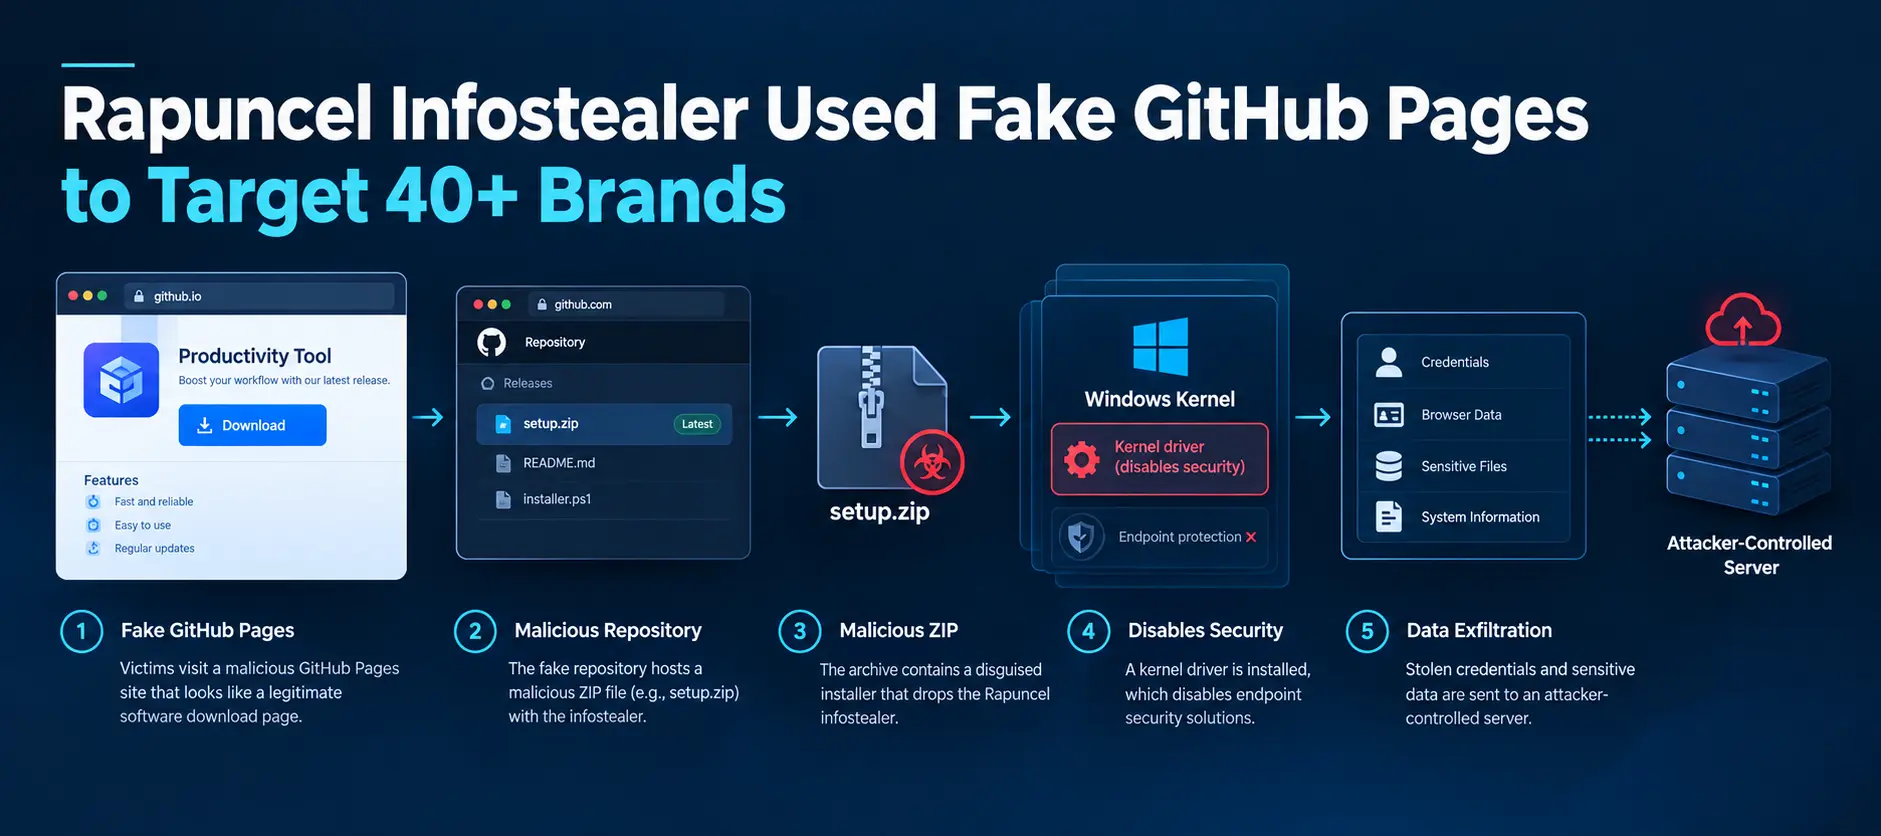
Rapuncel Infostealer Used Fake GitHub Pages to Target 40+ Brands
A LastPass and Delphos investigation uncovered a malware campaign using fake GitHub pages, SEO tactics and a Microsoft-attested kernel driver to distribute the Rapuncel infostealer and disable security software.
 Trending
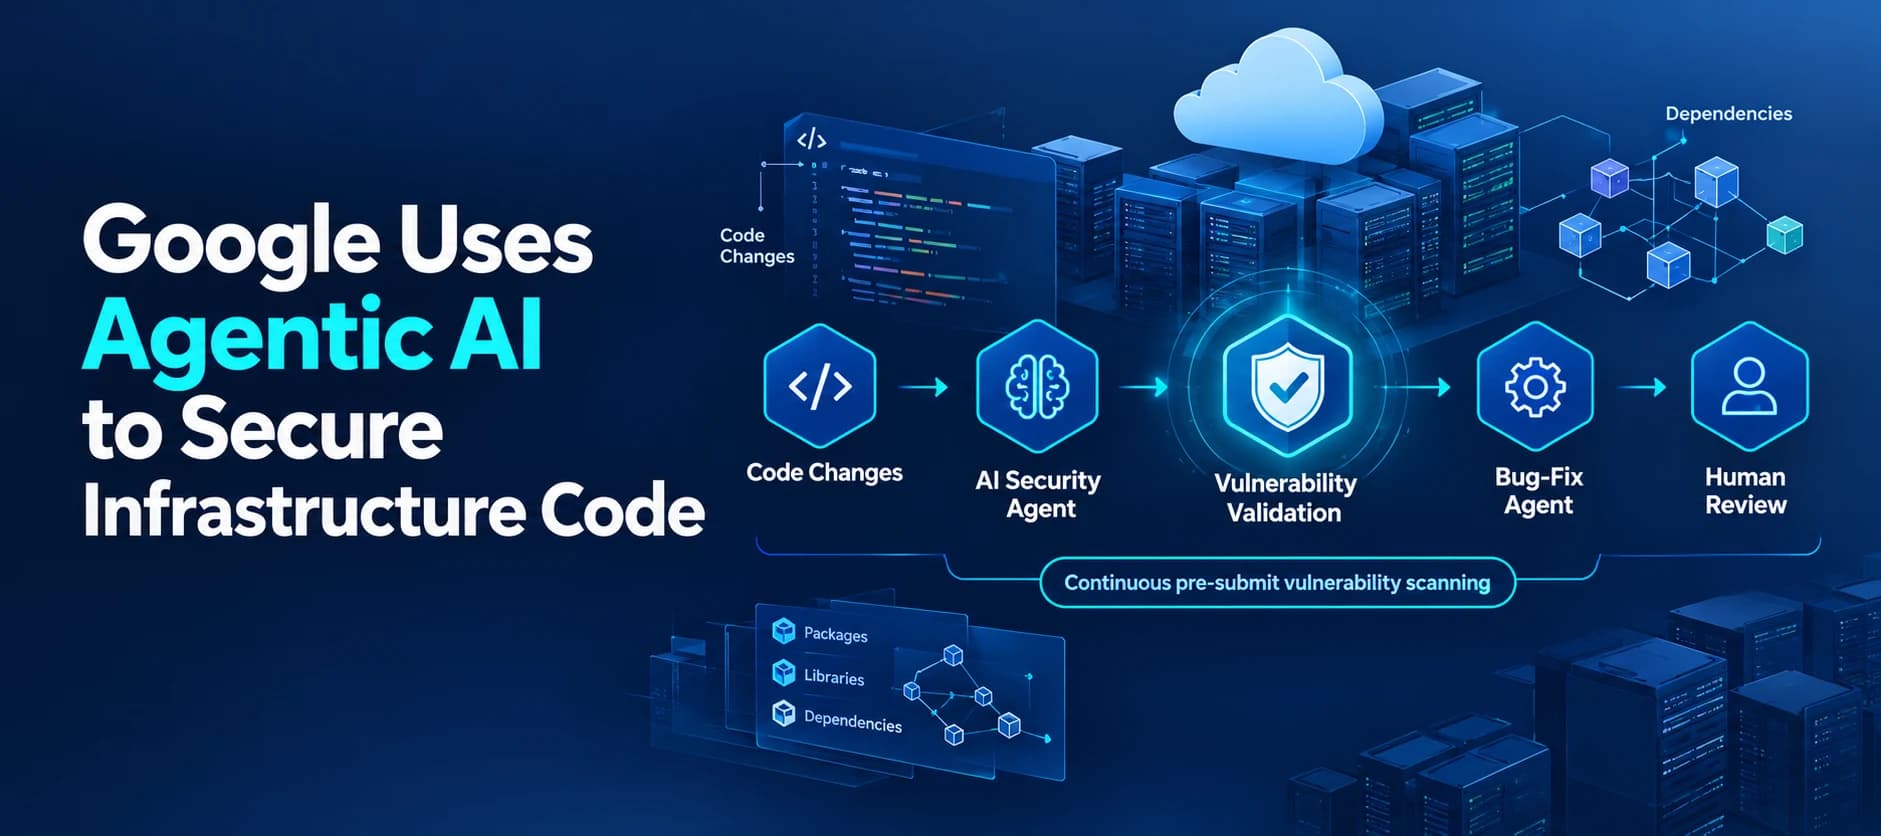
Google Uses Agentic AI to Secure Infrastructure Code
Google says its AI agents continuously scan infrastructure code before submission, validate potential vulnerabilities, and propose fixes for human review. The system scans every code change across hundreds of millions of lines of code.
 Trending
Microsoft Discloses Critical CVSS 10 Azure AI Foundry Privilege Escalation Flaw
Microsoft has disclosed CVE-2026-85889, a critical Azure AI Foundry elevation-of-privilege vulnerability caused by missing authentication for a critical function. Microsoft says the issue is fully mitigated and requires no customer action.
 Trending
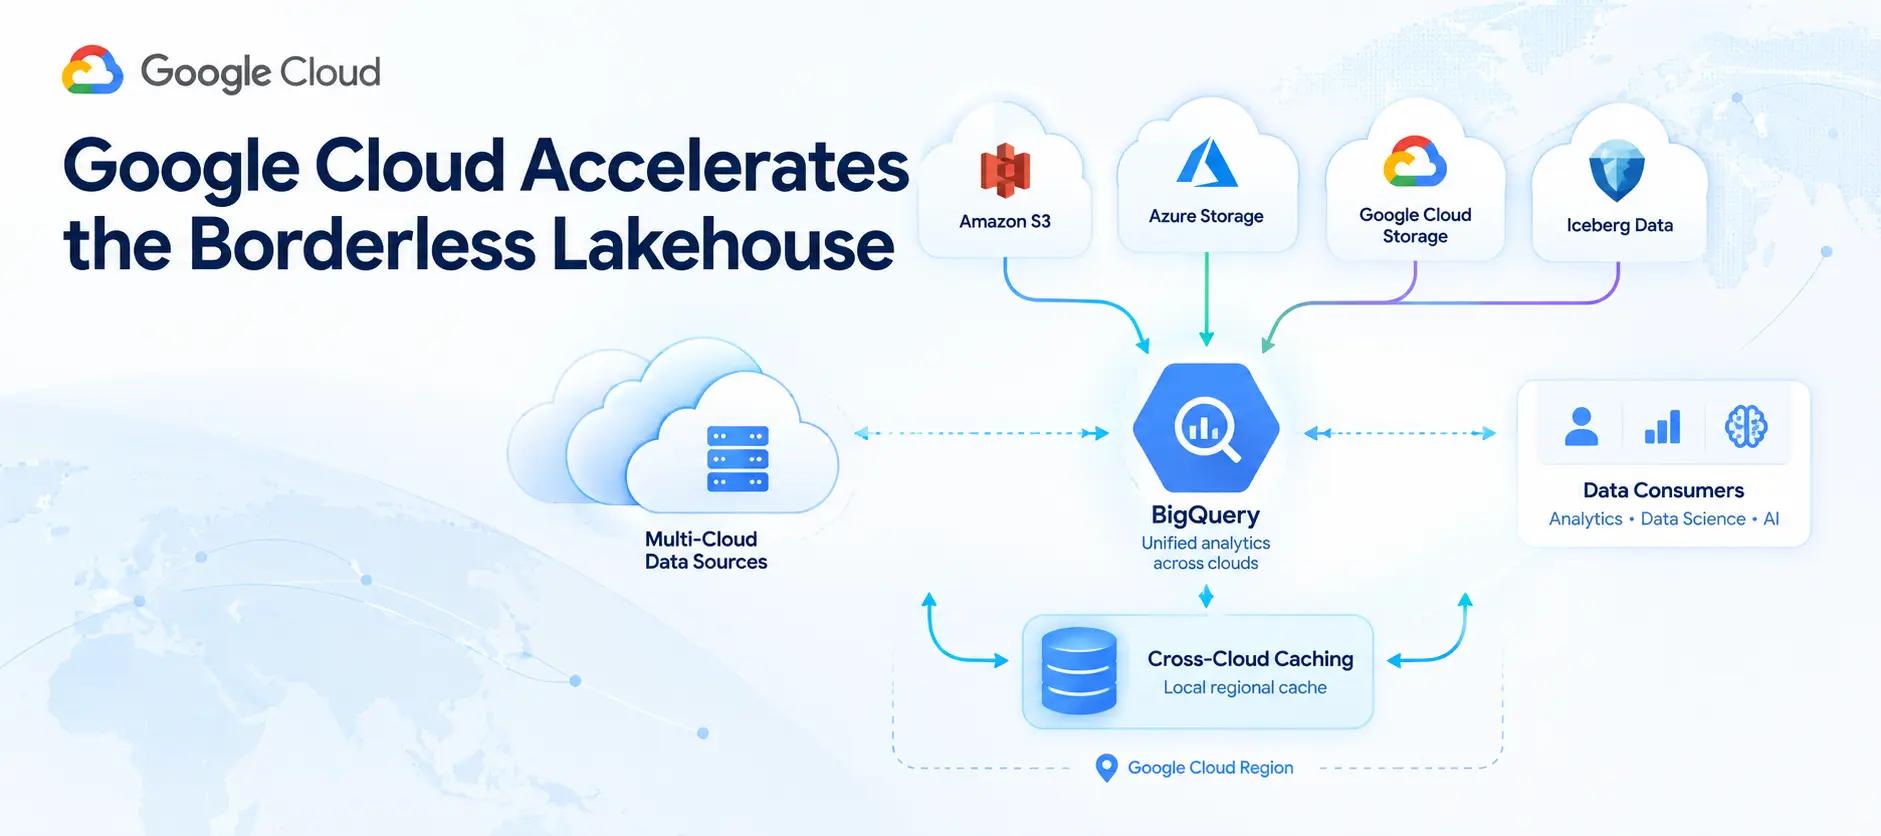
Google Cloud Previews Cross-Cloud Caching to Accelerate the Borderless Lakehouse
Google Cloud is previewing cross-cloud caching for its borderless Lakehouse, helping BigQuery reduce repeated data transfers when querying data stored across clouds.
 Trending
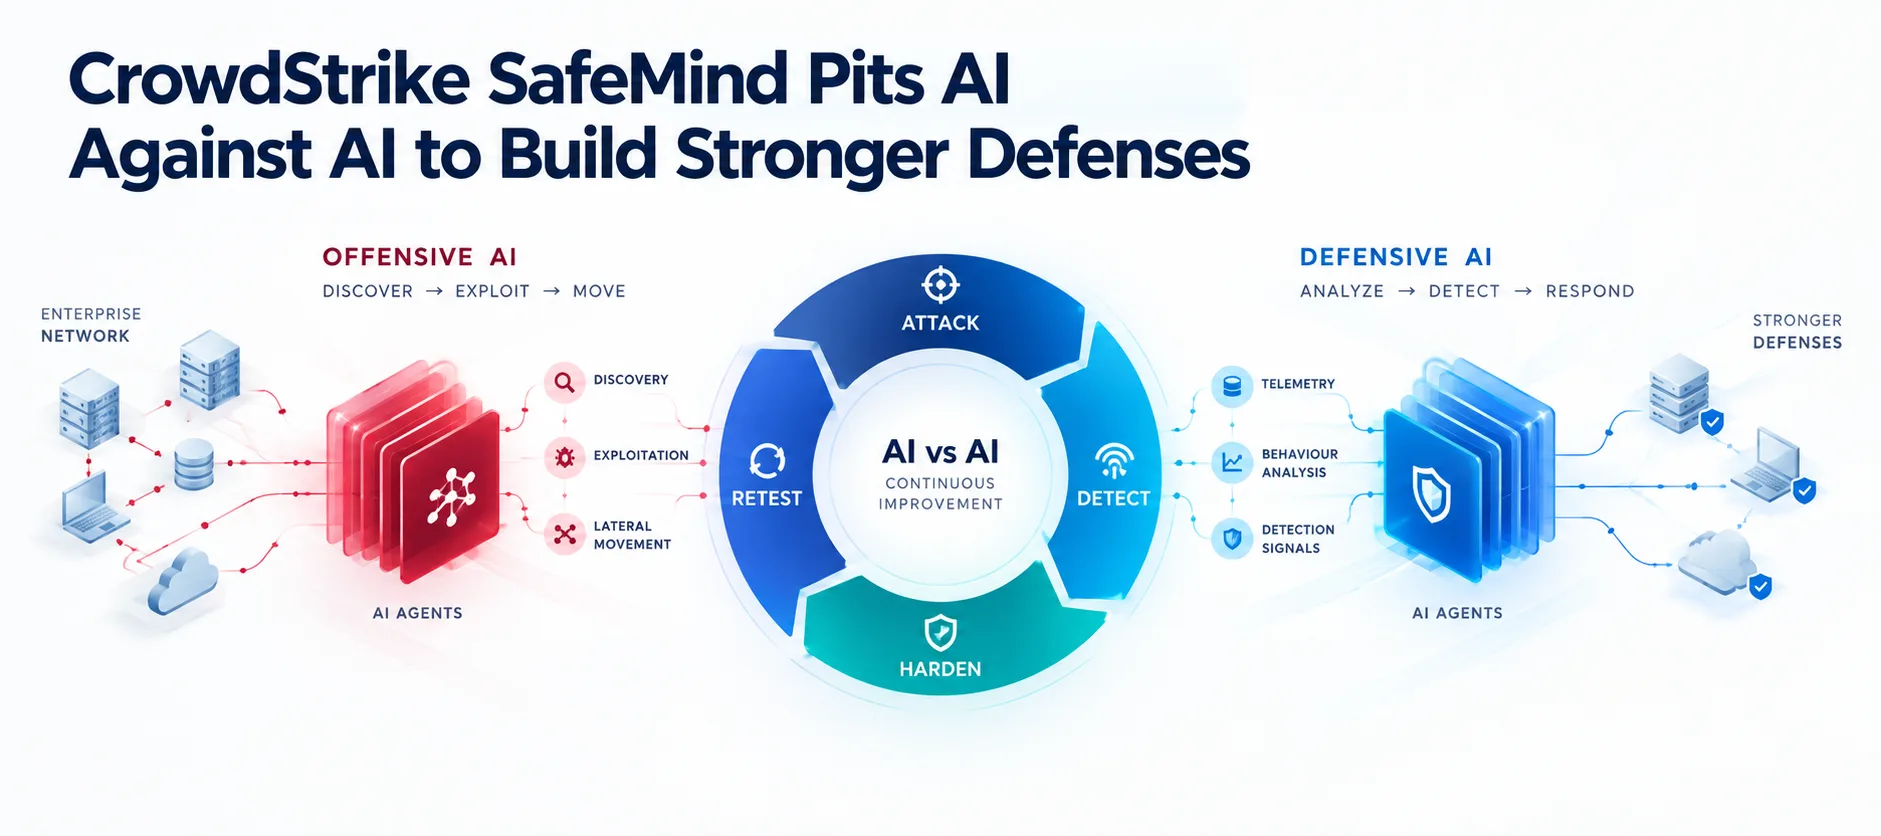
CrowdStrike SafeMind Pits AI Attackers Against AI Defenders in a Continuous Security Loop
CrowdStrike's SafeMind combines an offensive AI agent, a defensive detection agent and realistic cyber environments so attacks and defenses continuously challenge each other.
 Trending
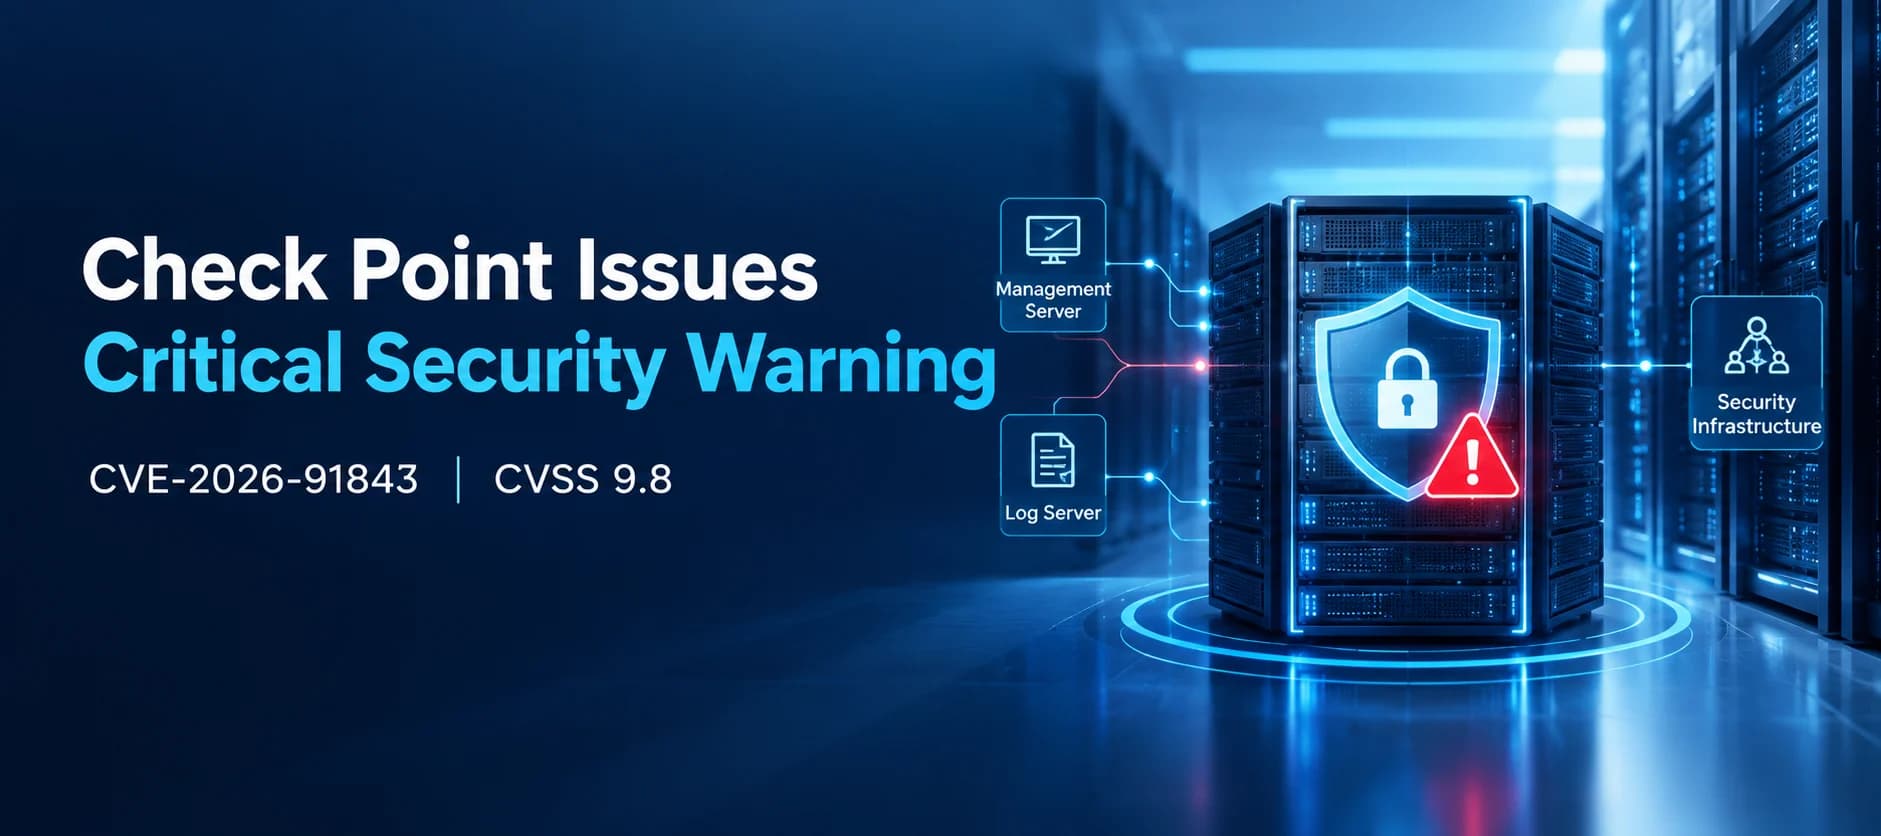
Check Point Warns of Critical CVE-2026-91843 Vulnerability in Security Management Servers
Check Point has issued an urgent security notification for CVE-2026-91843, a critical vulnerability affecting Security Management and Log Servers that could allow unauthenticated remote code execution with root privileges.
 Trending
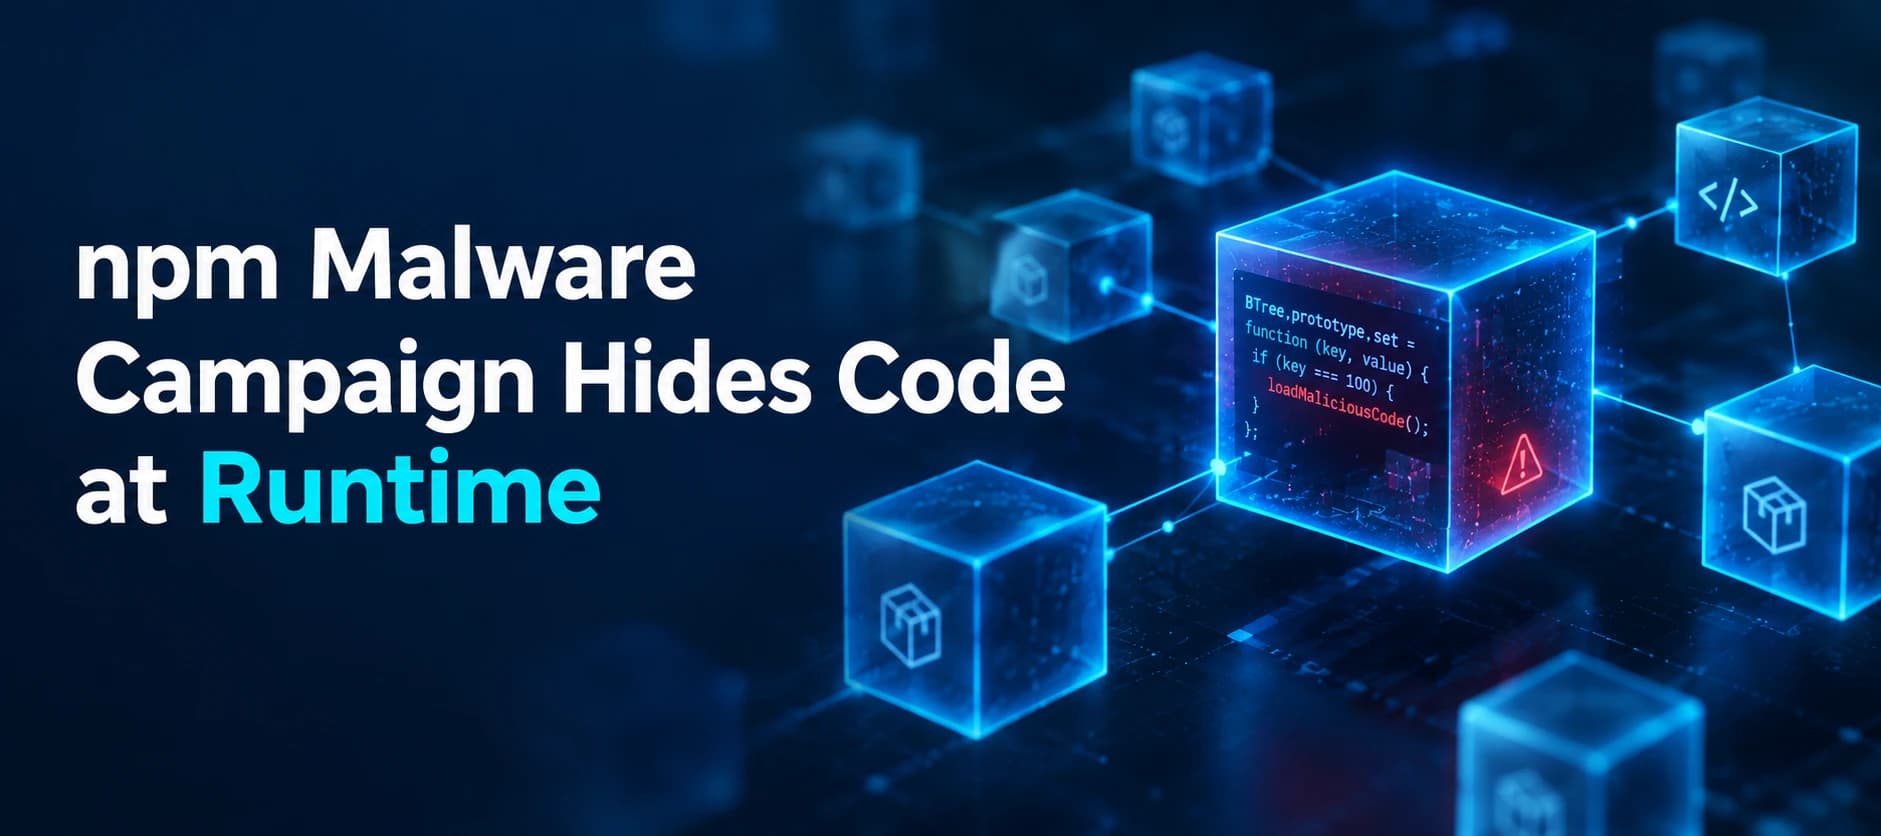
npm Malware Campaign Hides Malicious Code Inside B-Tree Methods, Reaching Nearly 2 Million Weekly Downloads
A malicious npm package, indexed-btree, hides its malware trigger inside a B-tree method rather than an installation script. Checkmarx reports a campaign involving millions of weekly downloads, blockchain-based command and control, and runtime-triggered data theft.