
Cloudflare Builds Evidence-Grounded Agentic Security Operations Harness
Cloudflare has built a multi-agent security operations harness that combines deterministic evidence collection with specialist AI agents to investigate alerts, correlate findings and provide evidence-backed recommendations to Managed Defense Analysts.
Xcademia Team

Cloudflare Takes a Multi-Agent Approach to Security Operations
Security teams rarely receive alerts in isolation.
A single security event can generate a spike of related alerts across an environment, forcing analysts to determine which events are connected, which require investigation and which are simply recurring noise.
Cloudflare describes this as the alert paradox. The more alerts arrive, the more time analysts can spend gathering evidence and connecting detections instead of resolving incidents.
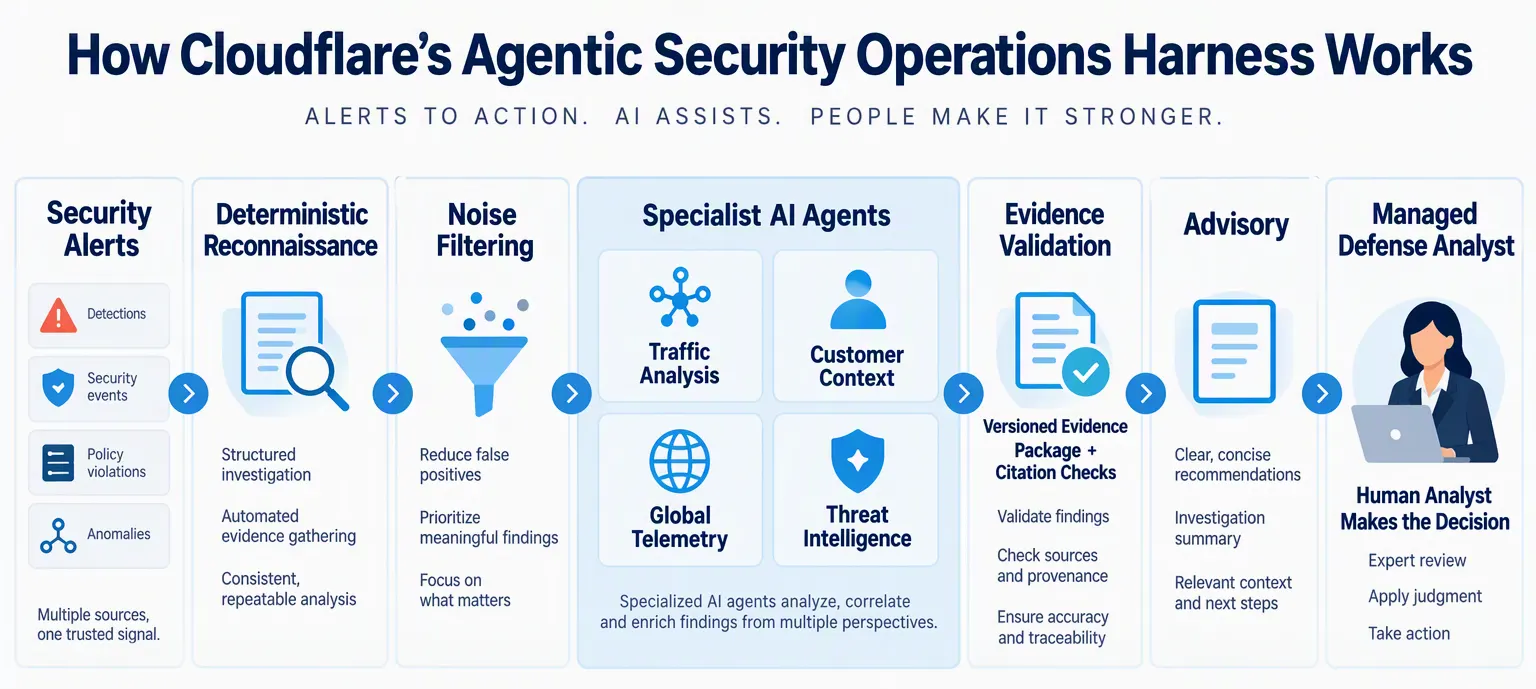
To address this problem, Cloudflare has developed a built-in, multi-AI-agent security operations harness for its Managed Defense service.
The company says the harness helps gather data, connect and aggregate detections, account for missing sources and provide Managed Defense Analysts with a consolidated view of an investigation.
Cloudflare's approach is deliberately different from simply giving one general-purpose AI agent control over the entire investigation.
Instead, the company separates deterministic evidence collection from AI-based interpretation and assigns different investigation tasks to specialist AI agents.
Cloudflare's Security Operations Harness
Cloudflare says its Managed Defense AI agent harness is designed to reduce the time analysts spend assembling information from multiple security sources.
The system collects investigation data, connects related detections and identifies gaps in available evidence while new alerts continue to arrive.
For deeper analysis, Cloudflare uses approved models from the OpenAI Daybreak Defense Network and its partnership with Anthropic.
The company says approved OpenAI Daybreak and Anthropic models, including GPT-5.6 Cyber and Mythos, are used for deeper model-backed analysis.
Initial analysis and scoring are performed using Clef, Cloudflare's open-source decision model.
The objective is not to remove analysts from the process. Instead, Cloudflare says the system gives Managed Defense Analysts a consolidated view of related alerts, available evidence, visible gaps and recommended next steps.
Why Cloudflare Moved Away From a Single AI Agent
Cloudflare says its first prototype used a single general-purpose AI agent to conduct the entire investigation.
The prototype produced useful analysis, but it also generated unsupported claims.
According to Cloudflare, several problems emerged.
Context Could Become Authority
A detection is a hypothesis, not proof that an exploit succeeded or that an attack occurred.
Cloudflare found that a broad AI agent could blur the distinction between evidence and interpretation.
Investigation Scope Could Drift
An AI agent could potentially query the wrong account, time period or data source.
Cloudflare concluded that a language-model prompt alone was not sufficient to enforce investigation boundaries.
Failed Lookups Could Become Ambiguous
If a lookup timed out, the resulting investigation might not clearly distinguish between:
A source that was not checked
A source that was checked but produced no match
A source that provided evidence supporting an absence
These limitations led Cloudflare to move evidence collection and scope enforcement into application code before AI models perform analysis.
Recon First, Inference Second
One of the central principles in Cloudflare's design is "recon first, inference second."
The front portion of the security operations harness does not use AI agents.
Instead, deterministic code runs a fixed set of reconnaissance workflows using versioned API calls.
The system collects information including:
Customer identity
Detection history
Traffic baseline
Enforcement outcome
Network observations
Each piece of information is stored with its source, version and timestamp.
Cloudflare says this allows the investigation to connect the behavior that triggered an alert with the security control that fired and the outcome that followed.
This fixed reconnaissance snapshot also makes evaluation more reproducible.
When AI agents independently retrieve information, two investigations can receive different inputs because the underlying data may have changed between runs.
Cloudflare's approach creates a snapshot that can be replayed. This means differences between specialist AI agents can be evaluated as differences in interpretation rather than differences in data retrieval.
Filtering Security Noise Before Deeper AI Analysis
Not every security alert represents an incident.
Cloudflare says the same rule can repeatedly trigger on a known traffic pattern. Sending every such alert to Managed Defense Analysts can increase workload and make it harder to focus on genuine security incidents.
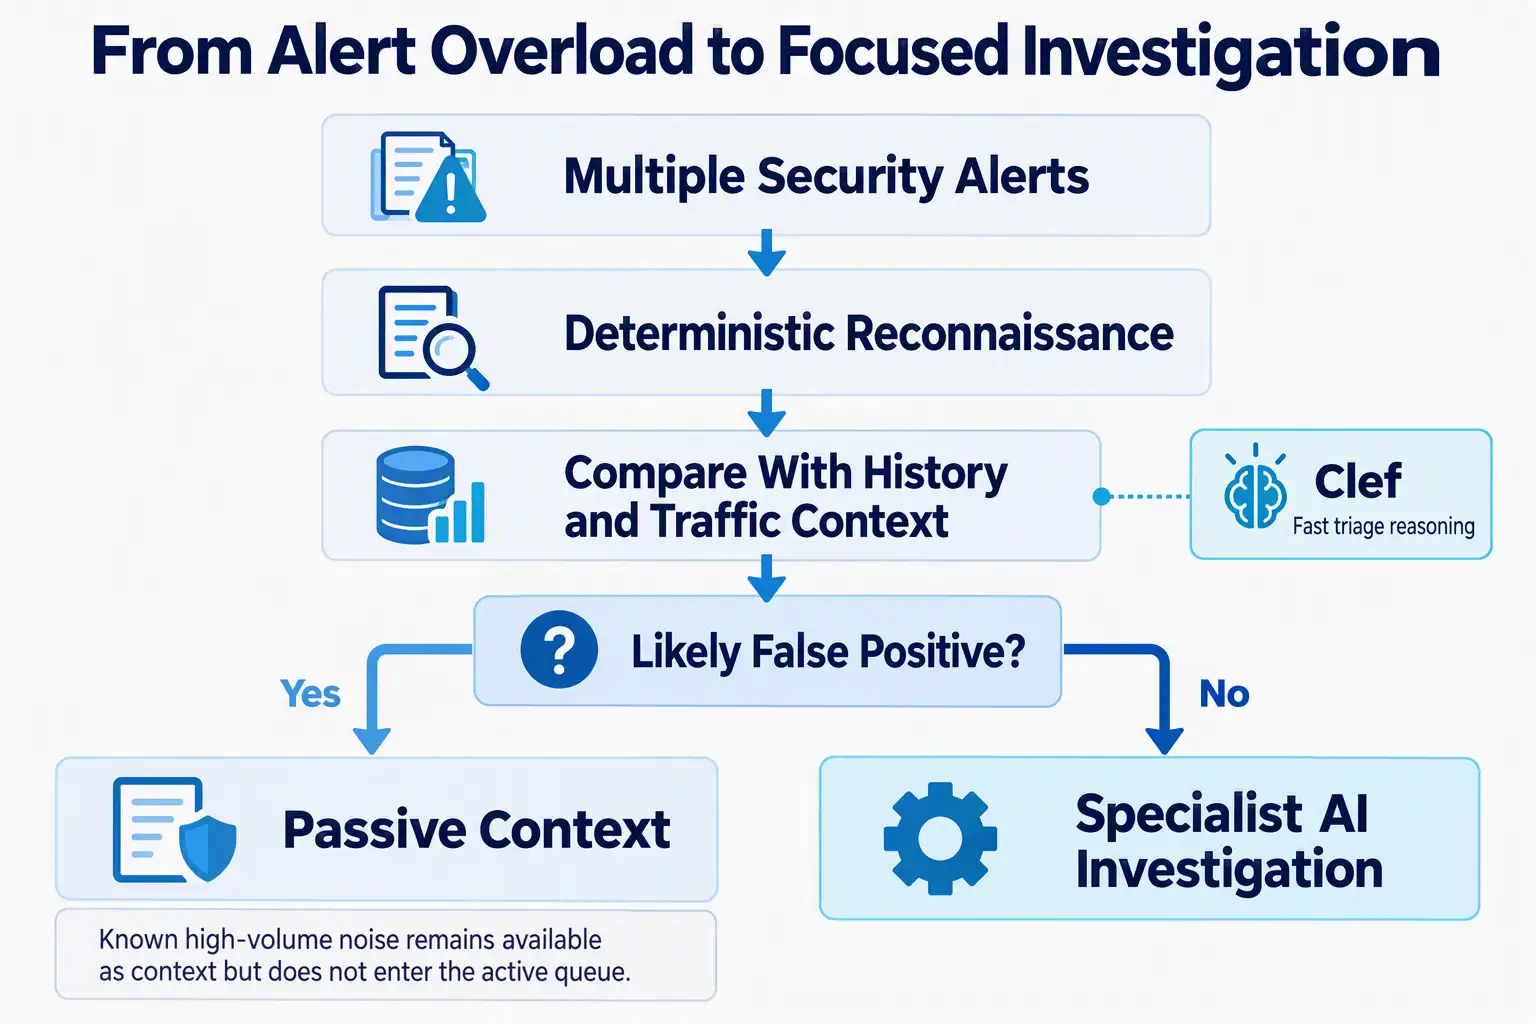
To address this, Cloudflare uses a lightweight triage model to compare an alert with its reconnaissance data.
The system considers questions such as:
Has this event been detected for the customer before?
What decision did Managed Defense Analysts make previously?
Does the traffic resemble normal human behavior?
Alerts with a high likelihood of being false positives can skip analysis by the specialist AI agents.
Cloudflare says Clef, running on Workers AI, is used for this fast agentic reasoning.
Known high-volume noise can also be deterministically classified as passive when it arrives. The information remains available as context but does not enter the active investigation queue.
Specialist AI Agents Handle Different Investigation Tasks
For alerts requiring deeper analysis, Cloudflare says a coordinator AI agent runs four specialist AI agents in parallel.
Each specialist has a narrow responsibility.
Traffic Analysis
The traffic analysis specialist reviews request behavior, historical changes and enforcement.
Customer Context
The customer context specialist examines earlier alerts, previous dispositions and decisions made by Managed Defense Analysts.
Global Telemetry
The global telemetry specialist compares the activity against privacy-preserving signals observed across Cloudflare's broader network.
Threat Intelligence
The threat intelligence specialist checks indicators already admitted to the alert or case.
A synthesis AI agent then combines the specialist findings into a single advisory.
Cloudflare says the synthesis agent cannot fetch new evidence or select a classification outside the approved vocabulary.
The separation is intended to make unsupported claims easier to identify and recommendations easier to audit.
Global Context Without Exposing Customer Data
Cloudflare says security investigations need context beyond the individual environment being monitored.
For example, an IP address might target one website, scan thousands of websites or appear for the first time. These patterns can carry different significance.
Cloudflare's global telemetry specialist uses aggregated information rather than another customer's individual records or identity.
The global view combines features from several Cloudflare services and datasets, including:
CDN
WAF
DDoS
Turnstile
Rate Limiting
Cloudforce One threat intelligence
The synthesis AI agent considers global reputation alongside customer history.
Cloudflare says this allows globally common patterns to provide useful context for an individual customer without automatically treating the activity as a widespread campaign affecting every customer.
History Becomes Part of the Evidence
Cloudflare's system also considers the history of an alert.
The reconnaissance dossier records an alert's previous track record, including how frequently the service alert has fired, how often previous instances were classified as false positives and what Managed Defense Analysts concluded.
This allows the system to distinguish between a pattern that has repeatedly been benign and a new pattern that has not previously been observed.
Approved background context from previous alerts and cases can also be carried into a new investigation.
Cloudflare says its system aggregates related alerts into a consolidated case.
Each case stores evidence, findings and recommendations.
The system deterministically joins and correlates this information, while a Managed Defense Analyst remains responsible for confirming the actual scope.
Over time, a case can connect network, application and Zero Trust evidence while retaining information about the source of that evidence.
From Evidence to a Decision
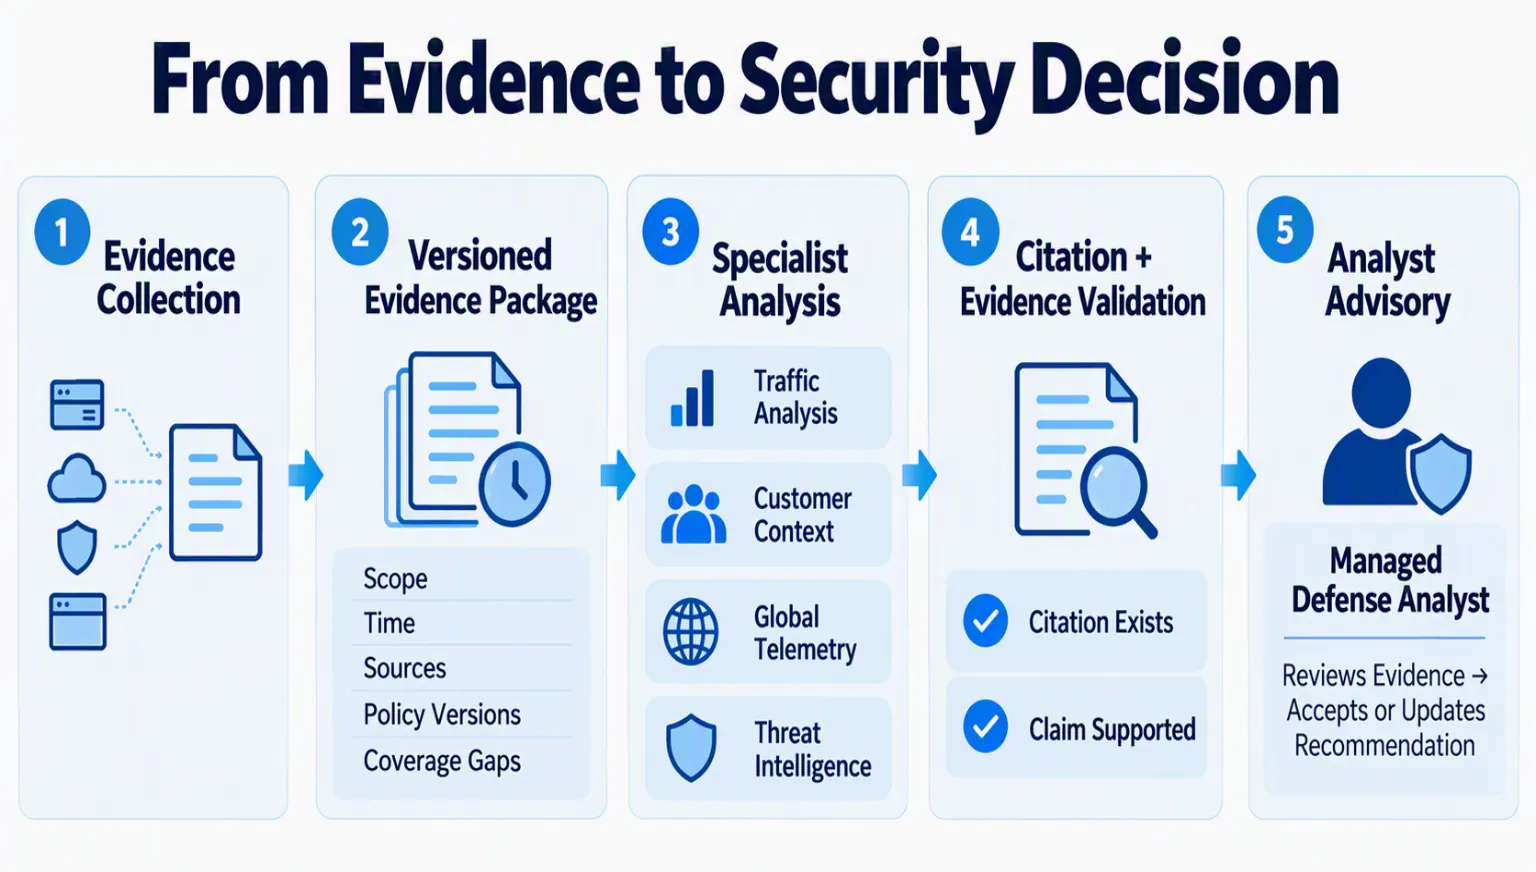
Cloudflare says every investigation begins analysis with a versioned evidence package.
The package contains:
Subject
Scope
Time anchor
Admitted evidence
Policy versions
Sources
Coverage gaps
Specialist AI agents must cite items from this evidence package.
Application code then checks whether each citation exists, belongs to the investigation and supports the claim attached to it.
Invalid findings can be corrected or recorded as limitations.
Cloudflare also uses Clef a second time to evaluate the evidence itself.
The system asks whether the collected evidence is sufficient for a decision and whether any evidence contradicts another finding.
Based on the available evidence, Clef selects from a deterministically reduced list of attack classifications and dispositions.
Cloudflare's Developer Platform Runs the Workflow
Cloudflare says its developer platform provides the infrastructure for the security operations process.
Application code running on Workers admits evidence and validates results.
Workflows coordinates the stages and saves completed work before the next stage begins.
This means that if a stage fails, the system can reuse evidence and findings that have already passed validation instead of starting the investigation from the beginning.
Cloudflare says D1 stores investigation and advisory state, while R2 stores bounded context and evidence artifacts.
Case-chat state persists in Durable Objects, uses Flue, and is enriched with AI Search.
The architecture therefore combines deterministic application logic, persistent state and AI-based analysis rather than putting the complete workflow under the control of a single language model.
Handling Incomplete Evidence
Security investigations at network scale will sometimes encounter incomplete information.
Cloudflare says a source may fail, a comparison may time out, metadata may be missing or a threat intelligence lookup may return no match.
Instead of treating these situations as equivalent, the system records the state of the evidence.
Cloudflare identifies three possible states:
Not checked
The source or comparison has not been evaluated.
Checked, with no matching result
The source was checked but did not return a relevant match.
Checked, with evidence supporting absence
The investigation contains evidence supporting the conclusion that something was absent.
This distinction is important because an unavailable source should not automatically be interpreted as evidence that nothing was found.
For example, if global telemetry is unavailable, the system can still describe what is unusual about activity for a specific customer.
However, Cloudflare says it cannot determine from that incomplete evidence whether the pattern is widespread.
When evidence is insufficient, the system makes no classification or disposition recommendation.
Recommendations Can Lead to Remediation
Cloudflare's goal extends beyond producing another investigation ticket.
The advisory can recommend specific mitigation actions, such as:
A rate-limiting rule for an abusive path
A WAF custom rule for a particular signature
A DDoS protection change
For fully managed customers, Managed Defense Analysts can apply suggested rules.
Other customers receive recommendations through the dashboard and their chosen alert path.
Cloudflare emphasizes that the Managed Defense Analyst remains responsible for the final decision and mitigation.
Each alert and case includes the evidence supporting the AI agent's recommendation.
This allows analysts to inspect the evidence, conduct additional investigation and either accept or modify the recommendation.
Human Analysts Remain in Control
A central part of Cloudflare's design is that AI agents do not receive authority to independently make security decisions across customer environments.
Cloudflare says application code fixes the customer scope before model results are processed.
Each specialist AI agent receives only the evidence required for its assigned task.
The model does not receive authority to cross tenant boundaries or act on behalf of Managed Defense Analysts.
This architecture reflects Cloudflare's broader emphasis on keeping evidence collection, scope enforcement and validation in application code while using AI for interpretation and recommendation.
What Comes Next for Cloudflare Managed Defense
Cloudflare says Managed Defense Analysts will continue to be responsible for judgment while the AI agent harness handles more repetitive investigation work.
The company says it plans to add a Custom Managed level over the next few quarters, providing more flexibility for individual organizations.
Cloudflare also plans to explore continuous AI agents that monitor Cloudflare traffic and identify patterns that fixed rules and thresholds might miss.
The source does not provide additional details about the planned Custom Managed level or the future continuous AI agents.
The current early beta is available in Cloudflare Managed Defense for eligible application-security alerts and cases.
Cloudflare says organizations already using supported products such as WAF, DDoS protection or Magic Transit can contact their enterprise account team about adding Managed Defense.
The Bigger Picture: Building Guardrails Around AI Security Operations
Cloudflare's approach highlights a broader shift in how organizations are experimenting with AI for security operations.
The central design choice is not simply to add more AI agents. It is to define what the agents are allowed to see, what evidence they can use, what conclusions they can make and how those conclusions are validated.
Cloudflare's experience with its first single-agent prototype also illustrates why evidence grounding matters in security investigations. A model can produce plausible analysis while still confusing a detection with proof, drifting outside the intended scope or failing to distinguish missing evidence from negative evidence.
The company's current architecture addresses those problems by putting deterministic reconnaissance, scope enforcement, evidence validation and workflow state outside the language model.
Specialist AI agents then operate within those boundaries.
For security teams, the development reflects growing interest in AI-assisted operations that preserve human judgment while reducing repetitive investigation work.
The key question is therefore not simply whether AI can investigate an alert.
It is whether the investigation can remain evidence-grounded, scoped, auditable and useful to the analyst making the final decision.
Source: Cloudflare Blog
About the Author