
Ahold Delhaize Begins Controlled System Relaunch After Cybersecurity Incident
Ahold Delhaize is beginning a controlled relaunch of certain systems following a cybersecurity incident. Its investigation continues, and the company says it currently has no evidence that customer or associate data was taken.
Xcademia Team
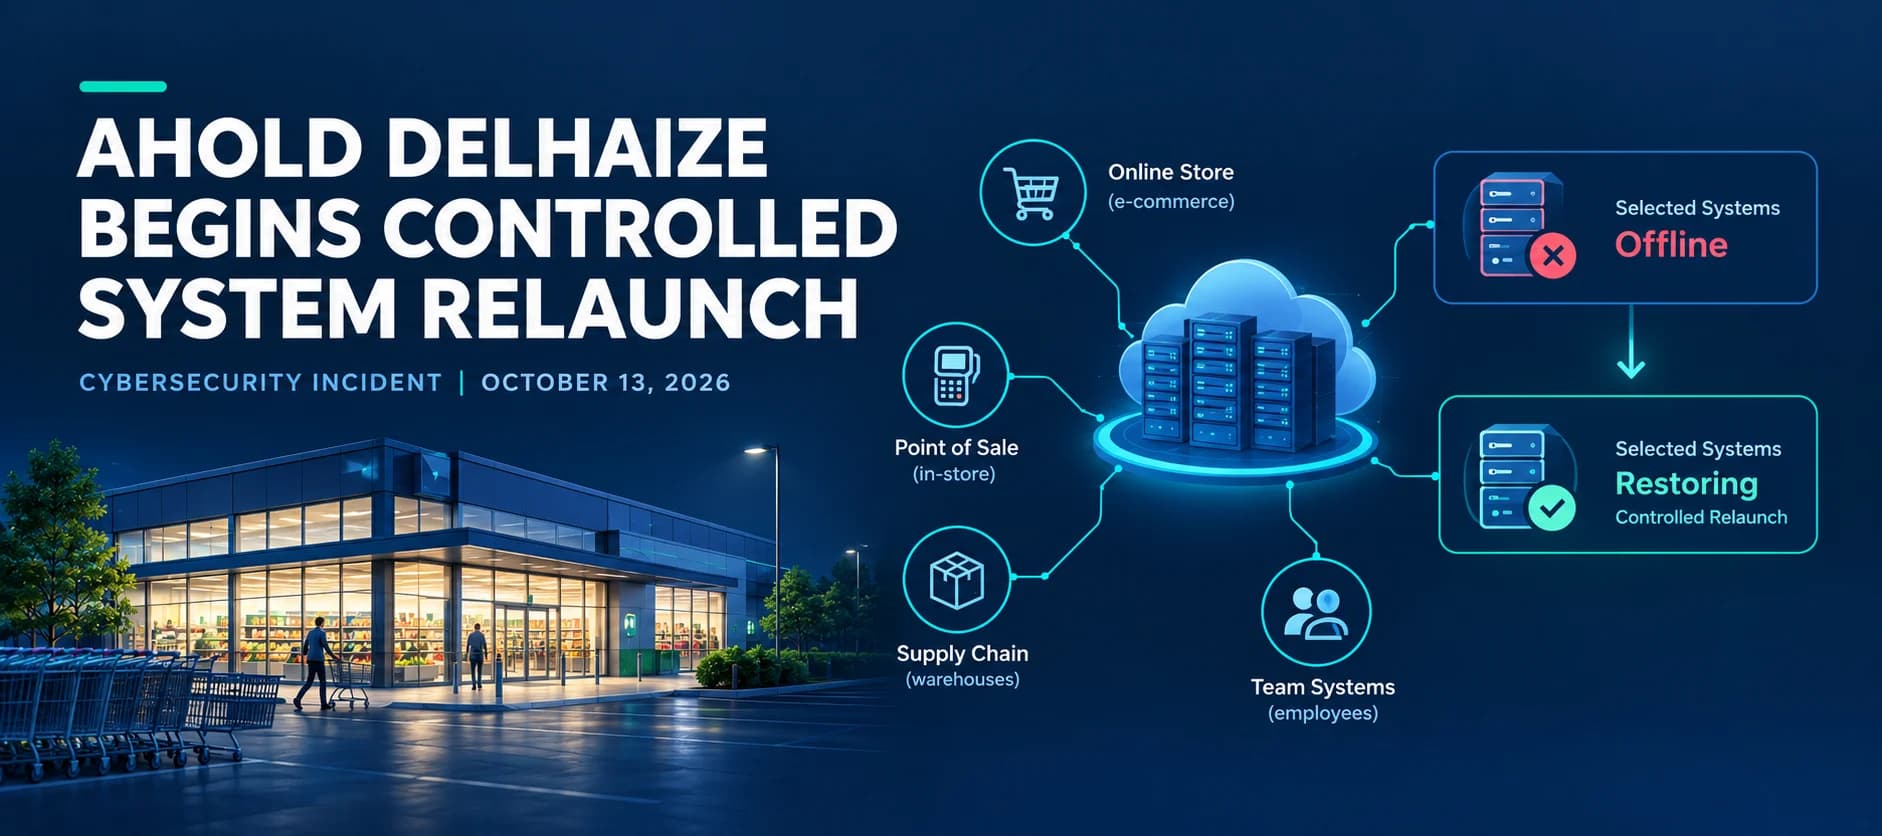
Ahold Delhaize has begun a controlled relaunch of certain systems following a cybersecurity incident affecting its network, as the international grocery retail group continues to investigate the issue and restore affected services safely.
In an update published on October 13, 2026, the company said its response had included precautionary measures, such as taking some systems offline to help protect its infrastructure. It acknowledged that these measures had disrupted customers, associates and business partners.
The company also stated that, although its investigation remains ongoing, it currently has no evidence that customer or associate data was taken in the incident.
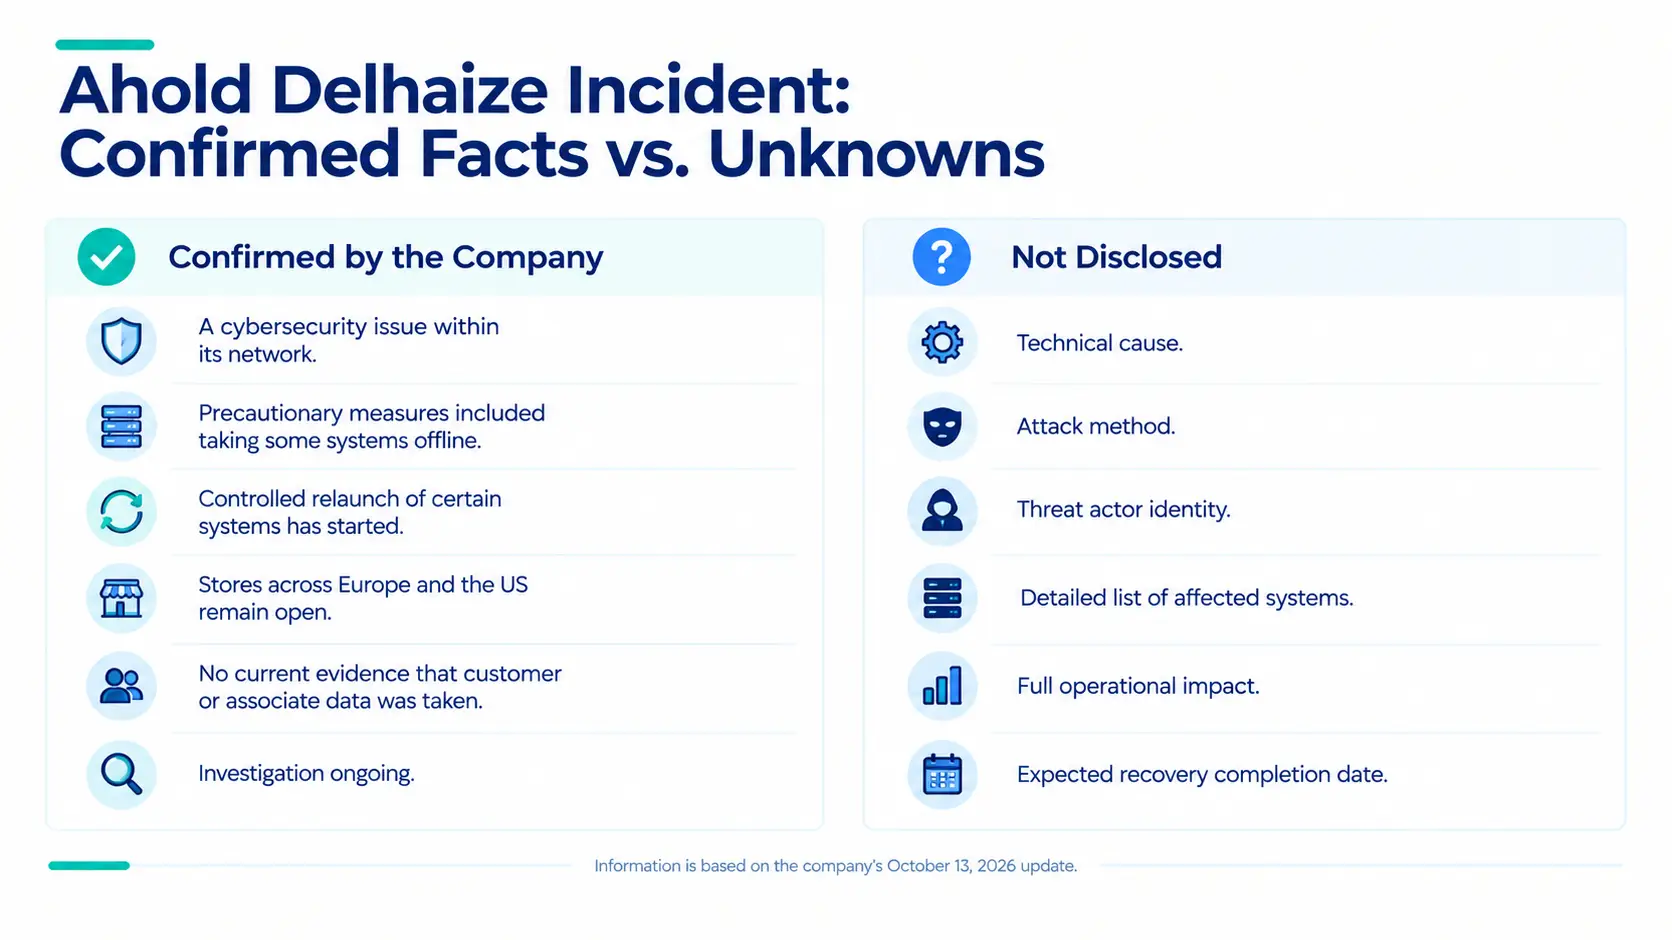
Ahold Delhaize has not disclosed the technical cause of the incident, the systems affected in detail or whether a cybercriminal group was involved.
Ahold Delhaize Begins Controlled System Recovery
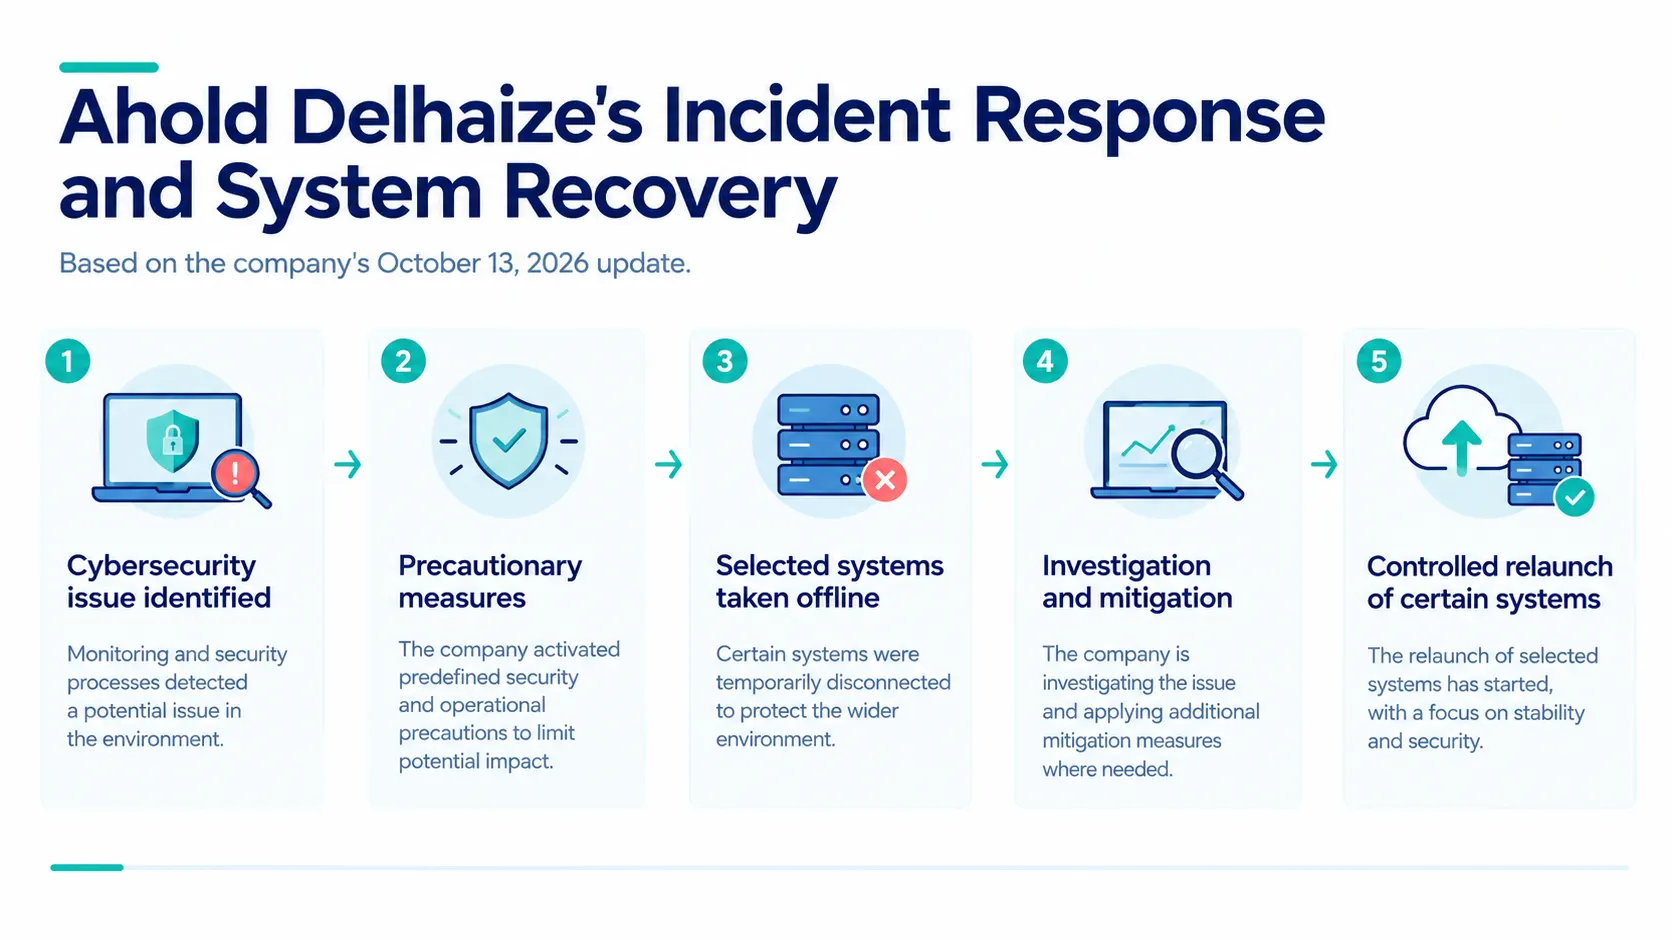
The company first disclosed the cybersecurity issue on October 12, 2026. According to its subsequent update, its teams have been assessing the incident and implementing measures to mitigate the issue.
Taking certain systems offline was part of the company's precautionary response. Ahold Delhaize said it is now starting a controlled relaunch of selected systems as its teams make progress in assessing and mitigating the problem.
The announcement did not identify the specific systems being brought back online or provide a timeline for completing the recovery process.
A controlled relaunch allows an organization to approach service restoration carefully while response teams continue assessing the incident. In this case, Ahold Delhaize has not disclosed the technical procedures or validation criteria guiding its restoration efforts.
Customer and Associate Data: What Is Known?
One of the most significant statements in Ahold Delhaize's update concerns the potential exposure of personal information.
The company said it currently has no evidence that customer and associate data was taken in the cybersecurity incident. However, it also confirmed that its investigation is ongoing.
This statement should not be interpreted as confirmation that no data was accessed or that the investigation has ruled out every form of data exposure. The company has reported the absence of evidence that data was taken at this stage, rather than declaring the incident fully resolved.
Ahold Delhaize has not disclosed whether the incident involved unauthorized access, malware, ransomware, data exfiltration or another attack method. It has also not provided details about the investigation's technical findings.
The current position: The company says it has no evidence at this moment that customer or associate data was taken, while its investigation continues.
Retail Operations Continue Across Europe and the United States
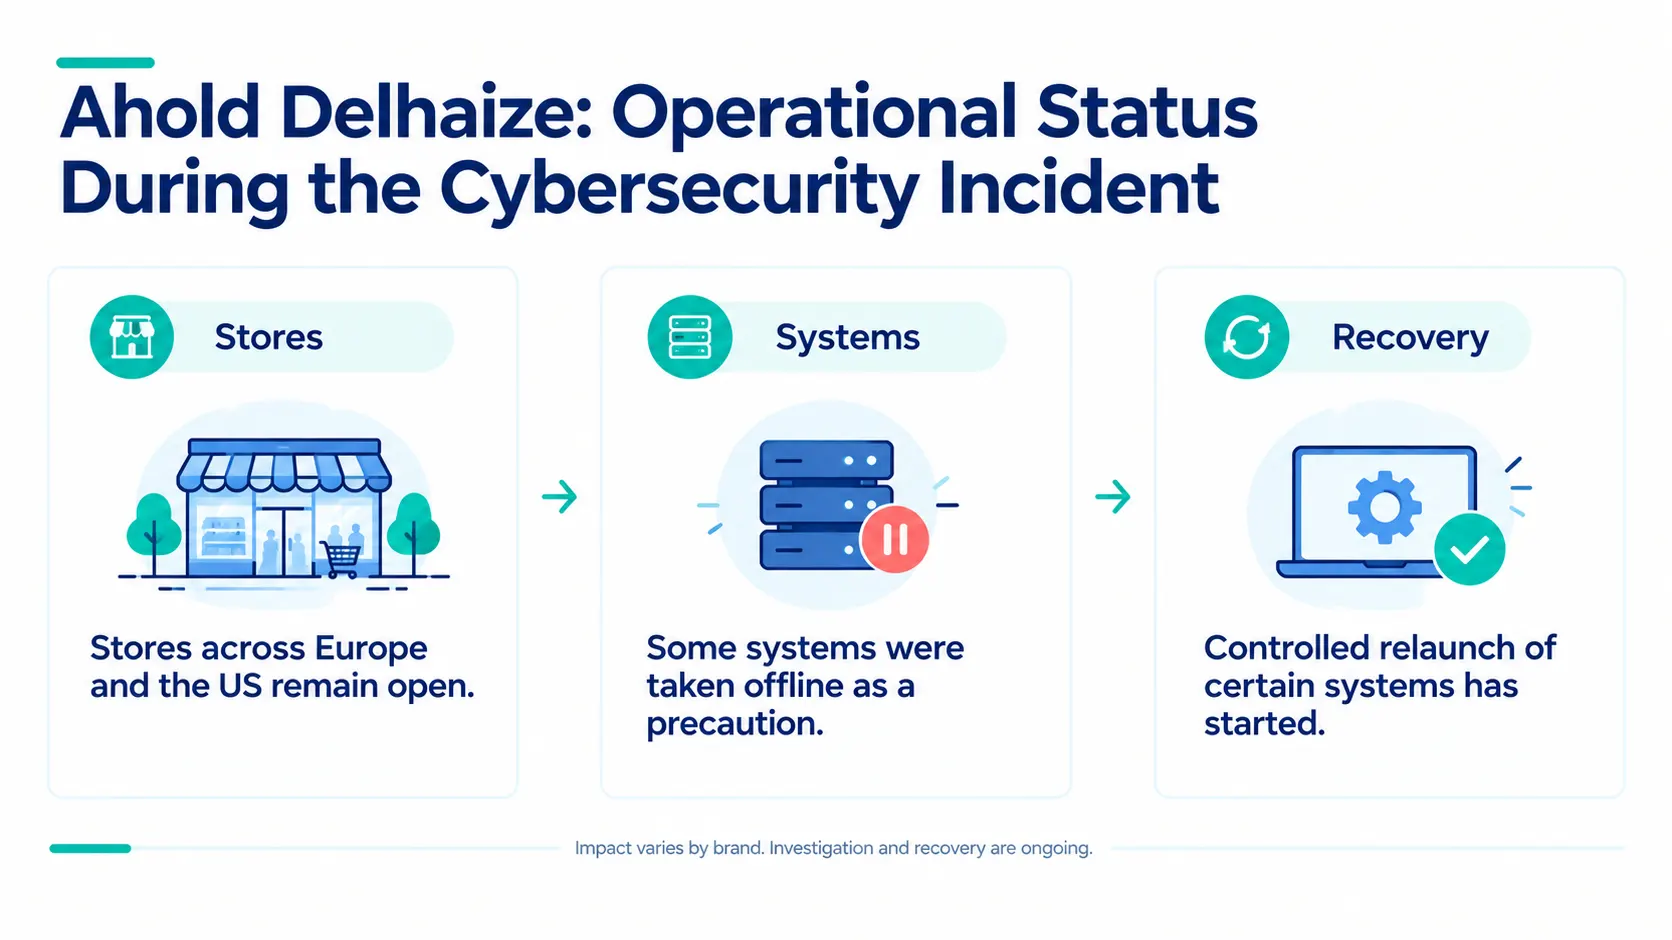
Despite the cybersecurity issue and the precautionary measures, Ahold Delhaize said its brands' stores across Europe and the United States remain open and are serving customers.
The company acknowledged that the impact of its response measures varies by brand. Each local brand is working to serve customers while minimizing disruption.
The update did not identify every affected brand, specify which services have been disrupted or quantify the operational impact. It also did not provide a detailed account of how the incident has affected individual stores or their supporting systems.
The continued operation of stores is an important part of the company's public update, but it does not mean that every supporting system or business service has returned to normal.
External Cybersecurity Experts and Authorities Involved
Ahold Delhaize said it is working with relevant internal teams and external cybersecurity experts as part of its response.
The company is also engaging with appropriate authorities and other stakeholders as necessary. It did not name the external cybersecurity providers or authorities involved, disclose the investigative methods being used or provide details about any suspected attackers.
The company explained that it is withholding further information because the investigation remains ongoing and additional disclosures could compromise security measures or interfere with response efforts.
This limits the amount of technical information currently available about the incident. Its origin, entry point, scope and potential long-term consequences have not been established in the company's published update.
Why the Incident Matters for Retail Cybersecurity
Ahold Delhaize's update highlights the operational decisions retailers may face when responding to a cybersecurity incident: protecting systems, investigating the cause and restoring services while limiting disruption to customers and business partners.
Taking systems offline can be a precautionary measure during an investigation. However, the company's announcement does not explain which technical risks prompted the decision in this case.
The controlled relaunch is another important development, indicating that the company has started bringing certain systems back into operation. The announcement does not establish when all affected systems will be restored or whether further disruptions are expected.
For retail organizations, the incident illustrates the importance of coordinated incident response, communication with stakeholders and carefully managed recovery. These are broader industry considerations, rather than details of Ahold Delhaize's undisclosed technical response.
The company's statement about customer and associate data also underlines the need for precise communication during an investigation. An absence of current evidence that data was taken is not equivalent to a final determination that no data was compromised.
What Happens Next?
Ahold Delhaize said it will provide further updates when appropriate. Its immediate stated priorities are to continue investigating the incident, mitigate the issue and restore affected systems safely.
The company has not announced a definitive recovery timeline, confirmed a threat actor or disclosed the technical cause of the cybersecurity issue.
Until further details become available, the extent of the incident and its ultimate impact remain uncertain.
Conclusion
Ahold Delhaize is moving from precautionary system isolation toward a controlled recovery following the cybersecurity incident disclosed on October 12, 2026.
The company has confirmed that selected systems are entering a controlled relaunch, its brands' stores across Europe and the United States remain open, and its investigation is continuing. It has also stated that it currently has no evidence that customer or associate data was taken.
The next important developments will be further findings from the investigation and updates on system restoration. For now, the company has not disclosed enough technical information to determine the incident's cause, the full scope of its impact or whether any threat actor was responsible.
Source: Ahold Delhaize Newsroom
About the Author