
Sharper every day.
Tutorials, analysis, and career playbooks across 12 disciplines, from cloud and cybersecurity to leadership, finance, and emerging tech. Written by people doing the work. Published daily.
- Articles published
- 94
- Disciplines covered
- 6
- Working contributors
- 2
Latest articles
Page 5 of 8 Career Guidance
Cybersecurity Careers in Dubai and the UAE 2026
Dubai and the UAE offer one of the fastest-growing cybersecurity job markets globally, with strong demand across banking, government, telecoms, and cloud security. This guide covers salaries, certifications, hiring sectors, visa realities, and the skills UAE employers want in 2026.
 Cloud Computing
CCSP vs XCLOUDP
CCSP is the most recognised cloud security certification globally. XCLOUDP focuses on applied multi-cloud security across AWS, Azure, and GCP with live labs and a practitioner-assessed capstone. This article compares both credentials for cloud security professionals in 2026.
 Cybersecurity
How to Use AI Tools to Run an ISO 27001 Gap Assessment
AI tools can reduce ISO 27001 gap assessment drafting from weeks to hours. This article explains a six-stage workflow for control mapping, gap analysis, remediation planning, and executive reporting while keeping analyst validation and judgement central.
 Cybersecurity
CRISC vs XCRISC
CRISC is a globally recognised IS risk credential focused on knowledge of risk and controls. XCRISC is a practitioner-assessed alternative testing real-world FAIR risk analysis, control design, and board reporting. This article compares both for 2026 GRC professionals.
 Career Guidance
What a GRC Analyst Actually Does
GRC analysts connect security controls, risk, audits, and board reporting into a coherent security programme. This article breaks down the real day-to-day work of a GRC analyst in 2026 across governance, risk management, compliance, vendor reviews, and audit preparation.
 Cybersecurity
CISM vs XCISM
CISM is the most recognised IS management credential globally. XCISM tests whether you can actually build a security programme, manage risk, lead teams, and present to a board under real assessment conditions. The honest IS management certification comparison for 2026.
 Cybersecurity
How to Build a Security Awareness Programme
Most security awareness programmes achieve high completion rates but no measurable behaviour change. This guide explains how to build a role-based, simulation-led programme measured against real risk reduction, not training activity.
 Cloud Computing
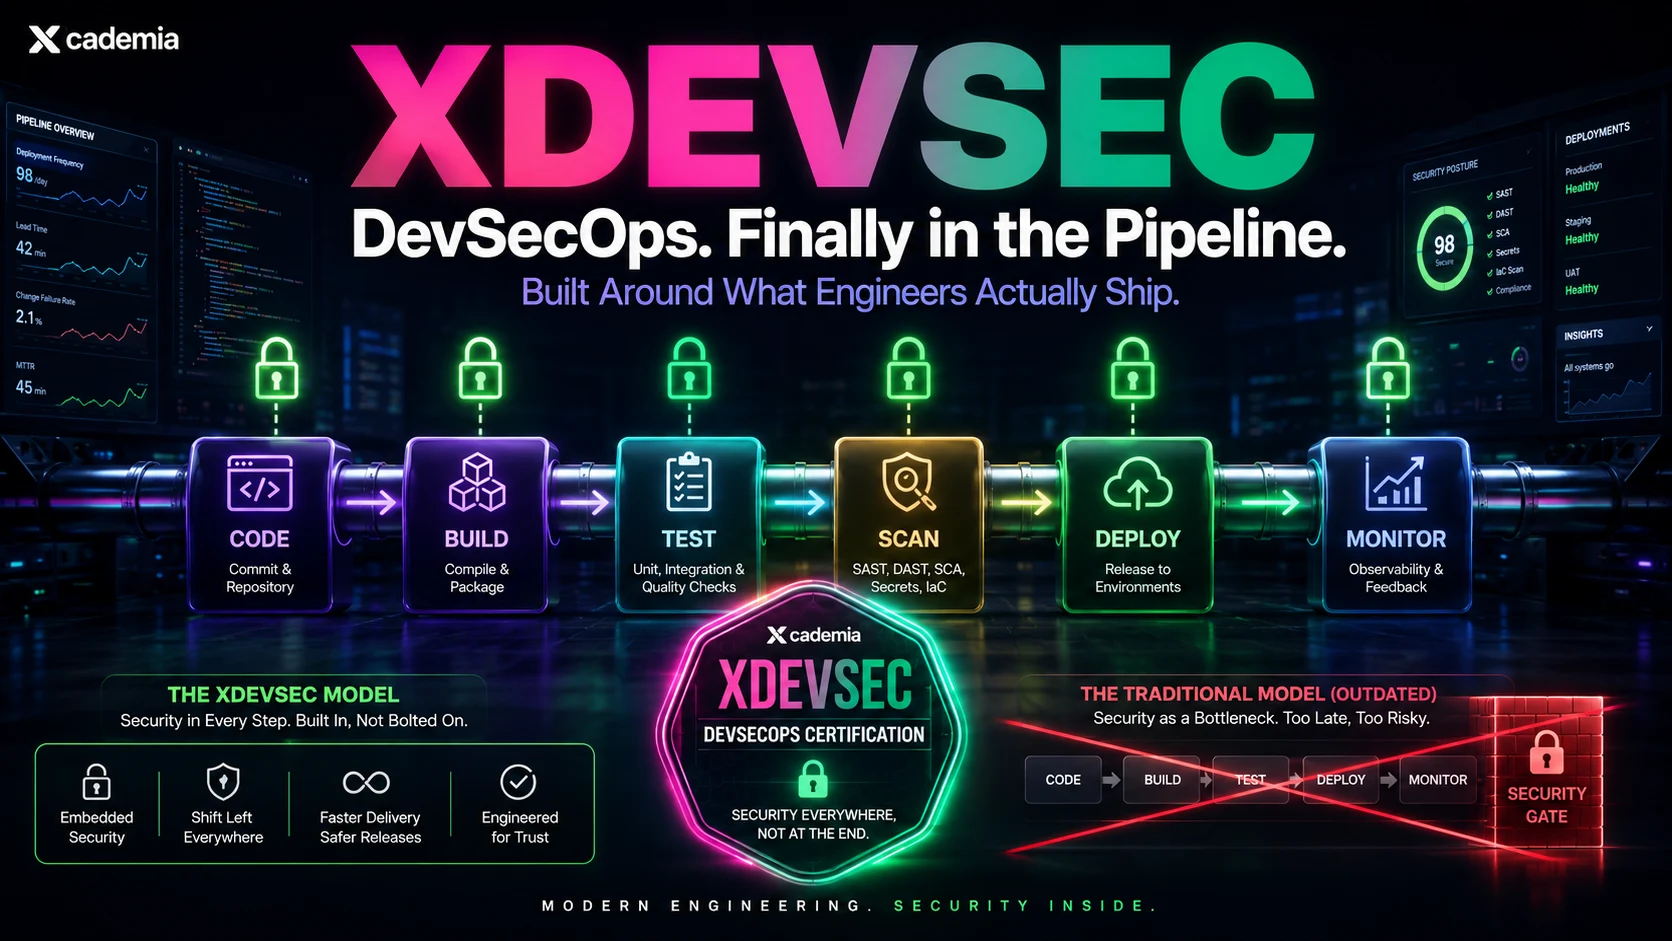
XDEVSEC
Most DevSecOps certifications test concepts, not implementation. XDEVSEC is built for engineers who ship: real CI/CD pipelines, live security gates, SAST, DAST, IaC, and supply chain security in a hands-on capstone.
 Industry Trends
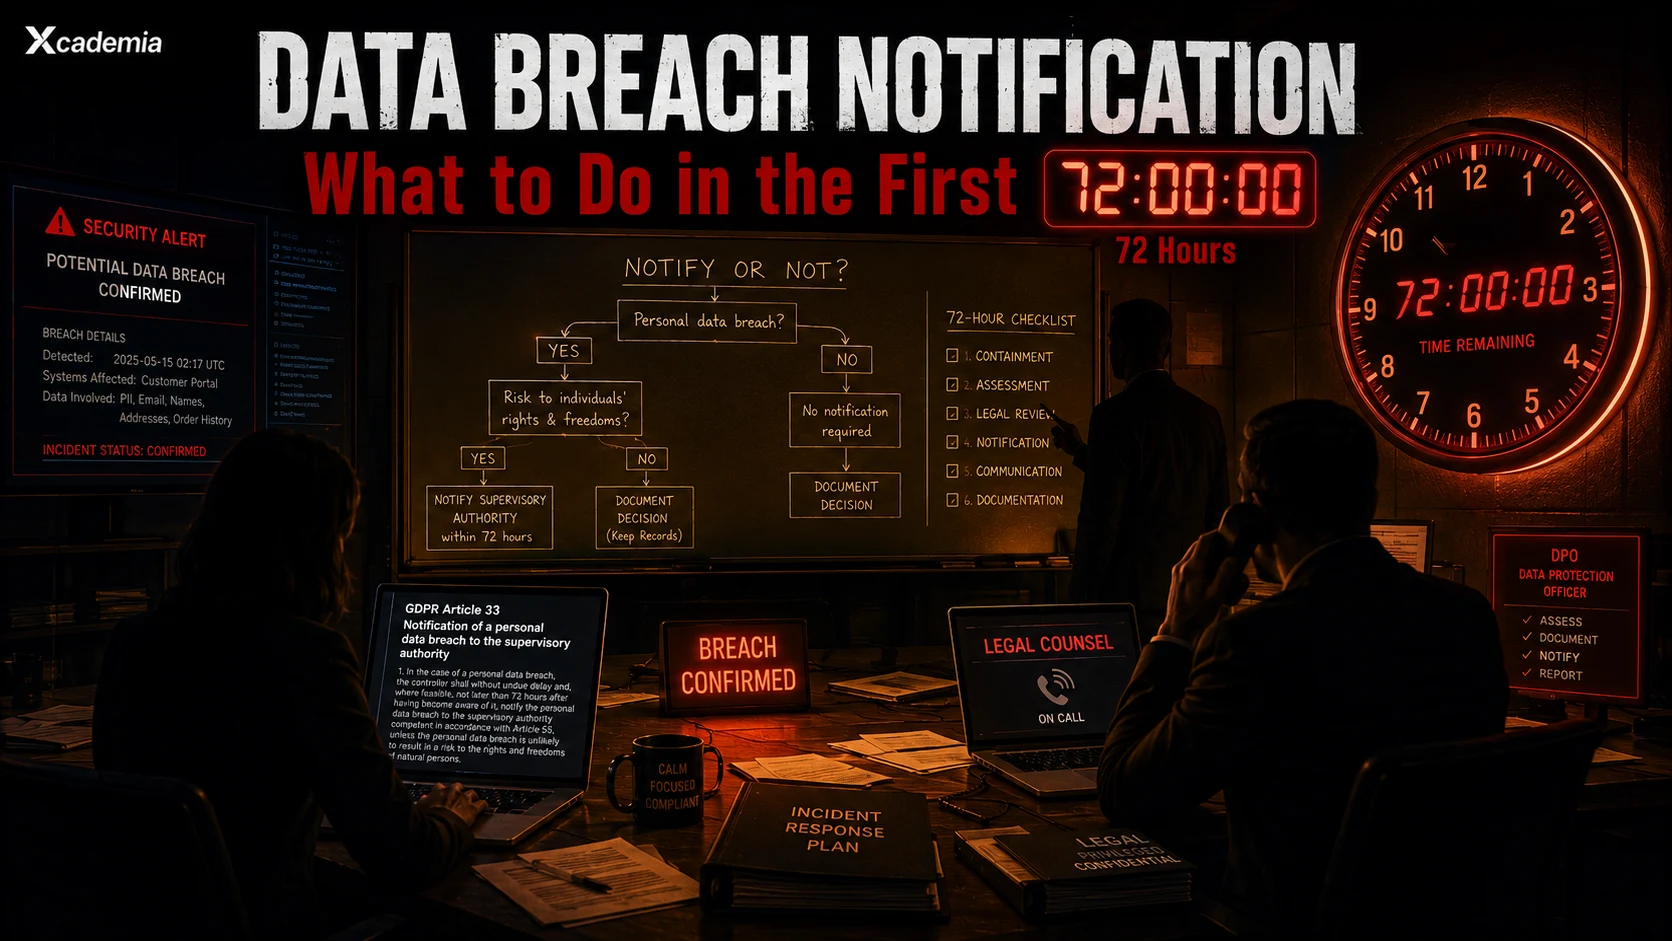
Data Breach Notification
When the forensic team confirms exfiltration, the 72-hour GDPR notification clock begins. This guide breaks down exactly what DPOs, CISOs, and legal teams must do across the first 72 hours, from assessment and ICO notification to individual disclosure and breach documentation.
 Cybersecurity
CASP+ vs XCASP
CASP+ proves advanced security knowledge through performance-based testing. XCASP proves you can design, defend, and communicate security architecture under real assessment conditions. An honest comparison for senior security professionals in 2026.
 Cybersecurity
How to Use AI Tools in a Penetration Test
AI tools can accelerate reconnaissance, vulnerability research, and report writing in a penetration test, but they cannot replace verification or technical judgement. This guide explains where AI adds value, where it misleads, and the rules that keep reports defensible.
 Cybersecurity
GCTI vs XCTI
SANS FOR578 and GCTI are respected CTI credentials, but are they worth $7,000-$9,000 in 2026? This article compares GCTI and XCTI across cost, assessment quality, operational relevance, and what each certification actually proves.